Goby is a new generation network security assessment tool. It can efficiently and practically scan vulnerabilities while sorting out the most complete attack surface information for a target enterprise. Goby can also quickly penetrate the company intranet based on a company's vulnerabilities exposed to the Internet. We strive for Goby to become a more vital tool that can benchmark against hackers' actual attack methods and help companies effectively understand and respond to cyber-attacks.
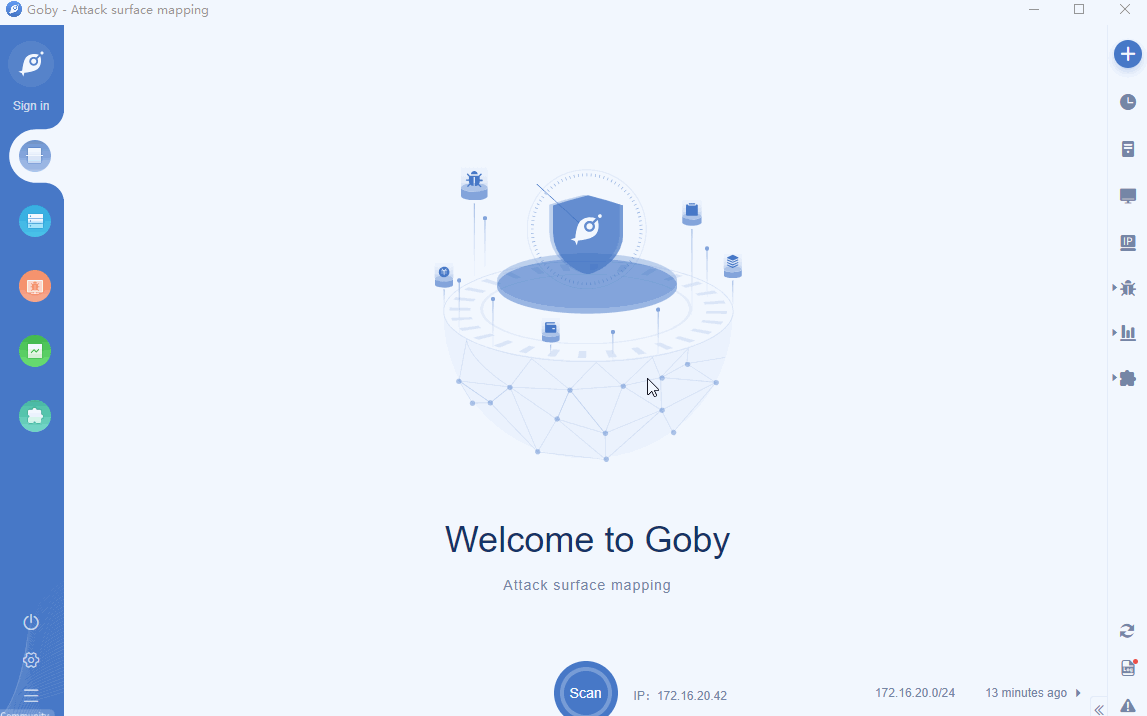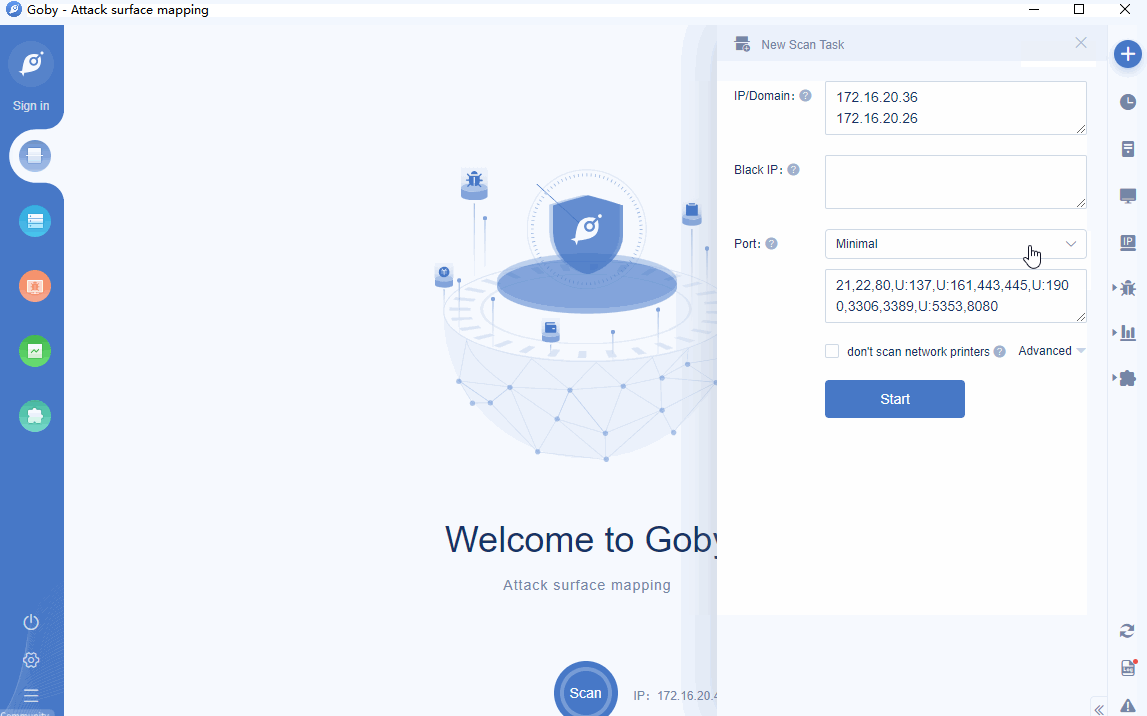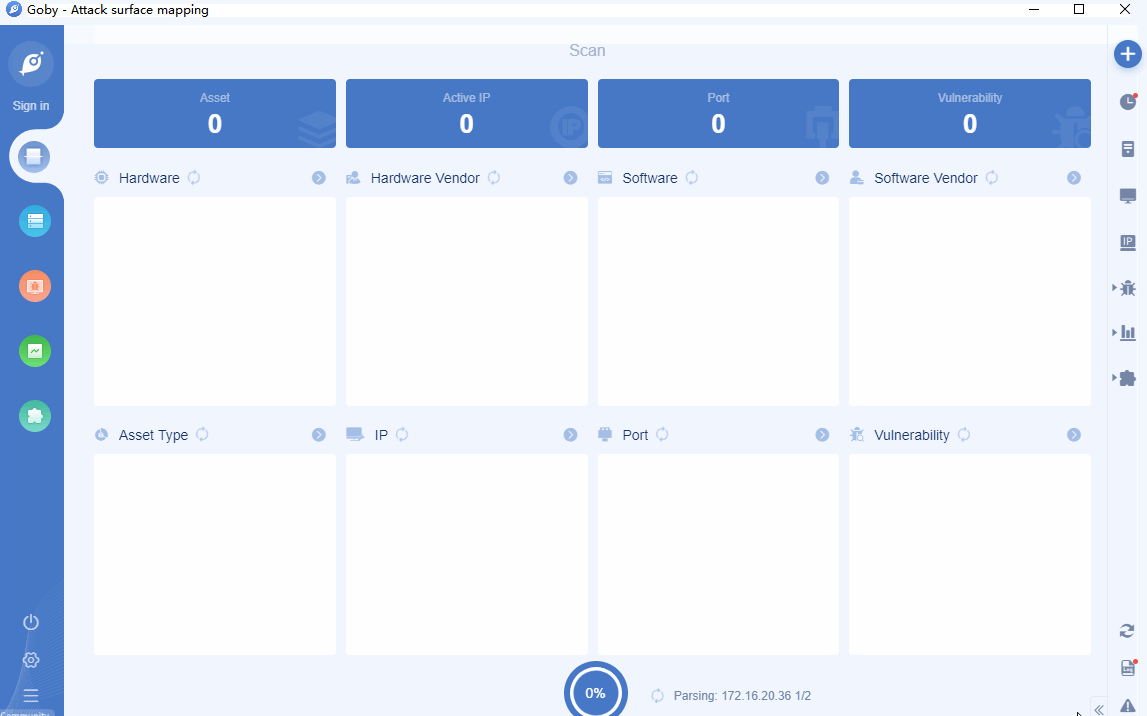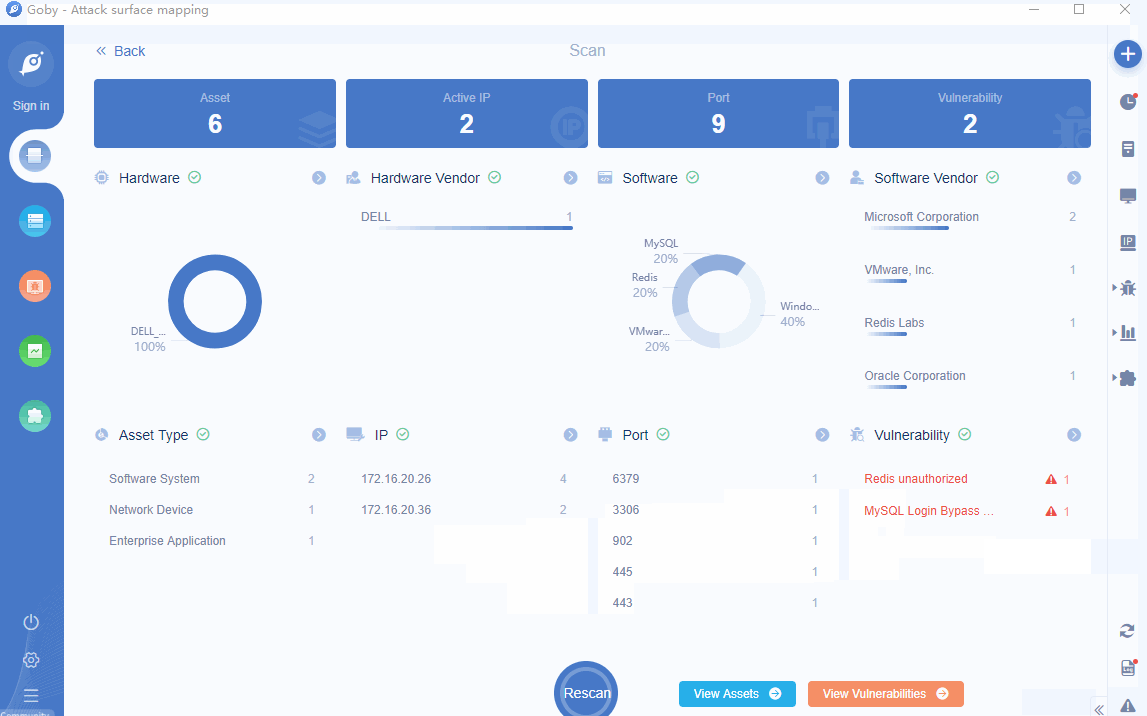
Goby currently uses Golang development, uses Electron and VUE as the front-end framework, supports windows, MacOS, and Linux without installation. Goby is based on network scanning, therefore permission is required to identify the NIC before using it.The installation methods of different platforms are as follows:
Npcap and install it.1. cd /dev
2. sudo chown $USER:admin bp*
For more information, see Goby WiKi
1. Rule bases
Goby has built in more than 100,000 rule recognition engines. The coverage of hardware types includes Network devices, IoT devices, Network Security products, office devices, etc. The coverage of software types includes: CRM,CMS,EMAIL,OA system, etc.
2. Protocol
Goby has built in more than 200 protocol recognition engines, including: Network protocols, Database protocols, IoT protocols , ICS protocols, etc.
3. Port
In addition to common ports, Goby also groups ports based on security practices, including: Enterprises, Cafes, Hotels, Airports, Databases, IoT, SCADA, ICS and Back door detection.
4. Common vulnerabilities and weak passwords
Goby covers common critical vulnerabilities such as Weblogic and Tomcat, as well as preset account information of more than 1,000 devices.
For more information about Goby FAQ, please visit here
Contribute POC
Please read here first if you submit an error or demand suggestion.
If you have a functional type of issue, you can raise an issue on GitHub or in the discussion group below:
169 followers · starred Jan 2022
13 followers · starred Sep 2024
Goby is a new generation network security assessment tool. It can efficiently and practically scan vulnerabilities while sorting out the most complete attack surface information for a target enterprise. Goby can also quickly penetrate the company intranet based on a company's vulnerabilities exposed to the Internet. We strive for Goby to become a more vital tool that can benchmark against hackers' actual attack methods and help companies effectively understand and respond to cyber-attacks.
Goby currently uses Golang development, uses Electron and VUE as the front-end framework, supports windows, MacOS, and Linux without installation. Goby is based on network scanning, therefore permission is required to identify the NIC before using it.The installation methods of different platforms are as follows:
Npcap and install it.1. cd /dev
2. sudo chown $USER:admin bp*
For more information, see Goby WiKi
1. Rule bases
Goby has built in more than 100,000 rule recognition engines. The coverage of hardware types includes Network devices, IoT devices, Network Security products, office devices, etc. The coverage of software types includes: CRM,CMS,EMAIL,OA system, etc.
2. Protocol
Goby has built in more than 200 protocol recognition engines, including: Network protocols, Database protocols, IoT protocols , ICS protocols, etc.
3. Port
In addition to common ports, Goby also groups ports based on security practices, including: Enterprises, Cafes, Hotels, Airports, Databases, IoT, SCADA, ICS and Back door detection.
4. Common vulnerabilities and weak passwords
Goby covers common critical vulnerabilities such as Weblogic and Tomcat, as well as preset account information of more than 1,000 devices.
For more information about Goby FAQ, please visit here
Contribute POC
Please read here first if you submit an error or demand suggestion.
If you have a functional type of issue, you can raise an issue on GitHub or in the discussion group below:
169 followers · starred Jan 2022
13 followers · starred Sep 2024



