Official repository vuls Scan: 15000+PoCs; 23 kinds of application password crack; 7000+Web fingerprints; 146 protocols and 90000+ rules Port scanning; Fuzz, HW, awesome BugBounty( ͡° ͜ʖ ͡°)...
See the codeREADME_中文 • Compile/Install/Run • Parameter Description • How to use • Scenario • POC List • Custom Scan • Best Practices

export PPSSWWDD=yourRootPswd
More references: config/doNmapScan.sh By default, naabu is used to complete port scanning -stats=true to view the scanning progress Can I not scan Ports?
noScan=true ./scan4all -l list.txt -v
# nmap result default noScan=true
./scan4all -l nmapRssuilt.xml -v

| TAG | COUNT | AUTHOR | COUNT | DIRECTORY | COUNT | SEVERITY | COUNT | TYPE | COUNT |
|---|---|---|---|---|---|---|---|---|---|
| cve | 1430 | daffainfo | 631 | cves | 1407 | info | 1474 | http | 3858 |
| panel | 655 | dhiyaneshdk | 584 | exposed-panels | 662 | high | 1009 | file | 76 |
| edb | 563 | pikpikcu | 329 | vulnerabilities | 509 | medium | 818 | network | 51 |
| lfi | 509 | pdteam | 269 | technologies | 282 | critical | 478 | dns | 17 |
| xss | 491 | geeknik | 187 | exposures | 275 | low | 225 | ||
| wordpress | 419 | dwisiswant0 | 169 | misconfiguration | 237 | unknown | 11 | ||
| exposure | 407 | 0x_akoko | 165 | token-spray | 230 | ||||
| cve2021 | 352 | princechaddha | 151 | workflows | 189 | ||||
| rce | 337 | ritikchaddha | 137 | default-logins | 103 | ||||
| wp-plugin | 316 | pussycat0x | 133 | file | 76 |
281 directories, 3922 files.
Support 7000+ web fingerprint scanning, identification:
Support 146 protocols and 90000+ rule port scanning
Fast HTTP sensitive file detection, can customize dictionary
Landing page detection
Supports multiple types of input - STDIN/HOST/IP/CIDR/URL/TXT
Supports multiple output types - JSON/TXT/CSV/STDOUT
Highly integratable: Configurable unified storage of results to Elasticsearch [strongly recommended]
Smart SSL Analysis:
Automatically identify the case of multiple IPs associated with a domain (DNS), and automatically scan the associated multiple IPs
Smart processing:
Automated supply chain identification, analysis and scanning
Link python3 <a href=https://github.com/hktalent/log4j-scan>log4j-scan
mkdir ~/MyWork/;cd ~/MyWork/;git clone https://github.com/hktalent/log4j-scan
Intelligently identify honeypots and skip Targets. This function is disabled by default. You can set EnableHoneyportDetection=true to enable
Highly customizable: allow to define your own dictionary through config/config.json configuration, or control more details, including but not limited to: nuclei, httpx, naabu, etc.
support HTTP Request Smuggling: CL-TE、TE-CL、TE-TE、CL_CL、BaseErr

Support via parameter Cookie='PHPSession=xxxx' ./scan4all -host xxxx.com, compatible with nuclei, httpx, go-poc, x-ray POC, filefuzz, http Smuggling
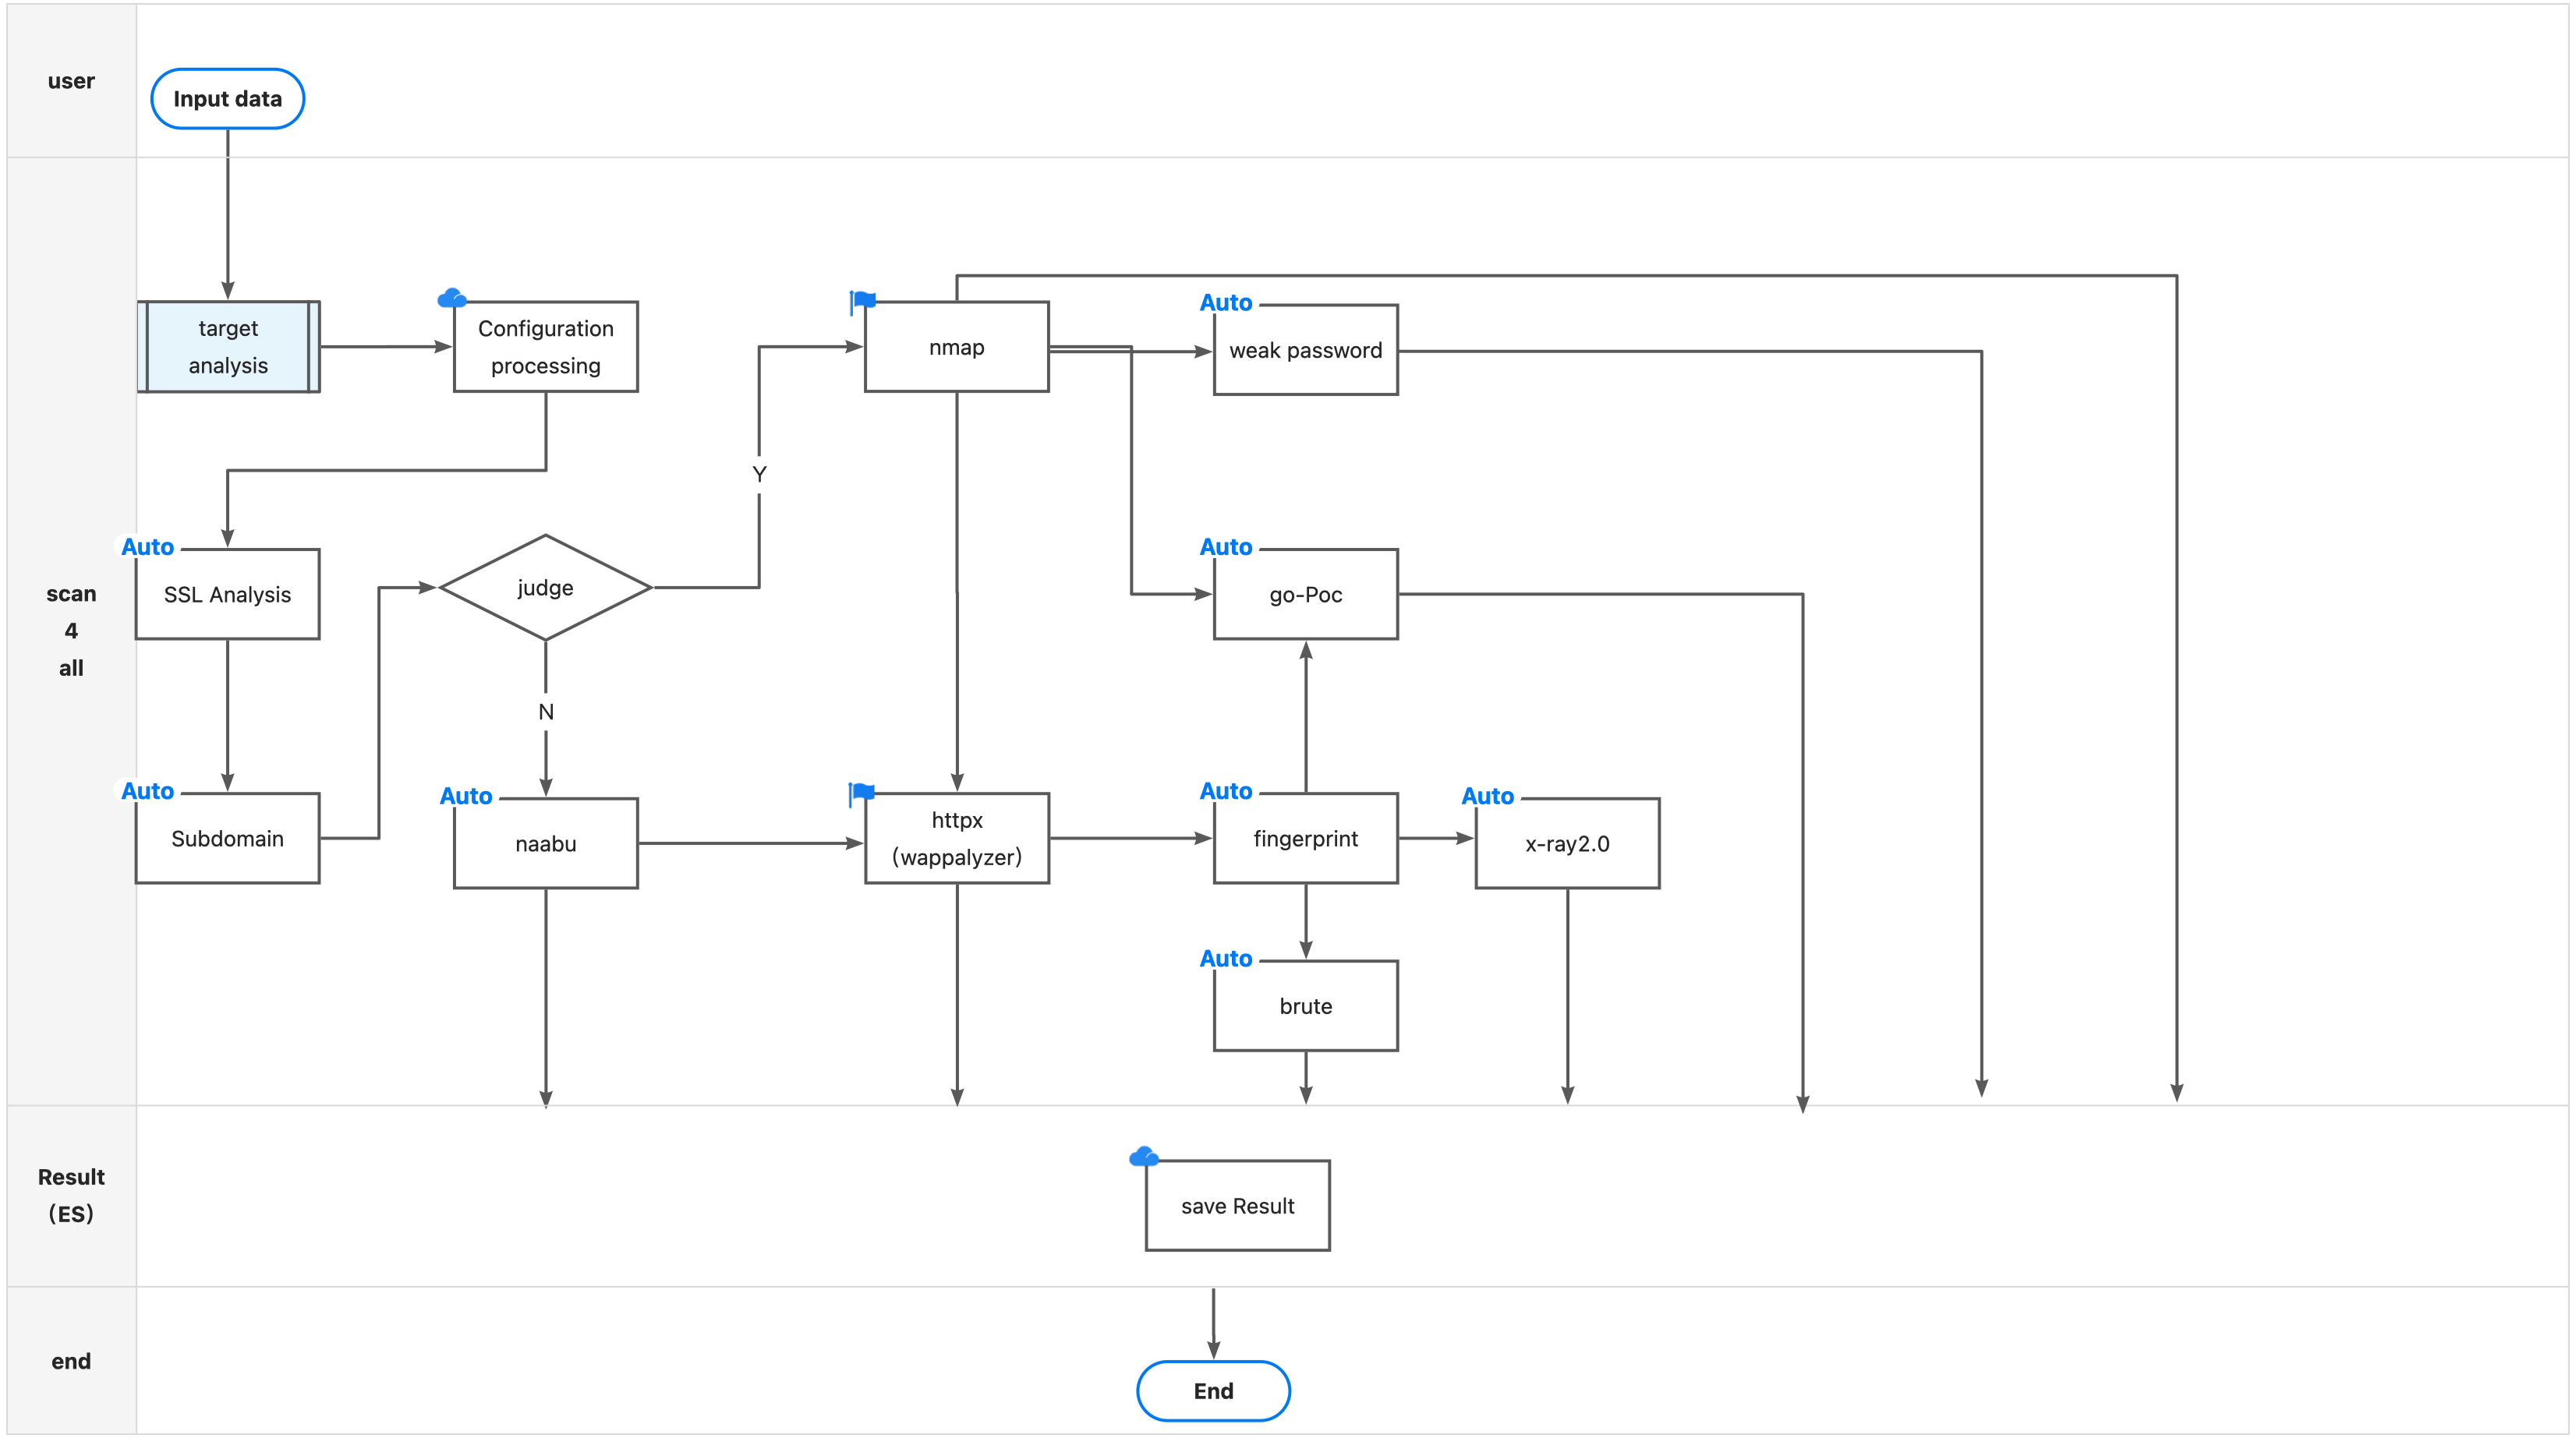
download from <a href=https://github.com/GhostTroops/scan4all/releases>Releases
go install github.com/GhostTroops/scan4all@2.8.9
scan4all -h
mkdir -p logs data
docker run --restart=always --ulimit nofile=65536:65536 -p 9200:9200 -p 9300:9300 -d --name es -v $PWD/logs:/usr/share/elasticsearch/logs -v $PWD /config/elasticsearch.yml:/usr/share/elasticsearch/config/elasticsearch.yml -v $PWD/config/jvm.options:/usr/share/elasticsearch/config/jvm.options -v $PWD/data:/ usr/share/elasticsearch/data hktalent/elasticsearch:7.16.2
# Initialize the es index, the result structure of each tool is different, and it is stored separately
./config/initEs.sh

# Search syntax, more query methods, learn Elasticsearch by yourself
http://127.0.0.1:9200/nmap_index/_doc/_search?q=_id:192.168.0.111
where 92.168.0.111 is the target to query
go build
# Precise scan szUrl list UrlPrecise=true
UrlPrecise=true ./scan4all -l xx.txt
# Disable adaptation to nmap and use naabu port to scan its internally defined http-related Ports
priorityNmap=false ./scan4all -tp http -list allOut.txt -v
more see: <a href=https://github.com/GhostTroops/scan4all/discussions>discussions
https://github.com/GhostTroops/scan4all/graphs/contributors
| Or | QQchat | Or | Tg | |
|---|---|---|---|---|
| <img width=166 src=https://github.com/hktalent/scan4all/blob/main/static/wcq.JPG> | <img width=166 src=https://github.com/hktalent/scan4all/blob/main/static/qqc.jpg> | <img width=166 src=https://github.com/hktalent/scan4all/blob/main/static/tg.jpg> |

| Wechat Pay | AliPay | Paypal | BTC Pay | BCH Pay |
|---|---|---|---|---|
| <img src=https://raw.githubusercontent.com/hktalent/myhktools/main/md/wc.png> | <img width=166 src=https://raw.githubusercontent.com/hktalent/myhktools/main/md/zfb.png> | paypal miracletalent@gmail.com | <img width=166 src=https://raw.githubusercontent.com/hktalent/myhktools/main/md/BTC.png> | <img width=166 src=https://raw.githubusercontent.com/hktalent/myhktools/main/md/BCH.jpg> |
370 followers · starred Sep 2023
258 followers · starred Nov 2022
174 followers · starred Oct 2024
319 followers · starred Jan 2026
Official repository vuls Scan: 15000+PoCs; 23 kinds of application password crack; 7000+Web fingerprints; 146 protocols and 90000+ rules Port scanning; Fuzz, HW, awesome BugBounty( ͡° ͜ʖ ͡°)...
See the codeREADME_中文 • Compile/Install/Run • Parameter Description • How to use • Scenario • POC List • Custom Scan • Best Practices
export PPSSWWDD=yourRootPswd
More references: config/doNmapScan.sh By default, naabu is used to complete port scanning -stats=true to view the scanning progress Can I not scan Ports?
noScan=true ./scan4all -l list.txt -v
# nmap result default noScan=true
./scan4all -l nmapRssuilt.xml -v
| TAG | COUNT | AUTHOR | COUNT | DIRECTORY | COUNT | SEVERITY | COUNT | TYPE | COUNT |
|---|---|---|---|---|---|---|---|---|---|
| cve | 1430 | daffainfo | 631 | cves | 1407 | info | 1474 | http | 3858 |
| panel | 655 | dhiyaneshdk | 584 | exposed-panels | 662 | high | 1009 | file | 76 |
| edb | 563 | pikpikcu | 329 | vulnerabilities | 509 | medium | 818 | network | 51 |
| lfi | 509 | pdteam | 269 | technologies | 282 | critical | 478 | dns | 17 |
| xss | 491 | geeknik | 187 | exposures | 275 | low | 225 | ||
| wordpress | 419 | dwisiswant0 | 169 | misconfiguration | 237 | unknown | 11 | ||
| exposure | 407 | 0x_akoko | 165 | token-spray | 230 | ||||
| cve2021 | 352 | princechaddha | 151 | workflows | 189 | ||||
| rce | 337 | ritikchaddha | 137 | default-logins | 103 | ||||
| wp-plugin | 316 | pussycat0x | 133 | file | 76 |
281 directories, 3922 files.
Support 7000+ web fingerprint scanning, identification:
Support 146 protocols and 90000+ rule port scanning
Fast HTTP sensitive file detection, can customize dictionary
Landing page detection
Supports multiple types of input - STDIN/HOST/IP/CIDR/URL/TXT
Supports multiple output types - JSON/TXT/CSV/STDOUT
Highly integratable: Configurable unified storage of results to Elasticsearch [strongly recommended]
Smart SSL Analysis:
Automatically identify the case of multiple IPs associated with a domain (DNS), and automatically scan the associated multiple IPs
Smart processing:
Automated supply chain identification, analysis and scanning
Link python3 <a href=https://github.com/hktalent/log4j-scan>log4j-scan
mkdir ~/MyWork/;cd ~/MyWork/;git clone https://github.com/hktalent/log4j-scan
Intelligently identify honeypots and skip Targets. This function is disabled by default. You can set EnableHoneyportDetection=true to enable
Highly customizable: allow to define your own dictionary through config/config.json configuration, or control more details, including but not limited to: nuclei, httpx, naabu, etc.
support HTTP Request Smuggling: CL-TE、TE-CL、TE-TE、CL_CL、BaseErr
Support via parameter Cookie='PHPSession=xxxx' ./scan4all -host xxxx.com, compatible with nuclei, httpx, go-poc, x-ray POC, filefuzz, http Smuggling
download from <a href=https://github.com/GhostTroops/scan4all/releases>Releases
go install github.com/GhostTroops/scan4all@2.8.9
scan4all -h
mkdir -p logs data
docker run --restart=always --ulimit nofile=65536:65536 -p 9200:9200 -p 9300:9300 -d --name es -v $PWD/logs:/usr/share/elasticsearch/logs -v $PWD /config/elasticsearch.yml:/usr/share/elasticsearch/config/elasticsearch.yml -v $PWD/config/jvm.options:/usr/share/elasticsearch/config/jvm.options -v $PWD/data:/ usr/share/elasticsearch/data hktalent/elasticsearch:7.16.2
# Initialize the es index, the result structure of each tool is different, and it is stored separately
./config/initEs.sh

# Search syntax, more query methods, learn Elasticsearch by yourself
http://127.0.0.1:9200/nmap_index/_doc/_search?q=_id:192.168.0.111
where 92.168.0.111 is the target to query
go build
# Precise scan szUrl list UrlPrecise=true
UrlPrecise=true ./scan4all -l xx.txt
# Disable adaptation to nmap and use naabu port to scan its internally defined http-related Ports
priorityNmap=false ./scan4all -tp http -list allOut.txt -v
more see: <a href=https://github.com/GhostTroops/scan4all/discussions>discussions
https://github.com/GhostTroops/scan4all/graphs/contributors
| Or | QQchat | Or | Tg | |
|---|---|---|---|---|
| <img width=166 src=https://github.com/hktalent/scan4all/blob/main/static/wcq.JPG> | <img width=166 src=https://github.com/hktalent/scan4all/blob/main/static/qqc.jpg> | <img width=166 src=https://github.com/hktalent/scan4all/blob/main/static/tg.jpg> |
| Wechat Pay | AliPay | Paypal | BTC Pay | BCH Pay |
|---|---|---|---|---|
| <img src=https://raw.githubusercontent.com/hktalent/myhktools/main/md/wc.png> | <img width=166 src=https://raw.githubusercontent.com/hktalent/myhktools/main/md/zfb.png> | paypal miracletalent@gmail.com | <img width=166 src=https://raw.githubusercontent.com/hktalent/myhktools/main/md/BTC.png> | <img width=166 src=https://raw.githubusercontent.com/hktalent/myhktools/main/md/BCH.jpg> |
370 followers · starred Sep 2023
258 followers · starred Nov 2022
174 followers · starred Oct 2024
319 followers · starred Jan 2026