Declarative node readiness for Kubernetes - gate scheduling with taints until node infrastructure (CNI, GPU, storage, custom checks) is actually ready.
See the code
A Kubernetes controller that provides fine-grained, declarative readiness for nodes. It ensures nodes only accept workloads when all required components eg: network agents, GPU drivers, storage drivers or custom health-checks, are fully ready on the node.
This project implements the proposed NodeReadinessGates API (KEP 5233) as an out-of-band solution and brings it to any Kubernetes cluster.
Use it to orchestrate complex bootstrap steps in your node-init workflow, enforce node health and improve workload reliability.
The Node Readiness Controller extends Kubernetes' node readiness model by allowing you to define additional pre-requisites for nodes (as readiness rules) in node conditions. It automatically manages node taints to prevent scheduling until all specified conditions are satisfied.
Kubernetes node has a simple "Ready" condition. Modern workloads need more critical infrastructure dependencies before they can run.
With this controller you can:
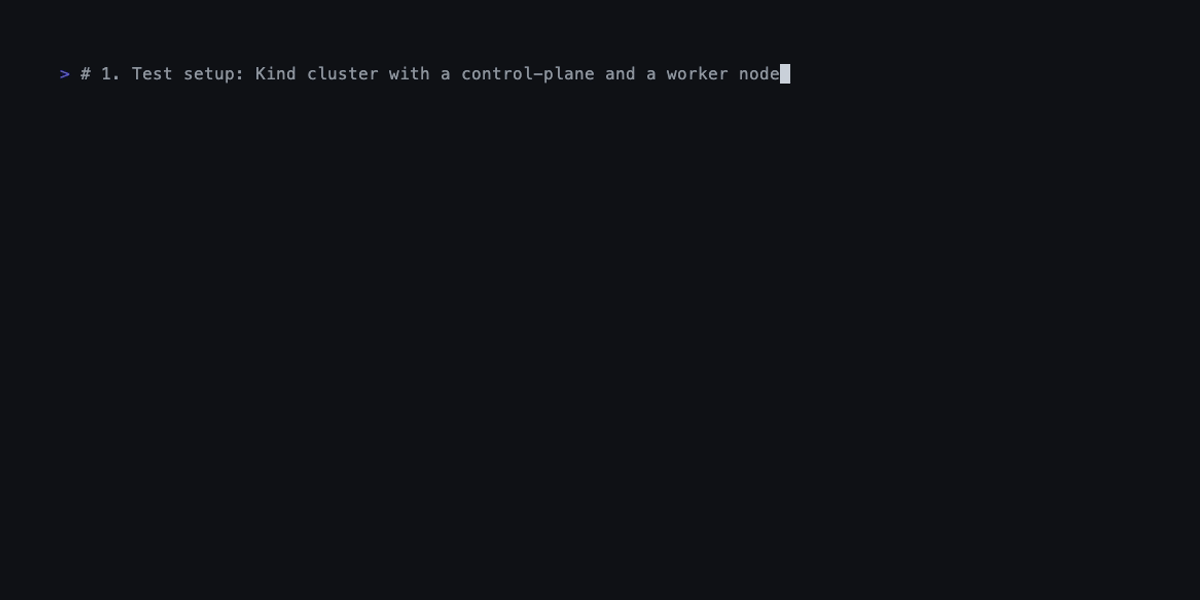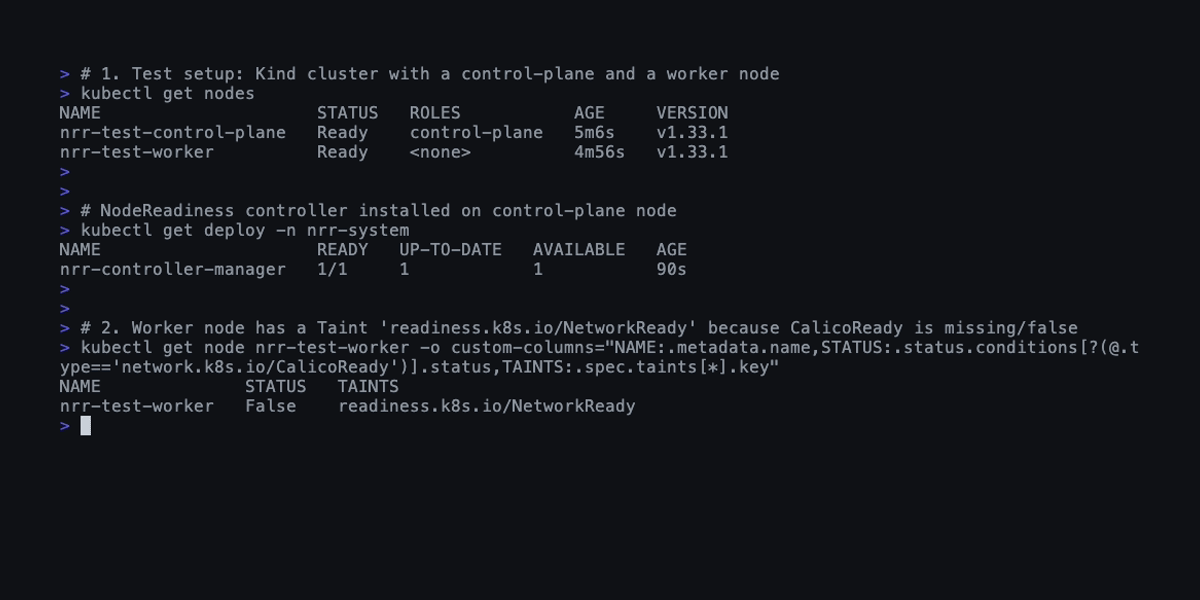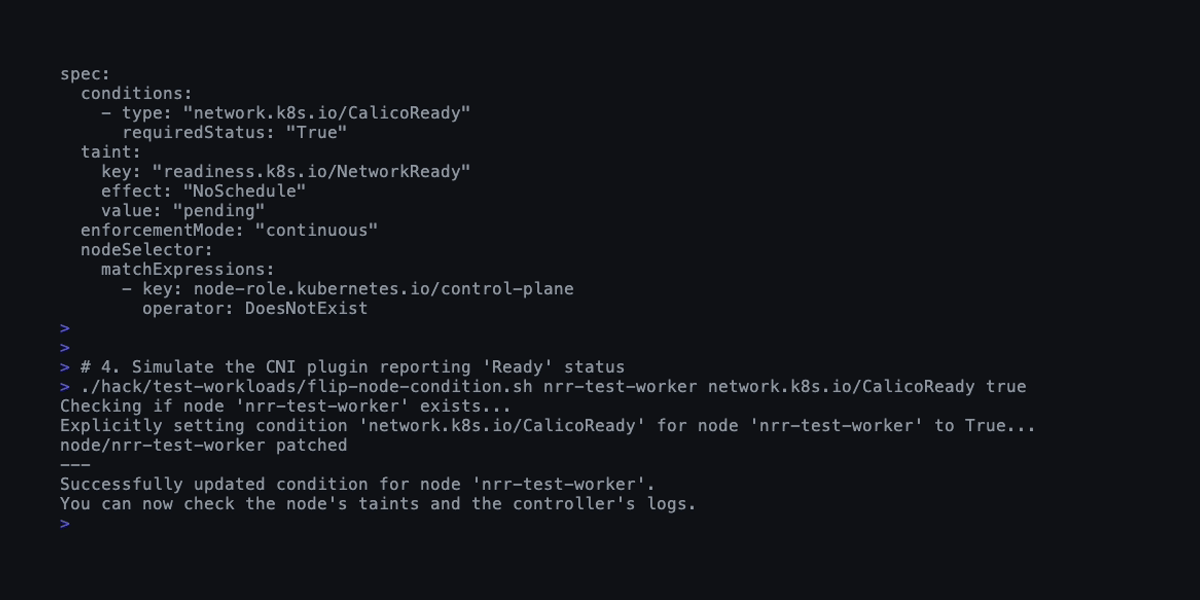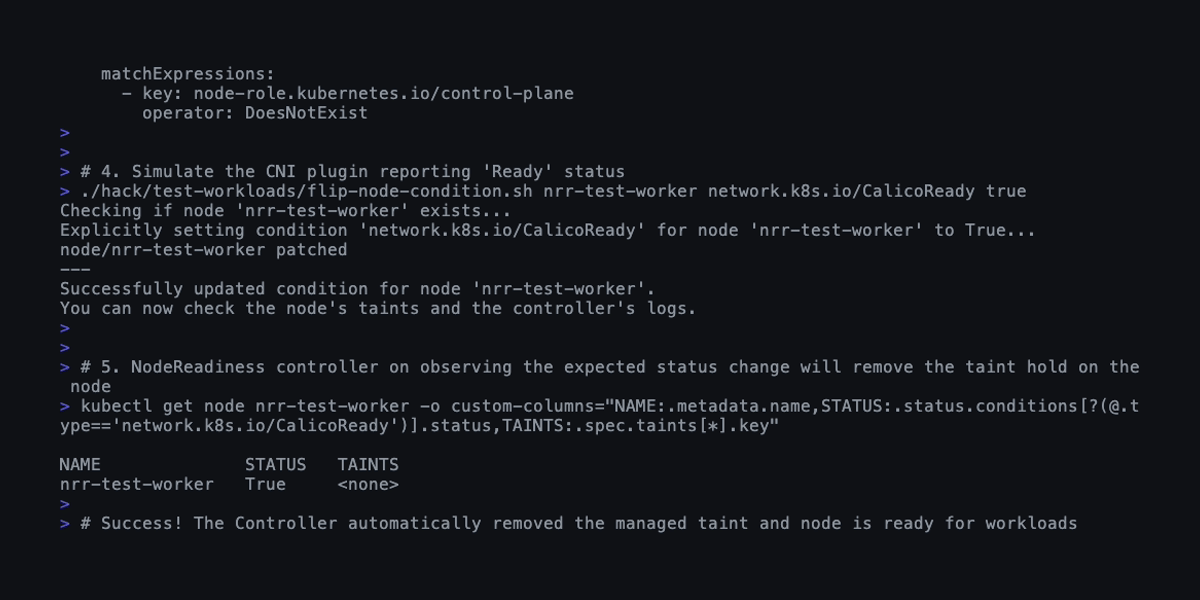
allOf or anyOf) to require ALL or ANY specified conditions to be satisfiedNode Readiness Controller in Kind cluster
Example Rule
apiVersion: readiness.node.x-k8s.io/v1alpha1
kind: NodeReadinessRule
metadata:
  name: network-readiness-rule
spec:
  conditions:
    - type: "example.com/CNIReady"
      requiredStatus: "True"
  taint:
    key: "readiness.k8s.io/NetworkReady"
    effect: "NoSchedule"
    value: "pending"
  enforcementMode: "bootstrap-only"
  nodeSelector:
    matchLabels:
      node-role.kubernetes.io/worker: ""
Find a more detailed walkthrough of setting up Node Readiness Controller in your Kind cluster here.
If you're interested in participating in future discussions or development related to Node Readiness Controller, you can reach the maintainers of the project at:
Open Issues / PRs / Discussions here:
See the Kubernetes community on the community page. You can also engage with SIG Node at #sig-node and mailing List
Participation in the Kubernetes community is governed by the Kubernetes Code of Conduct.
Latest release
Releases this year
602 followers · starred Jan 2026
835 followers · starred Nov 2025
244 followers · starred Nov 2025
347 followers · starred Aug 2026
Declarative node readiness for Kubernetes - gate scheduling with taints until node infrastructure (CNI, GPU, storage, custom checks) is actually ready.
See the code
A Kubernetes controller that provides fine-grained, declarative readiness for nodes. It ensures nodes only accept workloads when all required components eg: network agents, GPU drivers, storage drivers or custom health-checks, are fully ready on the node.
This project implements the proposed NodeReadinessGates API (KEP 5233) as an out-of-band solution and brings it to any Kubernetes cluster.
Use it to orchestrate complex bootstrap steps in your node-init workflow, enforce node health and improve workload reliability.
The Node Readiness Controller extends Kubernetes' node readiness model by allowing you to define additional pre-requisites for nodes (as readiness rules) in node conditions. It automatically manages node taints to prevent scheduling until all specified conditions are satisfied.
Kubernetes node has a simple "Ready" condition. Modern workloads need more critical infrastructure dependencies before they can run.
With this controller you can:
allOf or anyOf) to require ALL or ANY specified conditions to be satisfiedNode Readiness Controller in Kind cluster
Example Rule
apiVersion: readiness.node.x-k8s.io/v1alpha1
kind: NodeReadinessRule
metadata:
  name: network-readiness-rule
spec:
  conditions:
    - type: "example.com/CNIReady"
      requiredStatus: "True"
  taint:
    key: "readiness.k8s.io/NetworkReady"
    effect: "NoSchedule"
    value: "pending"
  enforcementMode: "bootstrap-only"
  nodeSelector:
    matchLabels:
      node-role.kubernetes.io/worker: ""
Find a more detailed walkthrough of setting up Node Readiness Controller in your Kind cluster here.
If you're interested in participating in future discussions or development related to Node Readiness Controller, you can reach the maintainers of the project at:
Open Issues / PRs / Discussions here:
See the Kubernetes community on the community page. You can also engage with SIG Node at #sig-node and mailing List
Participation in the Kubernetes community is governed by the Kubernetes Code of Conduct.
Latest release
Releases this year
602 followers · starred Jan 2026
835 followers · starred Nov 2025
244 followers · starred Nov 2025
347 followers · starred Aug 2026



