QQ Group: 653516618
A powerful multi-account management tool for Kiro IDE
Quick account switching, auto token refresh, group/tag management, machine ID management and more
English | 简体中文
📢 Sponsored Advertisement
Swiftproxy offers high-quality rotating and static residential proxies, with 90M+ residential IPs across 220+ locations worldwide. Supporting HTTP(S), SOCKS5, IP rotation, and sticky sessions, Swiftproxy provides flexible proxy solutions for Kiro account management, automation, and multi-account workflows.
💰 Rotating residential proxies starting at $0.7/GB
🎁 Exclusive Discount Code:
PROXY90— Get 10% OFF!
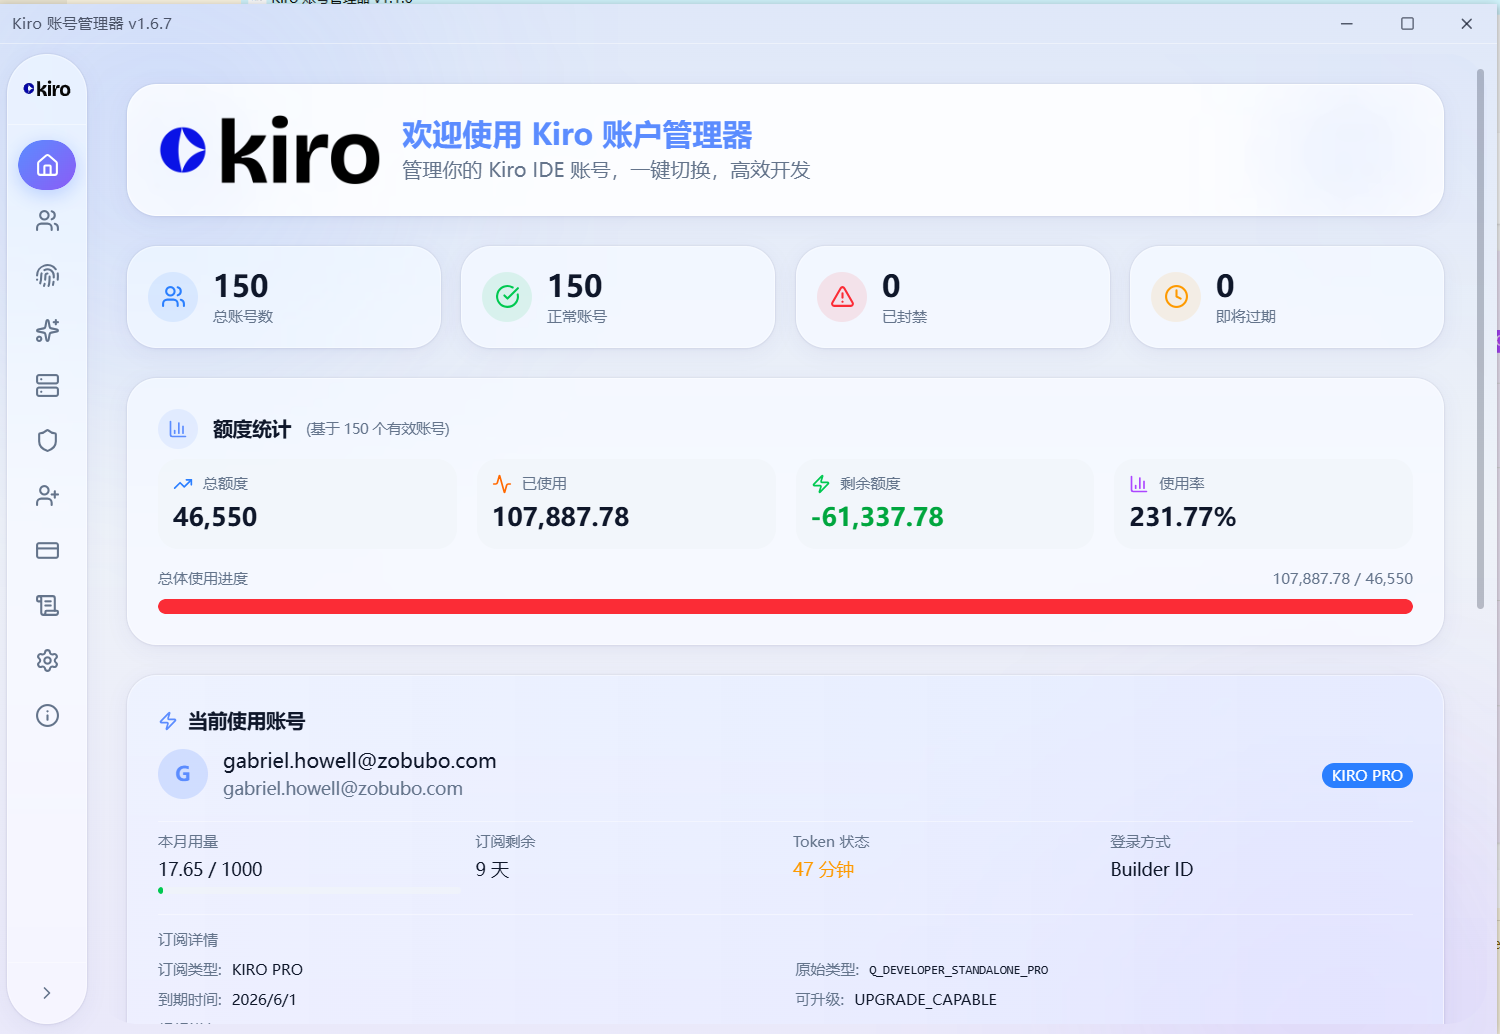
Shows account statistics, current account details, subscription info and quota breakdown.
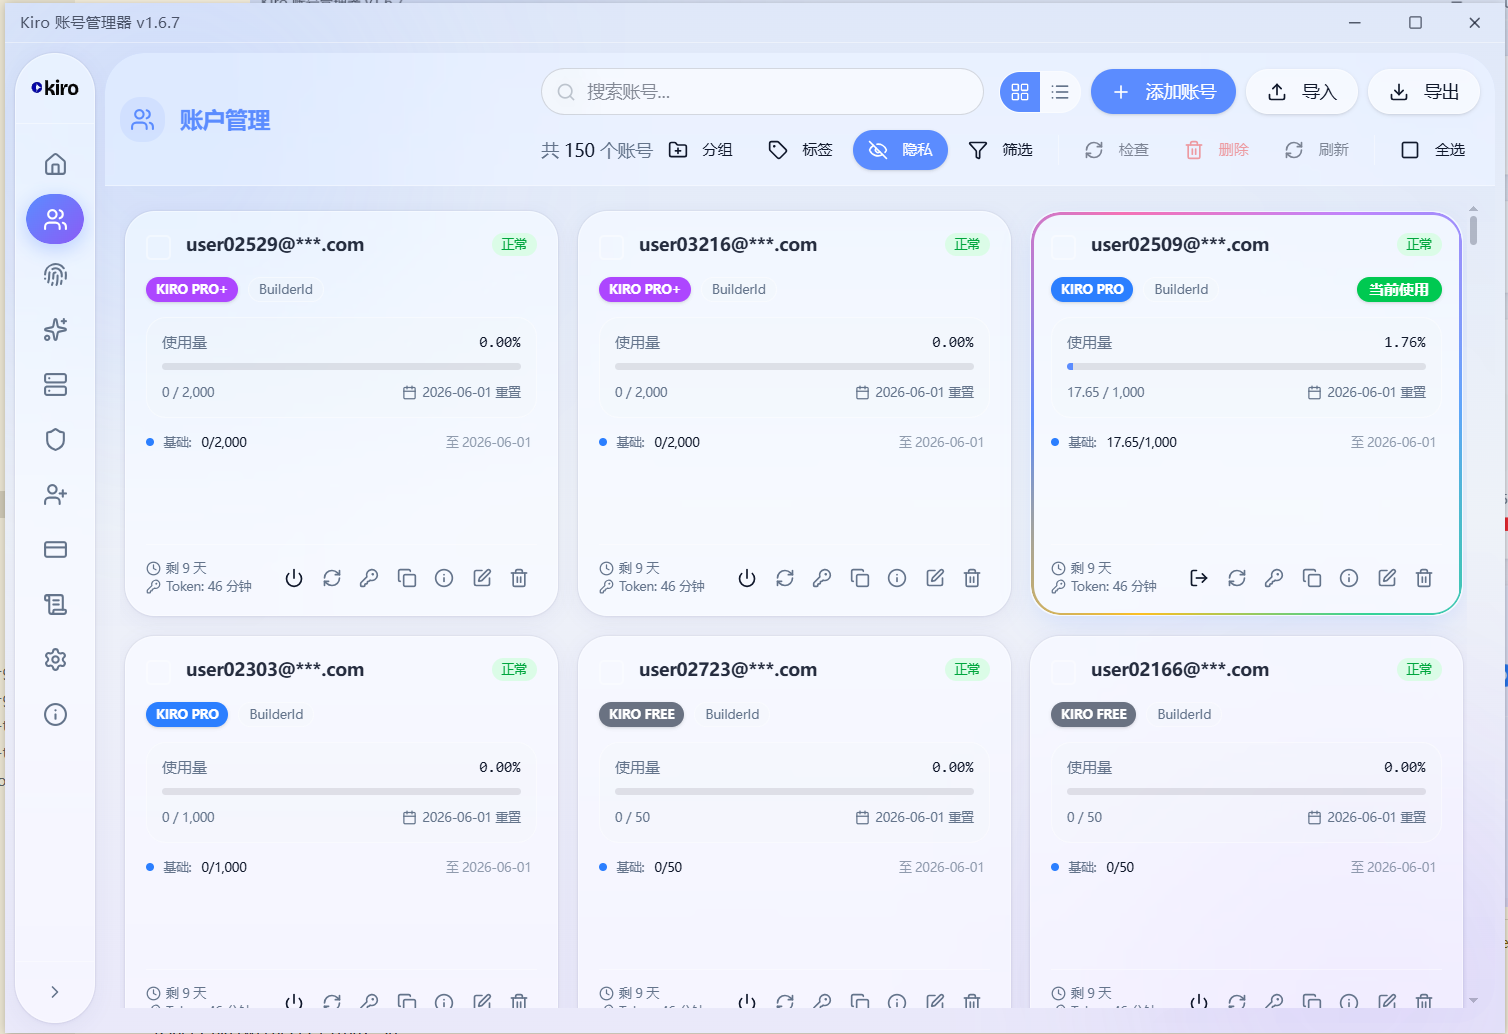
Manage all accounts, search, filter, batch operations, one-click switch.
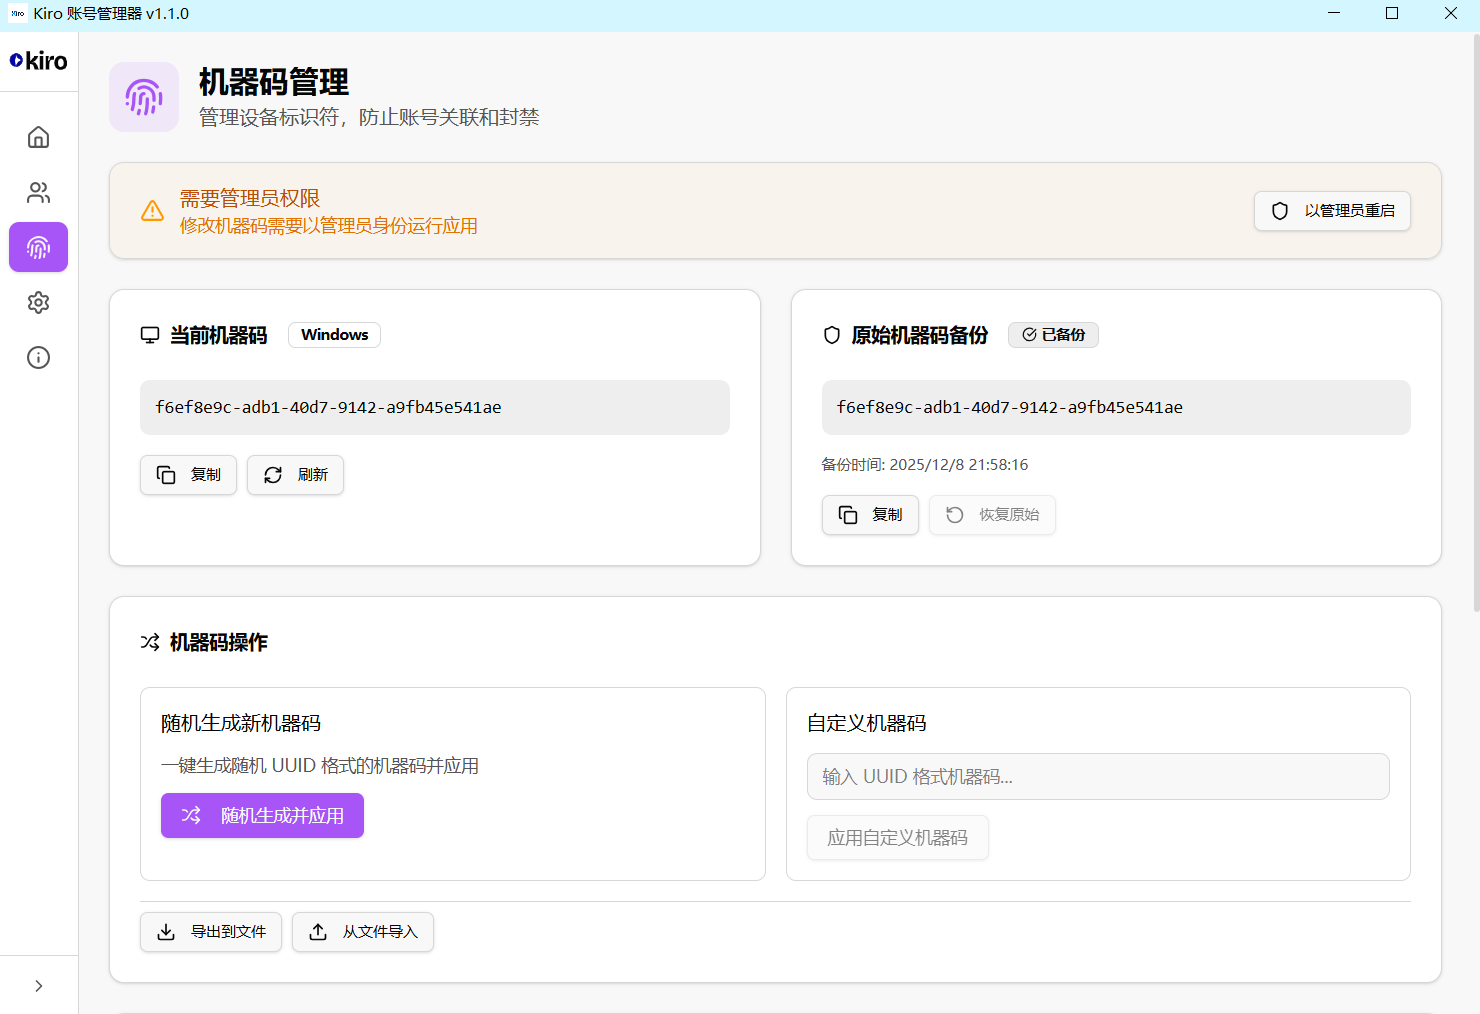
Manage device identifier, prevent account association bans, backup and restore.
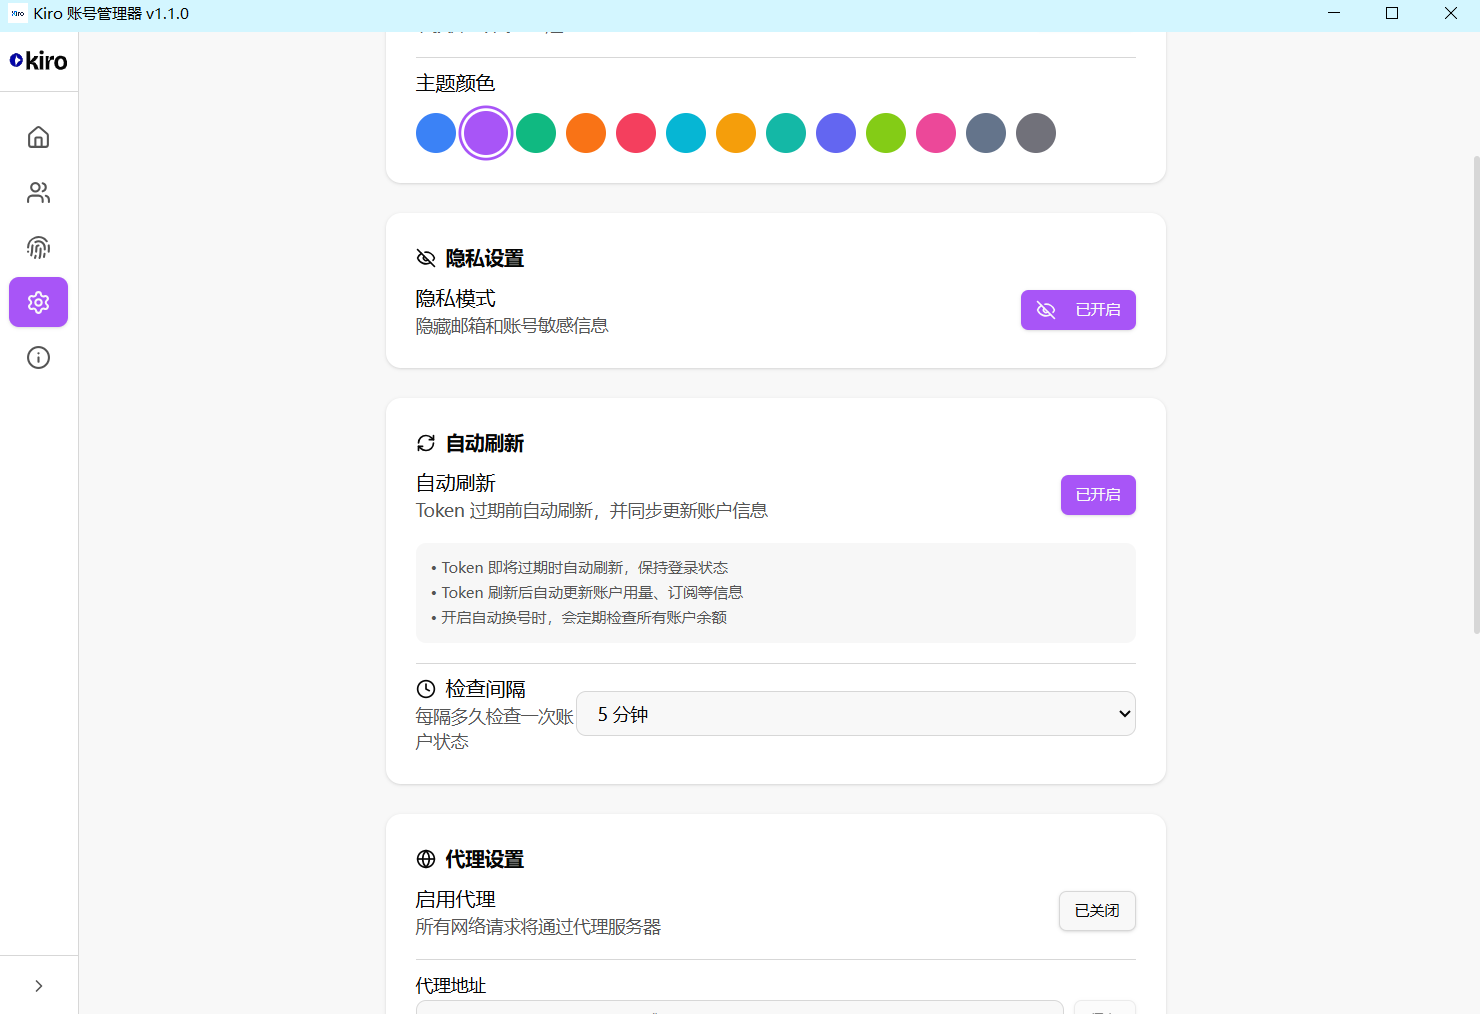
Configure theme colors, privacy mode, auto refresh, proxy and more.
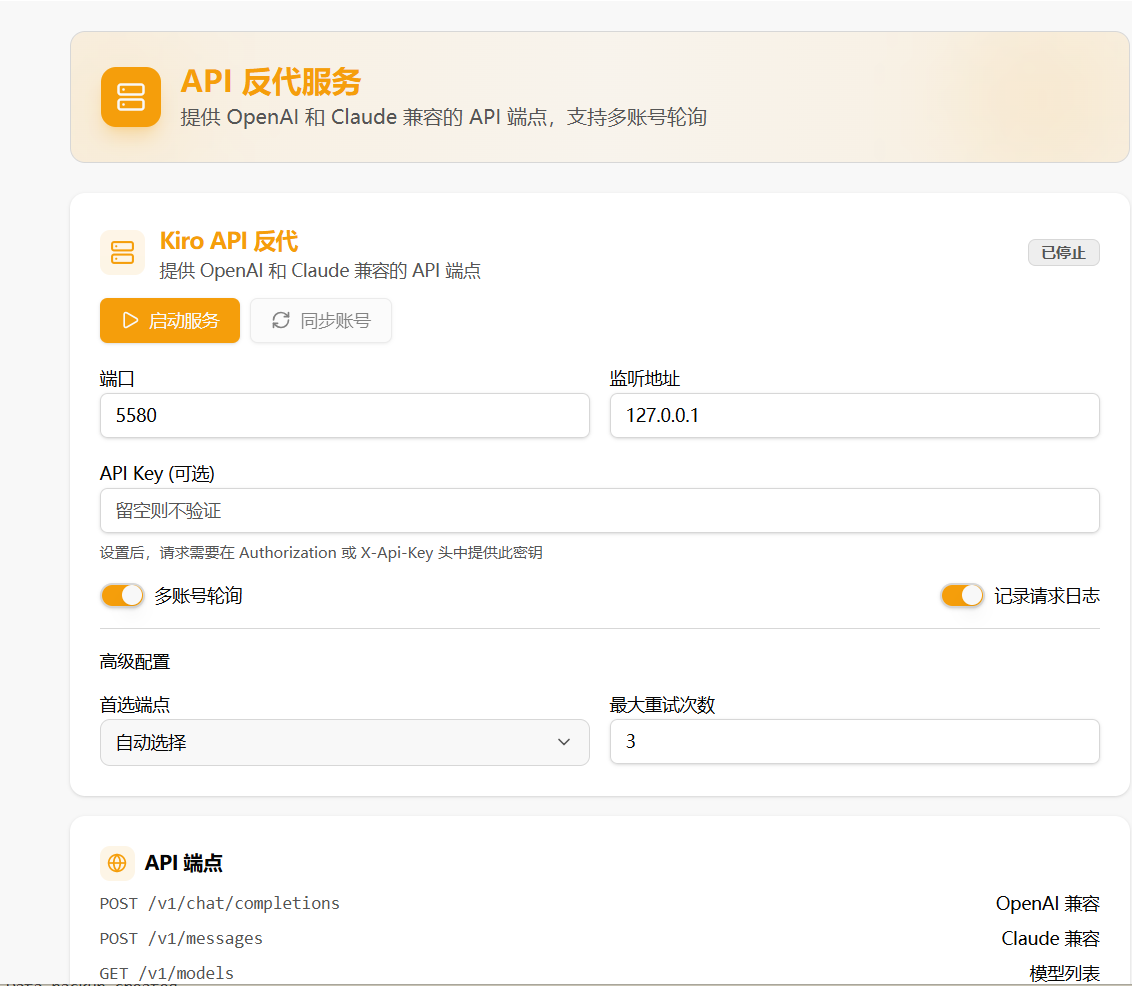
Provides OpenAI and Claude compatible API endpoints with multi-account rotation, auto token refresh, request retry and more.
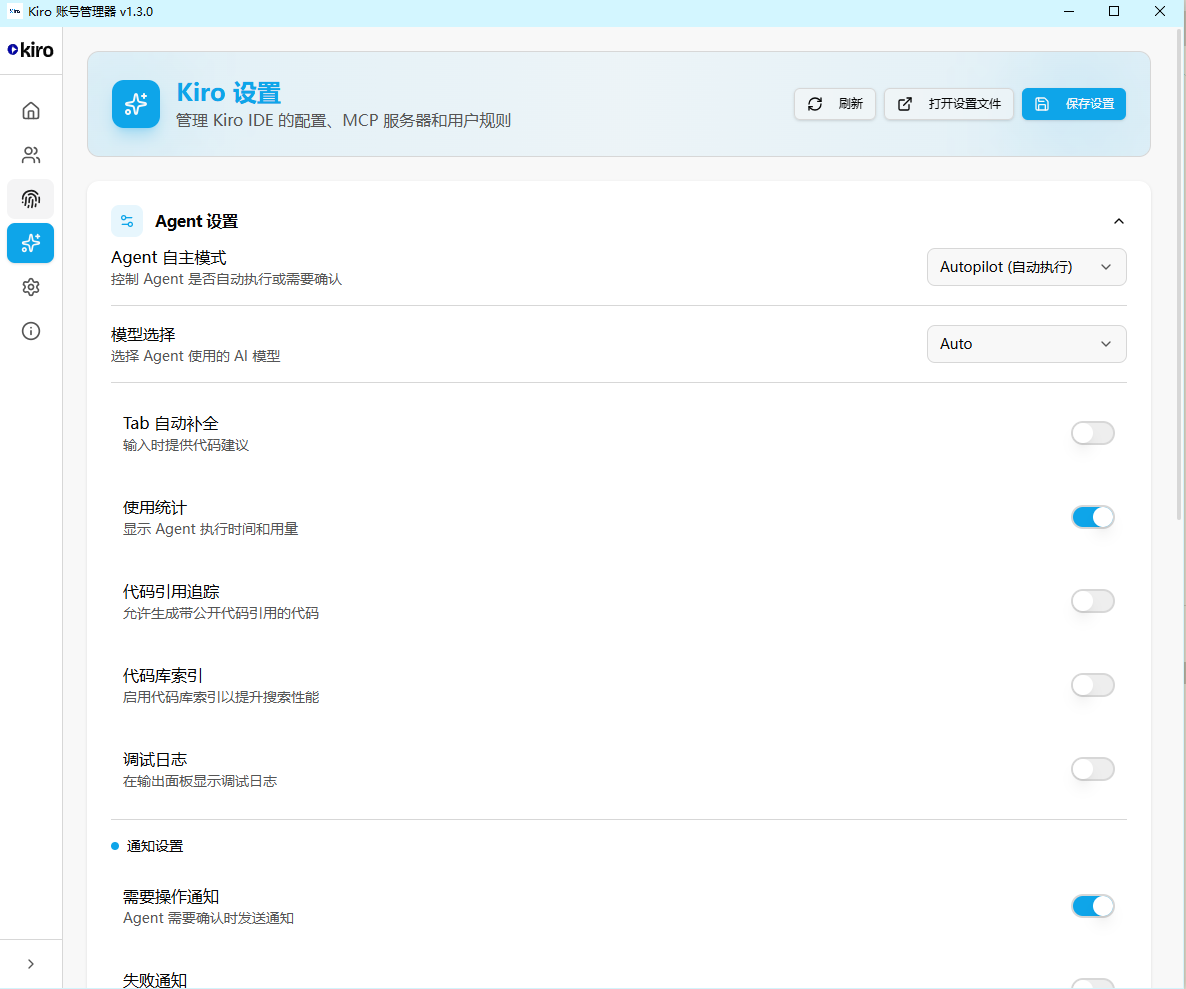
Sync Kiro IDE settings, edit MCP servers, manage user rules (Steering).
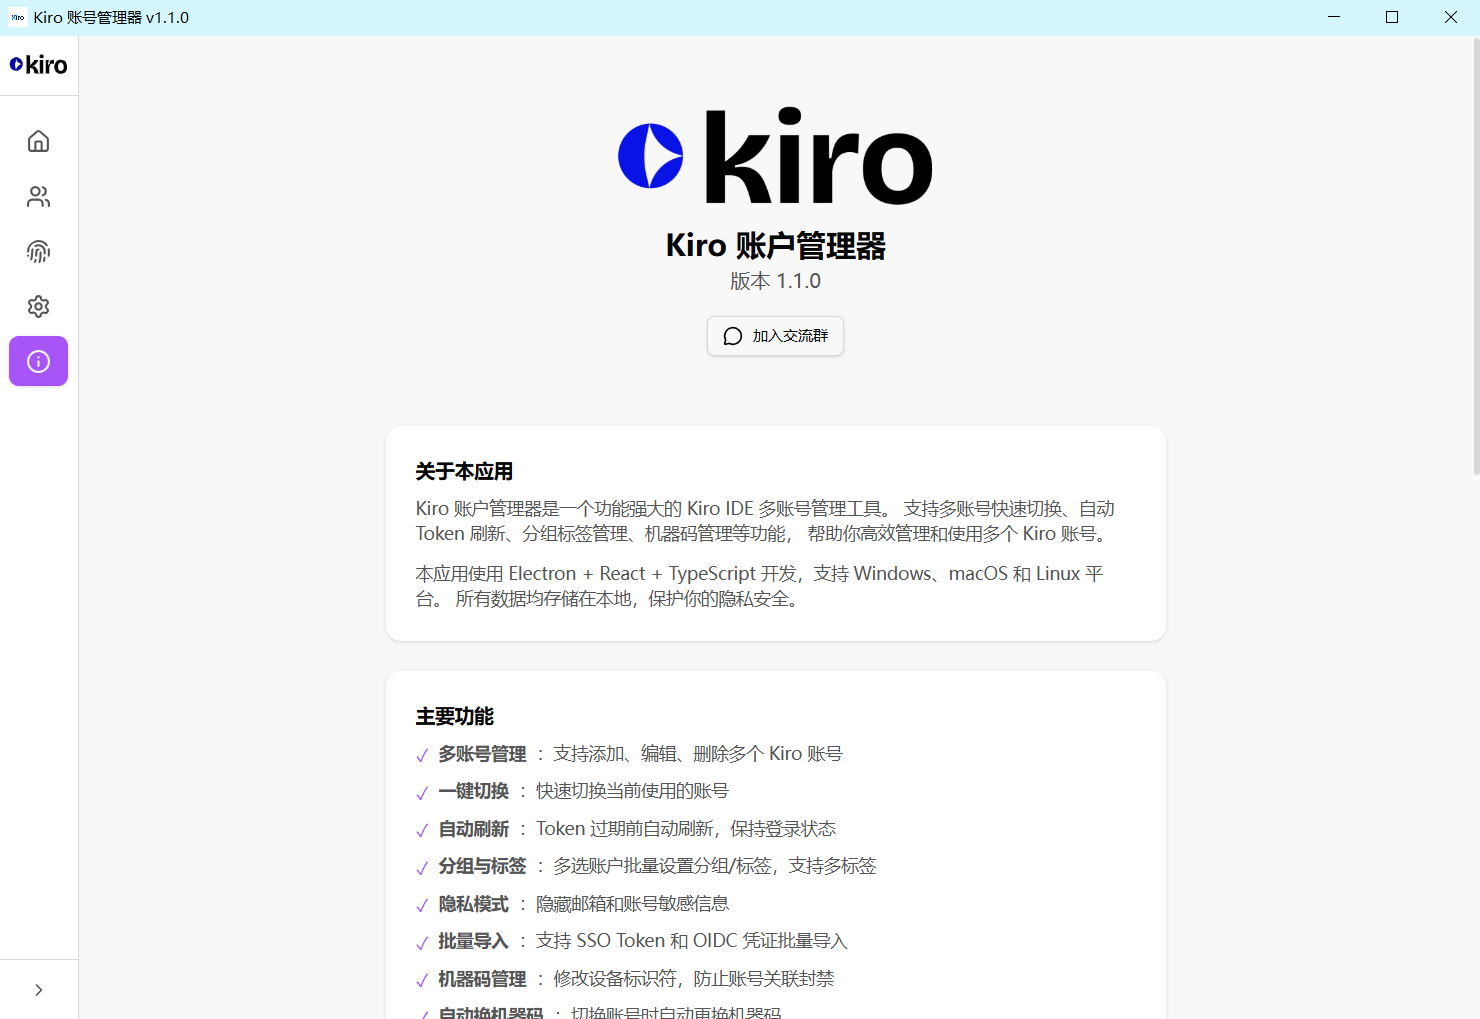
View version info, feature list, tech stack and author info.
Simply run the .exe installer.
Since the app is not code-signed by Apple, macOS will show "damaged and can't be opened" on first launch. Please follow these steps:
Method 1: Terminal Command (Recommended)
xattr -cr /Applications/Kiro\ Account\ Manager.app
Method 2: Right-click Open
Control and click the app (or right-click)chmod +x kiro-account-manager-*.AppImage
./kiro-account-manager-*.AppImage
dpkg -isnap install⚠️ Note: Modifying machine ID requires admin privileges, please run the app as administrator
npm install
npm run dev
# Windows
npm run build:win

# macOS
npm run build:mac

# Linux
npm run build:linux
# Windows 64-bit
npx electron-builder --win --x64

# Windows 32-bit
npx electron-builder --win --ia32

# Windows ARM64
npx electron-builder --win --arm64

# macOS Intel
npx electron-builder --mac --x64

# macOS Apple Silicon
npx electron-builder --mac --arm64

# Linux 64-bit
npx electron-builder --linux --x64

# Linux ARM64
npx electron-builder --linux --arm64
The project is configured with GitHub Actions workflow for auto building all platforms and architectures:
| Platform | Architecture | Format |
|---|---|---|
| Windows | x64, ia32, arm64 | exe, zip |
| macOS | x64, arm64 | dmg, zip |
| Linux | x64, arm64, armv7l | AppImage, deb, snap |
Push Tag: Auto build and release when pushing v* format tags
git tag v1.1.0
git push origin v1.1.0
Manual Trigger: Manually run workflow in GitHub Actions page
additionalModelRequestFieldsSchema from ListAvailableModels response to detect thinking capabilitythinking: {type, budget_tokens} and reasoning_effort to Kiro's additionalModelRequestFields (supports both output_config and reasoning schema paths)/v1/messages thinking: {type:"enabled", budget_tokens} to corresponding effort levels (low/medium/high/xhigh)reasoning_content field in OpenAI format, thinking content blocks in Claude formatTHINKING_SIGNATURE_INVALID error auto-retry — strips reasoningContent from history and retries (signature invalidation due to model updates)profileArn via POST codewhisperer.{region}.amazonaws.com/ListAvailableProfilesarn:aws:codewhisperer:{region}:610548660232:profile/VNECVYCYYAWN used when auto-fetch failssetProfileArnPersistCallback module-level callback — self-healed profileArn writes back to account pool + renderer store + memory snapshotonProxyAccountUpdate IPC event — renderer listens and persists profileArn to both top-level and credentials.profileArnProxyPanel and lazy-sync now read acc.profileArn || acc.credentials?.profileArnrefresh-account-token and verify-account-credentials now auto-fetch profileArn for ALL account types (not just Enterprise)refreshAccountToken store action now saves returned profileArn to both top-level and credentials<tool_use id="...">...</tool_use> XML as text content (in assistantResponseEvent / codeEvent) alongside structured toolUseEvent — these are now stripped from text output, preventing raw XML tags from appearing in client responsesx-amzn-kiro-agent-mode header sent to Kiro backend.kiro/steering/*.md rule filesalways-type steering documents are automatically injected into every request's system prompt (supports YAML frontmatter with inclusion: always/fileMatch/manual)ContextUsageEvent breakdown (Conversation / MCP tools / Steering files) from Kiro backend stream responsessteeringLoader.ts module — reads, parses frontmatter, and formats steering files for prompt injectionresolveProfileArnForWrite returned BuilderId placeholder ARN for Enterprise accounts when switching to IDE — IDE then used this invalid ARN causing "Invalid token" error. Now returns region-aware Enterprise fallback ARNresolveProfileArnForWrite now pass region parameter for correct Enterprise ARN generationresolveProfileArnForWrite to return placeholder ARN for BuilderId — Kiro IDE internal logic depends on this field existing; removing it caused IDE malfunctionListAvailableModels, ListAvailableSubscriptions, CreateSubscriptionToken, setUserPreference) now send placeholder ARN again (AWS 400 "profileArn must not be null")generateAssistantResponse / SendMessageStreaming) still do NOT send placeholder ARN (causes 403)migrateAccountDataIfNeeded cleanup of placeholder ARNs from account datasoftprops/action-gh-release@v1 uploading duplicate filenames causing 404 — replaced with find + cp flatten-and-dedup to release-assets/ directory before uploadyaml-language-server schema declaration to suppress IDE YAML lint false-positivesinputTokens, outputTokens, cacheReadTokens, reasoningTokens and other metric fields were incorrectly redacted as *** — removed overly broad 'token' matching rule, added SAFE_KEYS whitelistRegistrar.destroy() did not call abort(), causing destroyed registrars to continue executing async steps (e.g. sending OTP), leading to "no registration in progress" error when submitting verification codereadLine() had no timeout — when the server stalls mid-stream (network jitter / throttling / half-closed connection), the Promise hung forever, causing the mail-polling step to deadlock. Added 30s timeout with auto-reconnect on next retryThis release focuses on the core failure "after switching accounts / refreshing tokens in this app, Kiro IDE desktop gets force-logged-out ~1 hour later", closes the chain of bugs where BuilderId accounts still got written placeholder profileArn in multiple paths, adds an optional IDE Token proactive-renewal capability (off by default), fixes macOS auto-update 404, and ships a Kiro IDE binary patcher script plus several UI tweaks.
switch-account wrote the already-rotated/invalidated old refreshToken to disk — the old code only updated the local variable accessToken after calling OIDC for access_v2 + refresh_v2, but the refreshToken written into ~/.aws/sso/cache/kiro-auth-token.json was still v1 (immediately invalidated by BuilderId's rotating refresh-token mechanism). Kiro IDE's refresh loop later used v1 against OIDC → 401 → logoutAndForget() force-logoutrefresh-account-token ("Refresh Token" button) never wrote to disk at all — the old code only updated the in-app store and notified the renderer; the disk token file was untouched, so Kiro IDE never saw the new token. The UI showed "refreshed" but IDE actually kept using the old one and hit the same 401 → logout ~1h laterbackground-batch-refresh (the IPC used by "Auto Refresh") also never wrote to disk — the Auto Refresh feature (default every 5 minutes) refreshed all accounts but never synced to the IDE disk file. This was the biggest hidden hole after the switch/refresh-button fixes. Now every refreshed account, if recognized as the IDE current active account, is auto-syncedswitch-account hardcoded expiresAt = Date.now() + 3600*1000; now uses the real expiresIn returned by OIDCswitch-account previously still wrote the old token on OIDC refresh failure (planting a landmine); now it errors out without writing and surfaces a clear messagesrc/main/kiroAuthSync.ts and Bidirectional SyncwriteKiroAuthTokenFile / readKiroAuthTokenFile shared helpers — uniformly read/write ~/.aws/sso/cache/kiro-auth-token.json in a fully Kiro-IDE-compatible format (mode 0o600 etc.); social / IdC field ordering matches the IDE source serializerparseAccessTokenClaims — decodes the JWT body of an access token for sub / email / aud, used during reverse sync to identify "which account did the IDE just self-refresh"watchKiroAuthTokenFile — uses fs.watchFile with content-level debouncing; hooked up on app startlastSwitchedAccountId / refreshToken equality) finds the account in store → updates credentials → webContents.send('kiro-ide-token-changed') triggers renderer to loadFromStorage, UI immediately shows latest expiresAtlastWrittenTokenSignature (the token written by this app itself) is recognized by the watcher and skipped, preventing ping-pong between IDE and the appswitchAccount IPC returns refreshedCredentials (the real post-refresh access/refresh/expiresIn); the renderer immediately syncs to store, eliminating the cascading bug "store still holds v1 → next refresh hits invalidated refresh"FixedProfileArns hardcodes the placeholder ARN profile/AAAACCCCXXXX for BuilderId — calling codewhisperer.us-east-1.amazonaws.com/ListAvailableModels with this ARN deterministically triggers 403 "User is not authorized to make this call." The reverse-proxy side kiroApi.ts's resolveProfileArn now returns no profileArn for BuilderId and unknown providers; all call sites (fetchKiroModels / callKiroApiStream / 3 subscription endpoints) guard with null-checksswitch-account / switch-account-cli / refresh-account-token sync branch / runProactiveRenewal) still inlined the placeholder ARN — BuilderId accounts were force-stamped this placeholder into ~/.aws/sso/cache/kiro-auth-token.json or ~/.local/share/kiro-cli/data.sqlite3, planting the same landmine for Kiro IDE / kiro-cli REST calls. All paths now use the unified resolveProfileArnForWrite helper, which always returns undefined for BuilderIdkiroAuthSync.ts centrally hosts KIRO_BUILDER_ID_PLACEHOLDER_ARN / KIRO_SOCIAL_PROFILE_ARN; reverse-proxy kiroApi.ts becomes a re-exporter, eliminating drift risk across 5 duplicated constantswriteKiroAuthTokenFile — if a placeholder ARN is detected in input, it is automatically stripped to undefined, catching anything that bypassed the helpermigrateAccountDataIfNeeded performs a one-time scan of account data in electron-store, clearing placeholder ARNs written by older versions / Kiro IDE itself, then writes back idempotentlyattemptRefreshIfCloseToExpiry never fires, completely eliminating any race against OIDC rotationswitch-account / refresh-account-token / logout-account all schedule or clear the timer correctly with zero leaksproactiveRenewalEnabled key) and auto-restored after restarting the appscripts/patch-kiro-ide.cjsextension.js and the bundled JS under packages/kiro-shared:
getFixedProfileArn: short-circuit void 0 for BuilderIdsupportsProfiles: remove BuilderId from the IdC listresolveProfileArn: return void 0 directly for BuilderId tokens%APPDATA%/Kiro/User/globalStorage/kiro.kiro-agent/profile.json.kpatch-backup) + flags: --dry-run / --restore / --verbose / --kiro-dir; re-run the same command after Kiro IDE upgrades to re-patchnode scripts/patch-kiro-ide.cjs --dry-run for preview; node scripts/patch-kiro-ide.cjs to apply. Fully quit Kiro before runningelectron-builder replaces spaces in productName with . for the mac zip filename (yielding Kiro.Account.Manager-1.7.2-mac.zip), but the url field in latest-mac.yml replaces spaces with - (pointing at Kiro-Account-Manager-1.7.2-mac.zip). The mismatch caused updater 404. electron-builder.yml now sets mac.artifactName: ${name}-${version}-${arch}-mac.${ext} and explicit target: zip/dmg × [x64, arm64], unifying naming to kiro-account-manager-… across platforms and making latest-mac.yml include both x64 and arm64 entries so Apple Silicon users get a native arm64 buildRefreshCw icon and were visually indistinguishable; now respectively switched to Activity (check/activity semantic) and KeyRound (refresh-token semantic, consistent with the card view) with i18n tooltipsonKiroIdeTokenChanged IPC event — renderer subscribes and triggers loadFromStorage on receipt; the UI refreshes expiresAt instantly after IDE self-refreshnpm run typecheck:node && npm run typecheck:web both pass with zero errors--dry-run precisely targets all 5 candidate files on Windows D:\Program\Kiro (3 + 1 + 1 + 1 + 1 replacements)This release focuses on bulk import & quick-pick batched opening in the Subscription "Get Links" view, a boundary-character fix in card-key/credential parsing (resolving import-verification 401s), and assigning accounts to a chosen group when adding / batch-adding / importing.
-, it abuts the ---- separator forming 5+ consecutive -. The old split('----') consumed only the first 4, dropping ClientSecret's trailing - (corrupting the JWT) and turning provider into -BuilderId → authMethod mis-detected as social → refresh hit the wrong endpoint and returned 401splitCredentialLine — matches separators with /-{4,}/ and returns the extra (N-4) - to the previous field, keeping the JWT intact and provider correct; applied to OIDC batch import, TXT file card-key import, and Outlook mailbox parsingidp=BuilderId and ignored the 6th field — now reads the login method and infers from ClientId / Secret, consistent with the dialog batch-import logicgroupId: undefined, sending new accounts to "Ungrouped" forever — now they are categorized by the selected groupThis release focuses on Proton-based registration OTP auto-retrieval (accuracy + speed + log visibility), the Proton login-state & proxy experience, and card-key import/export fixes for GitHub/Google social-login accounts.
no-reply@signin.aws and reads the top two candidates, avoiding the "opened current mail but no code" deadlockprocess.env.HTTPS_PROXY) instead of the system proxy or the registration proxy pool; the session proxy is also refreshed on window reuse, so proxy changes take effect on the next retrievalprovider=BuilderId(IdC) on import, but social accounts have no ClientId / Secret and were rejected by the verify endpoint's authMethod !== 'social' && (!clientId || !clientSecret) guard ("please fill in Client ID and Client Secret")email----password----RefreshToken----ClientId----ClientSecret----loginMethod, so import can accurately restore social(Github/Google) / IdC(BuilderId/Enterprise)This release packs 70+ improvements covering reverse-proxy security hardening, batch registration concurrency isolation, SOCKS proxy support, unified task center, webhook notifications, analytics reporting, one-click diagnostics, config import/export, and major performance optimizations.
P0 Critical Security
readBody now enforces a max body size (default 10MB), rejects oversized Content-Length early + breaks connection on stream overflow → HTTP 413 (DoS protection)host=0.0.0.0/:: without any API Key; red banner in UI + explicit allowExternalWithoutApiKey flag required to bypasscrypto.timingSafeEqual to prevent timing-attack key guessing/admin/config GET masks apiKeys[].key plaintext, showing only xxxx***last4P1 Operations & Observability
/admin/config POST field allowlist, blocks remote mutation of port/host/apiKeys/tlsconversation_id to same account → preserve prompt cache + anti-risk-control)stop() (5s grace period → activeRequests.abort → socket.destroy)P2 Advanced
/metrics endpoint (8 core metrics: requests/tokens/credits/accounts/uptime)/admin/audit GET + enableAuditLog toggle)apiKeyAccountBindings: apiKey id → allowed account id array)fallbackPort simultaneously)recentRequests limit (default 100, max 10000)New files: src/main/proxy/selfSignedCert.ts, ProxySecurityPanel.tsx
New IPC: proxySelfSignedCertInfo / proxySelfSignedCertRegenerate / proxyNeedsRestart / proxyRestart / proxyAuditLog / onProxyWebhookTrigger
socks library + undici custom Agent + TLS upgrade)Concurrency Isolation Fixes
buildAutoConfig, weight rotation now actually works)resolvedProxyUrl() now includes system/env proxies)Feature Expansion
batchAutoImport and autoFetchProLink)useTaskStore, titlebar entry + drawer UI)I/O & Persistence
saveToStorage 500ms debounce + flushSaveImmediately force-flush APIcreateBackup 5-minute throttle (previously backed up on every save)ProxyLogStore async fs.promises.writeFile + 30s throttle + maxLogs 1M → 50Kproxy-account-suspended IPC updates memory snapshot only, deferred disk writequeueMicrotask async loading (no longer blocks loadFromStorage)Render & Compute
getFilteredAccounts / getStats / activeAccount module-level memoizationapplyBackgroundRefreshResults / applyBackgroundCheckResults batch merge (120ms buffer)importAccounts / importFromExportData single set callupdateTrayInfo 400ms debounceAccountToolbar selection status with useMemo + useCallback@tanstack/react-virtual, only render visible area)Invalid URL protocol (Windows registry ProxyServer multi-protocol string parsing, take only HTTP/HTTPS)tls-client-wrapper DLL moved to userData/tls-client/ for permanent storage (was in %TEMP%, could be cleaned by system)proxyServer.stop() socket force-destroy was too early, truncating responsesProxyPoolPage — Proxy pool management + advanced search + account binding + scheduled validationWebhooksPage — Webhook configuration + testing + event subscriptionDiagnosePage — One-click diagnostics (network / API / email / proxy / custom)ConfigSyncPage — Config import/export + AES-GCM encryptionproxyUrl field (account-bound egress proxy)machineId field (account-bound device ID)maxRequestBodyBytes / allowedIPs / deniedIPs / allowExternalWithoutApiKey / rateLimitPerKeyPerMinute / sessionAffinityEnabled / keepAliveTimeoutMs / headersTimeoutMs / recentRequestsLimit / enableMetrics / apiKeyAccountBindings / fallbackPort / enableAuditLog / apiKeyGroupBindings(deprecated)
text-green-500/600 → text-success, text-red-500/600 → text-destructive, text-amber/orange-500/600 → text-warning, decorative bg-blue-50/... → bg-primary/[0.04~0.15]_helpers.ts getStatusBadgeClass status colors fully tokenized with auto dark mode support--card-solid CSS variable (light #FFFFFF / dark #1A2236) — dedicated opaque background for account cards.bg-solid-card utility class with dual-class selector (.glass-card.bg-solid-card) to override glass-card transparent background and disable backdrop-filterbg-card into account data area causing "tinted overlay" effectbg-card transparencygenerateRowGlowStyle single-tag case removes horizontal background gradient, keeping only left 3px color stripe; multi-tag keeps vertical gradient stripebox-shadow/background) causing no visual feedback — switched to absolutely positioned overlay layer (absolute inset-0 ring-2 ring-inset ring-primary/60 bg-primary/[0.08] z-10) isolated from inline stylering-2 ring-primary/60 + bg-primary/[0.08] + primary shadowuseAccountsStore added activeGroupTab state ('all' | 'ungrouped' | <groupId>) with localStorage persistence — replaces multi-select filter logicgetFilteredAccounts() filters by activeGroupTab first (mutually exclusive)<header> got relative z-20 to elevate stacking context (.glass-toolbar's backdrop-filter creates isolated z layer)size="icon" h-8 w-8), saving ~280px widthChevronDown, more restrainedbg-destructive/10 red as warningProPlanType type — Pro / Pro+ / Power, mapped to Kiro backend Q_DEVELOPER_STANDALONE_{PRO|PRO_PLUS|POWER} qSubscriptionTypefetchProSubscriptionUrl uses user-selected plan type instead of hardcoded PROaccountPool.isAccountAvailable only marks accounts unavailable when refreshToken is missing; expired accounts with refreshToken pass through to proxyServer.getAvailableAccount for refresh; refresh failures auto-isolated via markNeedsRefresh forming a closed loopProxyConfig added multiAccountSelectionMode: 'all' | 'groups' and multiAccountGroupIds: string[] fieldssyncAccounts filters accounts by selected groups in multi-account + groups modemultiAccountSelectionMode / multiAccountGroupIds / accountSelectionStrategy)icon-only h-7 w-7 moved to Label row right side<p> tags moved to Label title tooltip (saves 30-40% vertical space)col-span-3 row ([Auto-trim toggle 160px][Number input flex-1])flex-wrap to grid-cols-3, 3 toggles (auto-switch/log requests/stream events) on one rowsk-xxx dropdown h-6 clipped by Select's internal py-2 — used Tailwind arbitrary attribute selector [&>button]:h-7 [&>button]:py-0 [&>button]:px-2.5 to force overrideSettings2 icon + uppercase tracking-wider minimalizedAccountManager.tsx trailing extra } causing TypeScript syntax errorAccountFilter.tsx cleaned up unused groups destructuringtokenCounter.ts module — encapsulates js-tiktoken cl100k_base encoder and getModelContextLength function, unifying all token computation logictokenUsage real value > contextUsageEvent percentage reverse calculation (modelCtx × percentage / 100) > tiktoken precise count > character-based fallback (input 0.42, output 0.4)assistantResponseEvent / codeEvent text and apply tiktoken, no longer relying on character lengthgetModelContextLength 3-tier lookup chain — Kiro fetchKiroModels's real maxInputTokens cache first → fuzzy match (claude-sonnet-4.5 ↔ claude-sonnet-4-5-20251001) → keyword fallback (sonnet/haiku/opus/gpt-4 etc.)CodeEvent parsing support — fixes lost streaming code content on this endpointparseEventStream signature extended with modelId and payloadStr parameters for end-to-end model context propagation enabling contextUsage reverse calculationmodelContextWindowCache definition in kiroApi.ts; unified import and re-export from tokenCounter.ts for backward compatibilitytokenBufferReserve behavior change — v1.6.7 force-enabled 50K reserve; v1.6.8 makes it an opt-in toggle, off by default, default value lowered to 20K when enabledenableTokenBufferReserve standalone switch — new field in ProxyConfig, frontend UI adds inline Switch controltrimHistoryByTokens is completely skipped; CONTENT_LENGTH_EXCEEDS_THRESHOLD from Kiro backend is forwarded as-is to the clientmodel.maxInputTokens - tokenBufferReserve (200K → 180K, 1M → 980K, range 5K~150K)disable condition extended with !enableTokenBufferReserve — input auto-greys when switch off; all related controls locked while server is runningnormalizeProxyUrl utility — auto-normalizes user-input non-standard proxy URLs (e.g. http:127.0.0.1:7890 missing //, 127.0.0.1:7890 missing scheme, leading/trailing whitespace) into standard http://host:port formatHTTP_PROXY/HTTPS_PROXY/NO_PROXY), Electron session.setProxy, and frontend UI now consistently use the normalized URL, avoiding proxy failure or duplicate setupset-proxy returns normalizedUrl to frontend store, auto-writing back to UI input for visual confirmationProxyConfig fields, IPC proxyStart/proxyUpdateConfig type signatures, backend OpenAI handleOpenAIStream and Claude handleClaudeStream auto-continue branches)tool_calls / tool_use directly to client after completion; client decides what to do next, no more server-side "fake continue" recursive call pathclientDrivenToolExecution=true configuration; long unusedelectron-builder build error ENOENT: no such file or directory, rename 'electron.exe' -> 'kiro-account-manager.exe' — root cause was incomplete electron-v38.7.2-win32-x64.zip download from npmmirror corrupting the Electron binary; switched to BITS download from cdn.npmmirror.com/binaries/electron/ for full zipapp.js download triggers RangeError: init["status"] must be in the range of 200 to 599, inclusive. — tlsclientwrapper returned status=0/undefined on network errors, triggering new Response() validation exception. Switched to undici fetch for static resources to bypass tls-client and avoid polluting its global statefailed to build client out of request input: failed to modify existing client: no tls client for modification check when proxy enabled — app.js download failure polluted the tls-client DLL global state, causing subsequent SessionClient initialization to fail. Auto-resolved by the app.js undici fix abovesetProxy changed to async function — awaits normalized URL from IPC and writes back to store for display, preventing UI/effective value mismatch403 + reason:"TEMPORARILY_SUSPENDED"), AccountSuspendedException (CodeWhisperer), and 423 Locked responsesProxyAccount gains suspendedAt / suspendReason / suspendMessage fields to track long-term bans (distinct from temporary errorCount cooldown)AccountPool adds isSuspended / markSuspended / clearSuspended — suspended accounts are permanently skipped in isAccountAvailable until manually cleared or reset()onAccountSuspended event + IPC proxy-account-suspended — full bridge from proxy server → main → preload → renderer store → UIstore.accountData[id].lastError and status='error' — survives app restartisBannedAccountError across store/accounts.ts / AccountSelectDialog / AccountCard — all three now recognize temporarily_suspended / temporarily suspended / User ID is suspended patterns and display the ban bannerAccountCard ban-detail dialog now has a Reset Suspended button that calls IPC proxy-clear-account-suspended → clears accountPool suspended flag + wipes store.accountData[id].lastError + sets status='active'accountPool.addAccount previously always forced isAvailable=true, which would silently wipe out the suspended state if an account was re-added (e.g., after proxy-sync-accounts). Now addAccount respects the incoming suspendedAt field and preserves isAvailable=false, so suspended accounts re-added from persisted data stay correctly skipped.host was 127.0.0.1 (loopback only) and the UI "Public" toggle was disabled while the server was running, so users couldn't switch without stopping the servicehttp://localhost:5580 instead of http://0.0.0.0:5580 (the latter is not a valid client target); copy-address button uses the same human-readable formLAN devices use http://<this-machine-IP>:<port>#f4f7fb, primary #5B8CFF, violet accent #8B5CF6, success #22C55E, translucent white borders rgba(255,255,255,0.4).glass-card / .glass-card-strong / .glass-card-subtle / .glass-sidebar / .glass-toolbar utility classes with backdrop-filter: blur(24px) saturate(180%)rounded-3xl (24px), glass backdrop, framer-motion spring width animation, layoutId-based active pill morph (primary → violet gradient)<Card> now defaults to glass variant with rounded-2xl (24px), supports variant=glass/glass-strong/glass-subtle/solid/elevated and interactive prop for hover-lift animation (translateY -2px + enhanced shadow).page-hero class with consistent 24px rounded glass headerglass-toolbar (16px blur + subtle bg + border-bottom only)AnimatePresence + motion.div wraps page content with fade + 8px Y-axis spring transition on route change#0a0e1a background with glass surfaces tuned for low-light readabilityframer-motion ^11.x for declarative animationsmotion.div wrapper now uses h-full flex flex-col so child page's flex-1 overflow-auto works correctly<Card className="border-0 shadow-sm hover:shadow-md transition-shadow duration-200"> across HomePage / SettingsPage / AboutPage / RegisterPage / KiroSettingsPage / ProxyPanel replaced with hover-lift — default glass variant now fully visibleUpdateDialog / CloseConfirmDialog / AccountDetailDialog / ProxyDetailedLogsDialog) switched from bg-background rounded-xl border to glass-card-strong rounded-2xl + backdrop-blur overlayButton component reworked: rounded-xl default, transition-all 200ms, hover -translate-y-px + ring-color glow on default/destructive variants, new gradient variant (theme-aware gradient-bg-primary + breathe-glow animation), new cta size (h-12 rounded-2xl) for primary call-to-actions--gradient-from / --gradient-to pair (purple/emerald/orange/rose/cyan/amber/teal/indigo/lime/pink/slate/zinc/sky/violet/fuchsia/red/yellow/green/stone/neutral + default). Sidebar's motion.span layoutId="sidebar-active-pill" reads from CSS vars, so the active menu pill morphs through the selected theme's hue gradient (e.g., emerald theme → teal-green gradient instead of fixed blue→violet)gradient-bg-primary and gradient-border utility classes now use var(--gradient-from/-to) so all gradient buttons/borders follow theme selection automaticallymain container now has .page-surface (dual blue/violet radial blobs @ 18% / 14% opacity, 60px blur) so glass cards have actual color to refract through — previously cards looked solid white on solid white backgroundborder + hover:shadow-lg overrides that were stomping the glass system; now uses hover-lift utility (translateY -2px + enhanced shadow) on non-active/non-banned cards; active glow border and banned red border preservedbg-[var(--glass-bg-subtle)] backdrop-blur-md with rounded-xl + larger focus ring; filter panel number inputs (AccountFilter) same treatmentlocalStorage('accounts_viewMode'). Compact list rows show inline email + status + subscription + tags + credit progress + key actions, with ~5x density vs cards (good for managing 100+ accounts)displayLimit default changed from All to 5K and now persists to localStorage('systemLogs_displayLimit') — previously the value reset to All on every page navigation/app restart, hurting initial render performance with large log volumestokenBufferReserve setting (replaces previous maxInputTokensThreshold) — adaptive history trimming based on the actual model's contextWindow returned by ListAvailableModelsmodel.maxInputTokens - tokenBufferReserve per request — default 50000 reserve fits all models (200K models → 150K cutoff, 1M models → 950K cutoff)system + tools + current message + output budget + estimation skew, preventing CONTENT_LENGTH_EXCEEDS_THRESHOLD on long conversations regardless of byte-based payload sizefetchKiroModels into the trimming logic so newly added Kiro models pick up correct limits automatically.glass-card-strong — rewritten as 90% translucent white (rgba(255,255,255,0.90) / dark rgba(20,25,40,0.90)) + backdrop-filter: blur(20px) saturate(160%) real frosted glass + 3-layer composite deep shadow (1px outer border + 0 24px 64px far shadow + 0 8px 24px near contact shadow) for strong elevationbg-black/40 backdrop-blur-sm / bg-black/50 to bg-slate-900/[0.12] dark:bg-black/50 backdrop-blur-xl — light-mode 12% slate ultra-faint mask + heavy blur (24px) so background blurs without graying out the dialog samplehover:bg-red-500 hover:text-white transition-colors, covering AccountDetailDialog / EditAccountDialog / AddAccountDialog / TagManageDialog / GroupManageDialog / ExportDialog / AccountCard ban+subscription / ApiKeyUsageDialog / AccountSelectDialog / UpdateDialog (15+ dialogs total), matching TitleBar close button for consistent danger semantics--glass-bg-strong token changed from opaque white to 90% translucent + backdrop-filter now actually applies, so dialogs are no longer flat opaque cards but true glass panels#f4f7fb → #EEF2F8 icy blue (inspired by F1 Fresh Blue), reducing the dead-white "AI palette" feel#0a0e1a → #0B1220 deep navy (inspired by E1 Deep Space), shifted from neutral gray-black to blue tone#E5EBF5 → #EEF2F8 → #F2F5FA simulating daylight transition; dark mode #0F1729 → #0B1220 → #060A14 for night-sky depthcolor-mix(in srgb, var(--gradient-from) 10%, ...) — switching themes now changes the entire ambient background (previously themes only affected buttons, not background atmosphere)rgba(91,140,255,0.55) blue/purple to color-mix(var(--gradient-from) 38%, transparent) — breathing glow follows the active theme hue, so blue/purple/green/orange/gold themes each have a distinct atmospheric tonergba(255,255,255,0.75)→rgba(244,247,251,0.65) to rgba(255,255,255,0.78)→rgba(229,235,245,0.65); dark-mode from neutral dark-gray to deep navy rgba(22,30,48,0.85)→rgba(11,18,32,0.75)<div> had bg-background opaque class overriding the body gradient — now removed so the gradient is actually visiblegold #C9A227 / navy #1E40AF / wine #9F1239 / champagne #B89968, suited for finance, business, and luxury-brand contextsdustyblue #64748B / terracotta #B45434 / sage #6B8E5A / mauve #8E7CC3, low-saturation premium grays for long-session eye comfortcoral #F87171 / forest #166534 / ocean #155E75, calm natural tonesforest light #166534 / dark #4ADE80) for WCAG contrastaccounts.ts theme-removal list includes the 11 new classes; zh.ts / en.ts / AboutPage.tsx updated from "21 themes" to "32 themes"animate-pulse + 45° repeating-linear-gradient), overflow visual width proportional to excess ratio (capped at 60% so base color remains visible)bg-red-500/10 + border-red-500/30 highlight areausagePrecision setting (2 decimals when enabled, 1 when off)test/e2e-fullsuite/ (30 cases, 29/30 pass) — covers Claude Code / OpenCode real captured requests + boundary/error paths/v1/messages/count_tokens, /v1/models, /v1/responses (OpenAI Responses API)tool_choice=any/none, stop_sequencesnode test/e2e-fullsuite/run.mjs), supports --only <id|tag> filter, JSON report (last-report.json)npm run test:e2e and npm run test:e2e:only scripts; full docs at docs/E2E-TESTING.mdclaude-sonnet-4.5 (overridable to claude-opus-4.7 etc); CASE 01 probe assertion relaxed (Kiro proxy has no probe-intercept)token=Nchars length indicator[IPC], [Kiro API], [Kiro REST API] each reduced to 1 line per request/response[KiroPayload] and [KiroAPI] Request to keep structured data in expandable details[REST->Unified] Converting response duplicate log, Using K-Proxy agent noise logsround-robin (default, load balanced) or sticky (preserves prompt cache); UI toggle next to Multi-Account switchrecordSuccess always pinned currentIndex to the success account, so successful requests stuck on the same account until failure. Default behavior changed to true round-robin (currentIndex = (success + 1) % len). Existing sticky behavior preserved as opt-in for prompt-cache-sensitive workloads.localStorage('models_dialog_ip_tip_dismissed').history.assistantResponseMessage.reasoningContent was rejected by Kiro backend with 400 Improperly formed request. Now history drops thinking blocks (current-turn thinking still works via additionalModelRequestFields.thinking={type:'adaptive'}). Affects both Anthropic and OpenAI converter paths. Caught by E2E CASE-08/09.input_tokens now subtracts cache_read + cache_creation to match Anthropic spec (was inflating client billing display)mapModelId now falls back to MODEL_ID_MAP.default (claude-sonnet-4.5) when model is completely unrecognized; preserves forward-compat for claude-{sonnet|haiku|opus}-{ver} patterns. Previously typo'd model names returned upstream 400 Improperly formed request. Caught by E2E CASE-20.credits / responseTime / cacheReadTokens / reasoningTokens in stats — affected /v1/responses (both stream and non-stream), /v1/chat/completions non-stream, /v1/messages non-stream. Frontend log table showed - for Credits and Time columns on non-streaming requests. All 4 paths now emit the full event payload + persist to recordRequest.cache_control breakpoints, calculates cache_read_input_tokens and cache_creation_input_tokens per account, returns realistic cache usage in API responsesephemeral TTL (5min/1h)206.3M, 1096K) with hover tooltip for full valueconsole.log/warn/error into log store@tanstack/react-virtual) — handles 100K+ entries without lagtool_result content block N requires text — empty/null tool results now normalized to "(no output)" instead of throwing 400modelSupportsThinkingParam()logStreamEvents enabledsimple-task, CLAUDE_SONNET_4_20250514_V1_0, CLAUDE_HAIKU_4_5_20251001_V1_0, CLAUDE_3_7_SONNET_20250219_V1_0thinking parameter no longer causes 400 REQUEST_BODY_INVALID — all thinking requests mapped to Kiro enum { type: "adaptive" } (Kiro schema only accepts ["adaptive", "disabled"])context_management, effort, anthropic_beta no longer injected into additionalModelRequestFields — Kiro schema does not allow additional properties, only thinking is permitted--- SYSTEM PROMPT --- text in user messages (detected as prompt injection by Claude models) — now uses Kiro official Human/AI pair injection matching the official IDE behaviorclaude-opus-4.7 to a Sonnet model — matching uses model family exclusion (opus/sonnet/haiku) to prevent cross-family mismatchesListAvailableModelsestimateTokens() helperSM_AI_STUDIO_IDEconversationId stabilization — same client session reuses the same conversationId across multi-turn requests (matches official Kiro IDE behavior)X-Claude-Code-Session-Id, x-opencode-session, x-session-affinity) → body fields (conversation_id, thread_id, session_id) → history fingerprint fallback/admin/cache/clear endpoint — manually clear conversationId and model cacheredacted_thinking block support — Kiro's ReasoningContentEvent.redactedContent decoded and converted to Anthropic redacted_thinking content blocks (request input and response output)thinking parameter also mapped to Kiro additionalModelRequestFieldsInvalid token error in Kiro IDEkiro-auth-token.json, ensuring Kiro IDE always gets a valid accessTokenprofileArn is now always included in the token file, auto-derived from provider when not stored (Google/GitHub → social profile, BuilderId → builder profile)region or clientIdHash fields)profileArn, and correctly identifies social vs IdC loginisSocial detection no longer incorrectly classifies BuilderId as social loginANTHROPIC_DEFAULT_HAIKU_MODEL, ANTHROPIC_DEFAULT_OPUS_MODEL, and ANTHROPIC_DEFAULT_SONNET_MODEL fields, matching the full official config formatclaude-3.7-sonnet) now appear in one-click client configuration model listInternet Settings) and macOS (scutil --proxy) with 30s cache[#taskId] to prevent log mixing{ message, taskId } for better filteringrefreshAppJSConfig uses Promise lock to prevent concurrent workers from racing on app.js download400 Improperly formed requestCLI origin for /SendMessageStreaming, and the ineffective automatic fallback from amazonq-cli to IDE protocol endpoints was removedmachineId, provider, authMethod, accountId) to ListAvailableModelsfetch failed, token expiration, refresh failures, and UnauthorizedException are no longer counted as banned accountsAccountSuspendedException, AccountSuspended, or HTTP 423), so transient network/token errors can still be retried in later refresh cycles403 is no longer treated as a ban signal during account status checks/v1beta/models, /v1beta/models/{model}:generateContent, /v1beta/models/{model}:streamGenerateContent)amazonq-cli preferred endpoint uses SendMessageStreaming only, no fallback on failureFATAL (request problem, return directly) vs RECOVERABLE (account problem, switch to next)onPoolEmpty lazy-load callback — proxy auto-loads accounts from store on first request (fixes Mac cold-start 503)All accounts quota exhausted (X/Y exhausted, Z in cooldown))<thinking> tag detection, directly pass through native reasoningContentEvent as OpenAI reasoning_content / Claude thinking blockadditionalModelRequestFields support — passes through thinking parameter from client to Kiro API~/.local/share/kiro-cli/data.sqlite3 SQLite databaseswitchTarget settingoverageStatus field detection — correctly maps REST API "ENABLED"/"DISABLED" strings to boolean valuesresourceDetail and overageCapability to frontendchcp 65001 to dev script)claude-opus-4.7 and other dynamic models no longer downgraded/v1/models results, avoids selecting unavailable static aliasesListAvailableModels official IDsx-amzn-kiro-agent-mode headerchrome_144tlsclientwrapper API call — body as 2nd parameter, options as 3rd parameterproxy-logs.json until manually clearedEnterprise provider typeqSubscriptionType parameterx-amzn-codewhisperer-optout-preference request header/anthropic/v1/messages, /v1/messages/count_tokens, /api/event_logging/batch endpointsThis project is licensed under the AGPL-3.0 License.
Thanks to all users who use and support this project!
If this project helps you, please give it a Star ⭐!
QQ Group: 653516618
A powerful multi-account management tool for Kiro IDE
Quick account switching, auto token refresh, group/tag management, machine ID management and more
English | 简体中文
📢 Sponsored Advertisement
Swiftproxy offers high-quality rotating and static residential proxies, with 90M+ residential IPs across 220+ locations worldwide. Supporting HTTP(S), SOCKS5, IP rotation, and sticky sessions, Swiftproxy provides flexible proxy solutions for Kiro account management, automation, and multi-account workflows.
💰 Rotating residential proxies starting at $0.7/GB
🎁 Exclusive Discount Code:
PROXY90— Get 10% OFF!
Shows account statistics, current account details, subscription info and quota breakdown.
Manage all accounts, search, filter, batch operations, one-click switch.
Manage device identifier, prevent account association bans, backup and restore.
Configure theme colors, privacy mode, auto refresh, proxy and more.
Provides OpenAI and Claude compatible API endpoints with multi-account rotation, auto token refresh, request retry and more.
Sync Kiro IDE settings, edit MCP servers, manage user rules (Steering).
View version info, feature list, tech stack and author info.
Simply run the .exe installer.
Since the app is not code-signed by Apple, macOS will show "damaged and can't be opened" on first launch. Please follow these steps:
Method 1: Terminal Command (Recommended)
xattr -cr /Applications/Kiro\ Account\ Manager.app
Method 2: Right-click Open
Control and click the app (or right-click)chmod +x kiro-account-manager-*.AppImage
./kiro-account-manager-*.AppImage
dpkg -isnap install⚠️ Note: Modifying machine ID requires admin privileges, please run the app as administrator
npm install
npm run dev
# Windows
npm run build:win

# macOS
npm run build:mac

# Linux
npm run build:linux
# Windows 64-bit
npx electron-builder --win --x64

# Windows 32-bit
npx electron-builder --win --ia32

# Windows ARM64
npx electron-builder --win --arm64

# macOS Intel
npx electron-builder --mac --x64

# macOS Apple Silicon
npx electron-builder --mac --arm64

# Linux 64-bit
npx electron-builder --linux --x64

# Linux ARM64
npx electron-builder --linux --arm64
The project is configured with GitHub Actions workflow for auto building all platforms and architectures:
| Platform | Architecture | Format |
|---|---|---|
| Windows | x64, ia32, arm64 | exe, zip |
| macOS | x64, arm64 | dmg, zip |
| Linux | x64, arm64, armv7l | AppImage, deb, snap |
Push Tag: Auto build and release when pushing v* format tags
git tag v1.1.0
git push origin v1.1.0
Manual Trigger: Manually run workflow in GitHub Actions page
additionalModelRequestFieldsSchema from ListAvailableModels response to detect thinking capabilitythinking: {type, budget_tokens} and reasoning_effort to Kiro's additionalModelRequestFields (supports both output_config and reasoning schema paths)/v1/messages thinking: {type:"enabled", budget_tokens} to corresponding effort levels (low/medium/high/xhigh)reasoning_content field in OpenAI format, thinking content blocks in Claude formatTHINKING_SIGNATURE_INVALID error auto-retry — strips reasoningContent from history and retries (signature invalidation due to model updates)profileArn via POST codewhisperer.{region}.amazonaws.com/ListAvailableProfilesarn:aws:codewhisperer:{region}:610548660232:profile/VNECVYCYYAWN used when auto-fetch failssetProfileArnPersistCallback module-level callback — self-healed profileArn writes back to account pool + renderer store + memory snapshotonProxyAccountUpdate IPC event — renderer listens and persists profileArn to both top-level and credentials.profileArnProxyPanel and lazy-sync now read acc.profileArn || acc.credentials?.profileArnrefresh-account-token and verify-account-credentials now auto-fetch profileArn for ALL account types (not just Enterprise)refreshAccountToken store action now saves returned profileArn to both top-level and credentials<tool_use id="...">...</tool_use> XML as text content (in assistantResponseEvent / codeEvent) alongside structured toolUseEvent — these are now stripped from text output, preventing raw XML tags from appearing in client responsesx-amzn-kiro-agent-mode header sent to Kiro backend.kiro/steering/*.md rule filesalways-type steering documents are automatically injected into every request's system prompt (supports YAML frontmatter with inclusion: always/fileMatch/manual)ContextUsageEvent breakdown (Conversation / MCP tools / Steering files) from Kiro backend stream responsessteeringLoader.ts module — reads, parses frontmatter, and formats steering files for prompt injectionresolveProfileArnForWrite returned BuilderId placeholder ARN for Enterprise accounts when switching to IDE — IDE then used this invalid ARN causing "Invalid token" error. Now returns region-aware Enterprise fallback ARNresolveProfileArnForWrite now pass region parameter for correct Enterprise ARN generationresolveProfileArnForWrite to return placeholder ARN for BuilderId — Kiro IDE internal logic depends on this field existing; removing it caused IDE malfunctionListAvailableModels, ListAvailableSubscriptions, CreateSubscriptionToken, setUserPreference) now send placeholder ARN again (AWS 400 "profileArn must not be null")generateAssistantResponse / SendMessageStreaming) still do NOT send placeholder ARN (causes 403)migrateAccountDataIfNeeded cleanup of placeholder ARNs from account datasoftprops/action-gh-release@v1 uploading duplicate filenames causing 404 — replaced with find + cp flatten-and-dedup to release-assets/ directory before uploadyaml-language-server schema declaration to suppress IDE YAML lint false-positivesinputTokens, outputTokens, cacheReadTokens, reasoningTokens and other metric fields were incorrectly redacted as *** — removed overly broad 'token' matching rule, added SAFE_KEYS whitelistRegistrar.destroy() did not call abort(), causing destroyed registrars to continue executing async steps (e.g. sending OTP), leading to "no registration in progress" error when submitting verification codereadLine() had no timeout — when the server stalls mid-stream (network jitter / throttling / half-closed connection), the Promise hung forever, causing the mail-polling step to deadlock. Added 30s timeout with auto-reconnect on next retryThis release focuses on the core failure "after switching accounts / refreshing tokens in this app, Kiro IDE desktop gets force-logged-out ~1 hour later", closes the chain of bugs where BuilderId accounts still got written placeholder profileArn in multiple paths, adds an optional IDE Token proactive-renewal capability (off by default), fixes macOS auto-update 404, and ships a Kiro IDE binary patcher script plus several UI tweaks.
switch-account wrote the already-rotated/invalidated old refreshToken to disk — the old code only updated the local variable accessToken after calling OIDC for access_v2 + refresh_v2, but the refreshToken written into ~/.aws/sso/cache/kiro-auth-token.json was still v1 (immediately invalidated by BuilderId's rotating refresh-token mechanism). Kiro IDE's refresh loop later used v1 against OIDC → 401 → logoutAndForget() force-logoutrefresh-account-token ("Refresh Token" button) never wrote to disk at all — the old code only updated the in-app store and notified the renderer; the disk token file was untouched, so Kiro IDE never saw the new token. The UI showed "refreshed" but IDE actually kept using the old one and hit the same 401 → logout ~1h laterbackground-batch-refresh (the IPC used by "Auto Refresh") also never wrote to disk — the Auto Refresh feature (default every 5 minutes) refreshed all accounts but never synced to the IDE disk file. This was the biggest hidden hole after the switch/refresh-button fixes. Now every refreshed account, if recognized as the IDE current active account, is auto-syncedswitch-account hardcoded expiresAt = Date.now() + 3600*1000; now uses the real expiresIn returned by OIDCswitch-account previously still wrote the old token on OIDC refresh failure (planting a landmine); now it errors out without writing and surfaces a clear messagesrc/main/kiroAuthSync.ts and Bidirectional SyncwriteKiroAuthTokenFile / readKiroAuthTokenFile shared helpers — uniformly read/write ~/.aws/sso/cache/kiro-auth-token.json in a fully Kiro-IDE-compatible format (mode 0o600 etc.); social / IdC field ordering matches the IDE source serializerparseAccessTokenClaims — decodes the JWT body of an access token for sub / email / aud, used during reverse sync to identify "which account did the IDE just self-refresh"watchKiroAuthTokenFile — uses fs.watchFile with content-level debouncing; hooked up on app startlastSwitchedAccountId / refreshToken equality) finds the account in store → updates credentials → webContents.send('kiro-ide-token-changed') triggers renderer to loadFromStorage, UI immediately shows latest expiresAtlastWrittenTokenSignature (the token written by this app itself) is recognized by the watcher and skipped, preventing ping-pong between IDE and the appswitchAccount IPC returns refreshedCredentials (the real post-refresh access/refresh/expiresIn); the renderer immediately syncs to store, eliminating the cascading bug "store still holds v1 → next refresh hits invalidated refresh"FixedProfileArns hardcodes the placeholder ARN profile/AAAACCCCXXXX for BuilderId — calling codewhisperer.us-east-1.amazonaws.com/ListAvailableModels with this ARN deterministically triggers 403 "User is not authorized to make this call." The reverse-proxy side kiroApi.ts's resolveProfileArn now returns no profileArn for BuilderId and unknown providers; all call sites (fetchKiroModels / callKiroApiStream / 3 subscription endpoints) guard with null-checksswitch-account / switch-account-cli / refresh-account-token sync branch / runProactiveRenewal) still inlined the placeholder ARN — BuilderId accounts were force-stamped this placeholder into ~/.aws/sso/cache/kiro-auth-token.json or ~/.local/share/kiro-cli/data.sqlite3, planting the same landmine for Kiro IDE / kiro-cli REST calls. All paths now use the unified resolveProfileArnForWrite helper, which always returns undefined for BuilderIdkiroAuthSync.ts centrally hosts KIRO_BUILDER_ID_PLACEHOLDER_ARN / KIRO_SOCIAL_PROFILE_ARN; reverse-proxy kiroApi.ts becomes a re-exporter, eliminating drift risk across 5 duplicated constantswriteKiroAuthTokenFile — if a placeholder ARN is detected in input, it is automatically stripped to undefined, catching anything that bypassed the helpermigrateAccountDataIfNeeded performs a one-time scan of account data in electron-store, clearing placeholder ARNs written by older versions / Kiro IDE itself, then writes back idempotentlyattemptRefreshIfCloseToExpiry never fires, completely eliminating any race against OIDC rotationswitch-account / refresh-account-token / logout-account all schedule or clear the timer correctly with zero leaksproactiveRenewalEnabled key) and auto-restored after restarting the appscripts/patch-kiro-ide.cjsextension.js and the bundled JS under packages/kiro-shared:
getFixedProfileArn: short-circuit void 0 for BuilderIdsupportsProfiles: remove BuilderId from the IdC listresolveProfileArn: return void 0 directly for BuilderId tokens%APPDATA%/Kiro/User/globalStorage/kiro.kiro-agent/profile.json.kpatch-backup) + flags: --dry-run / --restore / --verbose / --kiro-dir; re-run the same command after Kiro IDE upgrades to re-patchnode scripts/patch-kiro-ide.cjs --dry-run for preview; node scripts/patch-kiro-ide.cjs to apply. Fully quit Kiro before runningelectron-builder replaces spaces in productName with . for the mac zip filename (yielding Kiro.Account.Manager-1.7.2-mac.zip), but the url field in latest-mac.yml replaces spaces with - (pointing at Kiro-Account-Manager-1.7.2-mac.zip). The mismatch caused updater 404. electron-builder.yml now sets mac.artifactName: ${name}-${version}-${arch}-mac.${ext} and explicit target: zip/dmg × [x64, arm64], unifying naming to kiro-account-manager-… across platforms and making latest-mac.yml include both x64 and arm64 entries so Apple Silicon users get a native arm64 buildRefreshCw icon and were visually indistinguishable; now respectively switched to Activity (check/activity semantic) and KeyRound (refresh-token semantic, consistent with the card view) with i18n tooltipsonKiroIdeTokenChanged IPC event — renderer subscribes and triggers loadFromStorage on receipt; the UI refreshes expiresAt instantly after IDE self-refreshnpm run typecheck:node && npm run typecheck:web both pass with zero errors--dry-run precisely targets all 5 candidate files on Windows D:\Program\Kiro (3 + 1 + 1 + 1 + 1 replacements)This release focuses on bulk import & quick-pick batched opening in the Subscription "Get Links" view, a boundary-character fix in card-key/credential parsing (resolving import-verification 401s), and assigning accounts to a chosen group when adding / batch-adding / importing.
-, it abuts the ---- separator forming 5+ consecutive -. The old split('----') consumed only the first 4, dropping ClientSecret's trailing - (corrupting the JWT) and turning provider into -BuilderId → authMethod mis-detected as social → refresh hit the wrong endpoint and returned 401splitCredentialLine — matches separators with /-{4,}/ and returns the extra (N-4) - to the previous field, keeping the JWT intact and provider correct; applied to OIDC batch import, TXT file card-key import, and Outlook mailbox parsingidp=BuilderId and ignored the 6th field — now reads the login method and infers from ClientId / Secret, consistent with the dialog batch-import logicgroupId: undefined, sending new accounts to "Ungrouped" forever — now they are categorized by the selected groupThis release focuses on Proton-based registration OTP auto-retrieval (accuracy + speed + log visibility), the Proton login-state & proxy experience, and card-key import/export fixes for GitHub/Google social-login accounts.
no-reply@signin.aws and reads the top two candidates, avoiding the "opened current mail but no code" deadlockprocess.env.HTTPS_PROXY) instead of the system proxy or the registration proxy pool; the session proxy is also refreshed on window reuse, so proxy changes take effect on the next retrievalprovider=BuilderId(IdC) on import, but social accounts have no ClientId / Secret and were rejected by the verify endpoint's authMethod !== 'social' && (!clientId || !clientSecret) guard ("please fill in Client ID and Client Secret")email----password----RefreshToken----ClientId----ClientSecret----loginMethod, so import can accurately restore social(Github/Google) / IdC(BuilderId/Enterprise)This release packs 70+ improvements covering reverse-proxy security hardening, batch registration concurrency isolation, SOCKS proxy support, unified task center, webhook notifications, analytics reporting, one-click diagnostics, config import/export, and major performance optimizations.
P0 Critical Security
readBody now enforces a max body size (default 10MB), rejects oversized Content-Length early + breaks connection on stream overflow → HTTP 413 (DoS protection)host=0.0.0.0/:: without any API Key; red banner in UI + explicit allowExternalWithoutApiKey flag required to bypasscrypto.timingSafeEqual to prevent timing-attack key guessing/admin/config GET masks apiKeys[].key plaintext, showing only xxxx***last4P1 Operations & Observability
/admin/config POST field allowlist, blocks remote mutation of port/host/apiKeys/tlsconversation_id to same account → preserve prompt cache + anti-risk-control)stop() (5s grace period → activeRequests.abort → socket.destroy)P2 Advanced
/metrics endpoint (8 core metrics: requests/tokens/credits/accounts/uptime)/admin/audit GET + enableAuditLog toggle)apiKeyAccountBindings: apiKey id → allowed account id array)fallbackPort simultaneously)recentRequests limit (default 100, max 10000)New files: src/main/proxy/selfSignedCert.ts, ProxySecurityPanel.tsx
New IPC: proxySelfSignedCertInfo / proxySelfSignedCertRegenerate / proxyNeedsRestart / proxyRestart / proxyAuditLog / onProxyWebhookTrigger
socks library + undici custom Agent + TLS upgrade)Concurrency Isolation Fixes
buildAutoConfig, weight rotation now actually works)resolvedProxyUrl() now includes system/env proxies)Feature Expansion
batchAutoImport and autoFetchProLink)useTaskStore, titlebar entry + drawer UI)I/O & Persistence
saveToStorage 500ms debounce + flushSaveImmediately force-flush APIcreateBackup 5-minute throttle (previously backed up on every save)ProxyLogStore async fs.promises.writeFile + 30s throttle + maxLogs 1M → 50Kproxy-account-suspended IPC updates memory snapshot only, deferred disk writequeueMicrotask async loading (no longer blocks loadFromStorage)Render & Compute
getFilteredAccounts / getStats / activeAccount module-level memoizationapplyBackgroundRefreshResults / applyBackgroundCheckResults batch merge (120ms buffer)importAccounts / importFromExportData single set callupdateTrayInfo 400ms debounceAccountToolbar selection status with useMemo + useCallback@tanstack/react-virtual, only render visible area)Invalid URL protocol (Windows registry ProxyServer multi-protocol string parsing, take only HTTP/HTTPS)tls-client-wrapper DLL moved to userData/tls-client/ for permanent storage (was in %TEMP%, could be cleaned by system)proxyServer.stop() socket force-destroy was too early, truncating responsesProxyPoolPage — Proxy pool management + advanced search + account binding + scheduled validationWebhooksPage — Webhook configuration + testing + event subscriptionDiagnosePage — One-click diagnostics (network / API / email / proxy / custom)ConfigSyncPage — Config import/export + AES-GCM encryptionproxyUrl field (account-bound egress proxy)machineId field (account-bound device ID)maxRequestBodyBytes / allowedIPs / deniedIPs / allowExternalWithoutApiKey / rateLimitPerKeyPerMinute / sessionAffinityEnabled / keepAliveTimeoutMs / headersTimeoutMs / recentRequestsLimit / enableMetrics / apiKeyAccountBindings / fallbackPort / enableAuditLog / apiKeyGroupBindings(deprecated)
text-green-500/600 → text-success, text-red-500/600 → text-destructive, text-amber/orange-500/600 → text-warning, decorative bg-blue-50/... → bg-primary/[0.04~0.15]_helpers.ts getStatusBadgeClass status colors fully tokenized with auto dark mode support--card-solid CSS variable (light #FFFFFF / dark #1A2236) — dedicated opaque background for account cards.bg-solid-card utility class with dual-class selector (.glass-card.bg-solid-card) to override glass-card transparent background and disable backdrop-filterbg-card into account data area causing "tinted overlay" effectbg-card transparencygenerateRowGlowStyle single-tag case removes horizontal background gradient, keeping only left 3px color stripe; multi-tag keeps vertical gradient stripebox-shadow/background) causing no visual feedback — switched to absolutely positioned overlay layer (absolute inset-0 ring-2 ring-inset ring-primary/60 bg-primary/[0.08] z-10) isolated from inline stylering-2 ring-primary/60 + bg-primary/[0.08] + primary shadowuseAccountsStore added activeGroupTab state ('all' | 'ungrouped' | <groupId>) with localStorage persistence — replaces multi-select filter logicgetFilteredAccounts() filters by activeGroupTab first (mutually exclusive)<header> got relative z-20 to elevate stacking context (.glass-toolbar's backdrop-filter creates isolated z layer)size="icon" h-8 w-8), saving ~280px widthChevronDown, more restrainedbg-destructive/10 red as warningProPlanType type — Pro / Pro+ / Power, mapped to Kiro backend Q_DEVELOPER_STANDALONE_{PRO|PRO_PLUS|POWER} qSubscriptionTypefetchProSubscriptionUrl uses user-selected plan type instead of hardcoded PROaccountPool.isAccountAvailable only marks accounts unavailable when refreshToken is missing; expired accounts with refreshToken pass through to proxyServer.getAvailableAccount for refresh; refresh failures auto-isolated via markNeedsRefresh forming a closed loopProxyConfig added multiAccountSelectionMode: 'all' | 'groups' and multiAccountGroupIds: string[] fieldssyncAccounts filters accounts by selected groups in multi-account + groups modemultiAccountSelectionMode / multiAccountGroupIds / accountSelectionStrategy)icon-only h-7 w-7 moved to Label row right side<p> tags moved to Label title tooltip (saves 30-40% vertical space)col-span-3 row ([Auto-trim toggle 160px][Number input flex-1])flex-wrap to grid-cols-3, 3 toggles (auto-switch/log requests/stream events) on one rowsk-xxx dropdown h-6 clipped by Select's internal py-2 — used Tailwind arbitrary attribute selector [&>button]:h-7 [&>button]:py-0 [&>button]:px-2.5 to force overrideSettings2 icon + uppercase tracking-wider minimalizedAccountManager.tsx trailing extra } causing TypeScript syntax errorAccountFilter.tsx cleaned up unused groups destructuringtokenCounter.ts module — encapsulates js-tiktoken cl100k_base encoder and getModelContextLength function, unifying all token computation logictokenUsage real value > contextUsageEvent percentage reverse calculation (modelCtx × percentage / 100) > tiktoken precise count > character-based fallback (input 0.42, output 0.4)assistantResponseEvent / codeEvent text and apply tiktoken, no longer relying on character lengthgetModelContextLength 3-tier lookup chain — Kiro fetchKiroModels's real maxInputTokens cache first → fuzzy match (claude-sonnet-4.5 ↔ claude-sonnet-4-5-20251001) → keyword fallback (sonnet/haiku/opus/gpt-4 etc.)CodeEvent parsing support — fixes lost streaming code content on this endpointparseEventStream signature extended with modelId and payloadStr parameters for end-to-end model context propagation enabling contextUsage reverse calculationmodelContextWindowCache definition in kiroApi.ts; unified import and re-export from tokenCounter.ts for backward compatibilitytokenBufferReserve behavior change — v1.6.7 force-enabled 50K reserve; v1.6.8 makes it an opt-in toggle, off by default, default value lowered to 20K when enabledenableTokenBufferReserve standalone switch — new field in ProxyConfig, frontend UI adds inline Switch controltrimHistoryByTokens is completely skipped; CONTENT_LENGTH_EXCEEDS_THRESHOLD from Kiro backend is forwarded as-is to the clientmodel.maxInputTokens - tokenBufferReserve (200K → 180K, 1M → 980K, range 5K~150K)disable condition extended with !enableTokenBufferReserve — input auto-greys when switch off; all related controls locked while server is runningnormalizeProxyUrl utility — auto-normalizes user-input non-standard proxy URLs (e.g. http:127.0.0.1:7890 missing //, 127.0.0.1:7890 missing scheme, leading/trailing whitespace) into standard http://host:port formatHTTP_PROXY/HTTPS_PROXY/NO_PROXY), Electron session.setProxy, and frontend UI now consistently use the normalized URL, avoiding proxy failure or duplicate setupset-proxy returns normalizedUrl to frontend store, auto-writing back to UI input for visual confirmationProxyConfig fields, IPC proxyStart/proxyUpdateConfig type signatures, backend OpenAI handleOpenAIStream and Claude handleClaudeStream auto-continue branches)tool_calls / tool_use directly to client after completion; client decides what to do next, no more server-side "fake continue" recursive call pathclientDrivenToolExecution=true configuration; long unusedelectron-builder build error ENOENT: no such file or directory, rename 'electron.exe' -> 'kiro-account-manager.exe' — root cause was incomplete electron-v38.7.2-win32-x64.zip download from npmmirror corrupting the Electron binary; switched to BITS download from cdn.npmmirror.com/binaries/electron/ for full zipapp.js download triggers RangeError: init["status"] must be in the range of 200 to 599, inclusive. — tlsclientwrapper returned status=0/undefined on network errors, triggering new Response() validation exception. Switched to undici fetch for static resources to bypass tls-client and avoid polluting its global statefailed to build client out of request input: failed to modify existing client: no tls client for modification check when proxy enabled — app.js download failure polluted the tls-client DLL global state, causing subsequent SessionClient initialization to fail. Auto-resolved by the app.js undici fix abovesetProxy changed to async function — awaits normalized URL from IPC and writes back to store for display, preventing UI/effective value mismatch403 + reason:"TEMPORARILY_SUSPENDED"), AccountSuspendedException (CodeWhisperer), and 423 Locked responsesProxyAccount gains suspendedAt / suspendReason / suspendMessage fields to track long-term bans (distinct from temporary errorCount cooldown)AccountPool adds isSuspended / markSuspended / clearSuspended — suspended accounts are permanently skipped in isAccountAvailable until manually cleared or reset()onAccountSuspended event + IPC proxy-account-suspended — full bridge from proxy server → main → preload → renderer store → UIstore.accountData[id].lastError and status='error' — survives app restartisBannedAccountError across store/accounts.ts / AccountSelectDialog / AccountCard — all three now recognize temporarily_suspended / temporarily suspended / User ID is suspended patterns and display the ban bannerAccountCard ban-detail dialog now has a Reset Suspended button that calls IPC proxy-clear-account-suspended → clears accountPool suspended flag + wipes store.accountData[id].lastError + sets status='active'accountPool.addAccount previously always forced isAvailable=true, which would silently wipe out the suspended state if an account was re-added (e.g., after proxy-sync-accounts). Now addAccount respects the incoming suspendedAt field and preserves isAvailable=false, so suspended accounts re-added from persisted data stay correctly skipped.host was 127.0.0.1 (loopback only) and the UI "Public" toggle was disabled while the server was running, so users couldn't switch without stopping the servicehttp://localhost:5580 instead of http://0.0.0.0:5580 (the latter is not a valid client target); copy-address button uses the same human-readable formLAN devices use http://<this-machine-IP>:<port>#f4f7fb, primary #5B8CFF, violet accent #8B5CF6, success #22C55E, translucent white borders rgba(255,255,255,0.4).glass-card / .glass-card-strong / .glass-card-subtle / .glass-sidebar / .glass-toolbar utility classes with backdrop-filter: blur(24px) saturate(180%)rounded-3xl (24px), glass backdrop, framer-motion spring width animation, layoutId-based active pill morph (primary → violet gradient)<Card> now defaults to glass variant with rounded-2xl (24px), supports variant=glass/glass-strong/glass-subtle/solid/elevated and interactive prop for hover-lift animation (translateY -2px + enhanced shadow).page-hero class with consistent 24px rounded glass headerglass-toolbar (16px blur + subtle bg + border-bottom only)AnimatePresence + motion.div wraps page content with fade + 8px Y-axis spring transition on route change#0a0e1a background with glass surfaces tuned for low-light readabilityframer-motion ^11.x for declarative animationsmotion.div wrapper now uses h-full flex flex-col so child page's flex-1 overflow-auto works correctly<Card className="border-0 shadow-sm hover:shadow-md transition-shadow duration-200"> across HomePage / SettingsPage / AboutPage / RegisterPage / KiroSettingsPage / ProxyPanel replaced with hover-lift — default glass variant now fully visibleUpdateDialog / CloseConfirmDialog / AccountDetailDialog / ProxyDetailedLogsDialog) switched from bg-background rounded-xl border to glass-card-strong rounded-2xl + backdrop-blur overlayButton component reworked: rounded-xl default, transition-all 200ms, hover -translate-y-px + ring-color glow on default/destructive variants, new gradient variant (theme-aware gradient-bg-primary + breathe-glow animation), new cta size (h-12 rounded-2xl) for primary call-to-actions--gradient-from / --gradient-to pair (purple/emerald/orange/rose/cyan/amber/teal/indigo/lime/pink/slate/zinc/sky/violet/fuchsia/red/yellow/green/stone/neutral + default). Sidebar's motion.span layoutId="sidebar-active-pill" reads from CSS vars, so the active menu pill morphs through the selected theme's hue gradient (e.g., emerald theme → teal-green gradient instead of fixed blue→violet)gradient-bg-primary and gradient-border utility classes now use var(--gradient-from/-to) so all gradient buttons/borders follow theme selection automaticallymain container now has .page-surface (dual blue/violet radial blobs @ 18% / 14% opacity, 60px blur) so glass cards have actual color to refract through — previously cards looked solid white on solid white backgroundborder + hover:shadow-lg overrides that were stomping the glass system; now uses hover-lift utility (translateY -2px + enhanced shadow) on non-active/non-banned cards; active glow border and banned red border preservedbg-[var(--glass-bg-subtle)] backdrop-blur-md with rounded-xl + larger focus ring; filter panel number inputs (AccountFilter) same treatmentlocalStorage('accounts_viewMode'). Compact list rows show inline email + status + subscription + tags + credit progress + key actions, with ~5x density vs cards (good for managing 100+ accounts)displayLimit default changed from All to 5K and now persists to localStorage('systemLogs_displayLimit') — previously the value reset to All on every page navigation/app restart, hurting initial render performance with large log volumestokenBufferReserve setting (replaces previous maxInputTokensThreshold) — adaptive history trimming based on the actual model's contextWindow returned by ListAvailableModelsmodel.maxInputTokens - tokenBufferReserve per request — default 50000 reserve fits all models (200K models → 150K cutoff, 1M models → 950K cutoff)system + tools + current message + output budget + estimation skew, preventing CONTENT_LENGTH_EXCEEDS_THRESHOLD on long conversations regardless of byte-based payload sizefetchKiroModels into the trimming logic so newly added Kiro models pick up correct limits automatically.glass-card-strong — rewritten as 90% translucent white (rgba(255,255,255,0.90) / dark rgba(20,25,40,0.90)) + backdrop-filter: blur(20px) saturate(160%) real frosted glass + 3-layer composite deep shadow (1px outer border + 0 24px 64px far shadow + 0 8px 24px near contact shadow) for strong elevationbg-black/40 backdrop-blur-sm / bg-black/50 to bg-slate-900/[0.12] dark:bg-black/50 backdrop-blur-xl — light-mode 12% slate ultra-faint mask + heavy blur (24px) so background blurs without graying out the dialog samplehover:bg-red-500 hover:text-white transition-colors, covering AccountDetailDialog / EditAccountDialog / AddAccountDialog / TagManageDialog / GroupManageDialog / ExportDialog / AccountCard ban+subscription / ApiKeyUsageDialog / AccountSelectDialog / UpdateDialog (15+ dialogs total), matching TitleBar close button for consistent danger semantics--glass-bg-strong token changed from opaque white to 90% translucent + backdrop-filter now actually applies, so dialogs are no longer flat opaque cards but true glass panels#f4f7fb → #EEF2F8 icy blue (inspired by F1 Fresh Blue), reducing the dead-white "AI palette" feel#0a0e1a → #0B1220 deep navy (inspired by E1 Deep Space), shifted from neutral gray-black to blue tone#E5EBF5 → #EEF2F8 → #F2F5FA simulating daylight transition; dark mode #0F1729 → #0B1220 → #060A14 for night-sky depthcolor-mix(in srgb, var(--gradient-from) 10%, ...) — switching themes now changes the entire ambient background (previously themes only affected buttons, not background atmosphere)rgba(91,140,255,0.55) blue/purple to color-mix(var(--gradient-from) 38%, transparent) — breathing glow follows the active theme hue, so blue/purple/green/orange/gold themes each have a distinct atmospheric tonergba(255,255,255,0.75)→rgba(244,247,251,0.65) to rgba(255,255,255,0.78)→rgba(229,235,245,0.65); dark-mode from neutral dark-gray to deep navy rgba(22,30,48,0.85)→rgba(11,18,32,0.75)<div> had bg-background opaque class overriding the body gradient — now removed so the gradient is actually visiblegold #C9A227 / navy #1E40AF / wine #9F1239 / champagne #B89968, suited for finance, business, and luxury-brand contextsdustyblue #64748B / terracotta #B45434 / sage #6B8E5A / mauve #8E7CC3, low-saturation premium grays for long-session eye comfortcoral #F87171 / forest #166534 / ocean #155E75, calm natural tonesforest light #166534 / dark #4ADE80) for WCAG contrastaccounts.ts theme-removal list includes the 11 new classes; zh.ts / en.ts / AboutPage.tsx updated from "21 themes" to "32 themes"animate-pulse + 45° repeating-linear-gradient), overflow visual width proportional to excess ratio (capped at 60% so base color remains visible)bg-red-500/10 + border-red-500/30 highlight areausagePrecision setting (2 decimals when enabled, 1 when off)test/e2e-fullsuite/ (30 cases, 29/30 pass) — covers Claude Code / OpenCode real captured requests + boundary/error paths/v1/messages/count_tokens, /v1/models, /v1/responses (OpenAI Responses API)tool_choice=any/none, stop_sequencesnode test/e2e-fullsuite/run.mjs), supports --only <id|tag> filter, JSON report (last-report.json)npm run test:e2e and npm run test:e2e:only scripts; full docs at docs/E2E-TESTING.mdclaude-sonnet-4.5 (overridable to claude-opus-4.7 etc); CASE 01 probe assertion relaxed (Kiro proxy has no probe-intercept)token=Nchars length indicator[IPC], [Kiro API], [Kiro REST API] each reduced to 1 line per request/response[KiroPayload] and [KiroAPI] Request to keep structured data in expandable details[REST->Unified] Converting response duplicate log, Using K-Proxy agent noise logsround-robin (default, load balanced) or sticky (preserves prompt cache); UI toggle next to Multi-Account switchrecordSuccess always pinned currentIndex to the success account, so successful requests stuck on the same account until failure. Default behavior changed to true round-robin (currentIndex = (success + 1) % len). Existing sticky behavior preserved as opt-in for prompt-cache-sensitive workloads.localStorage('models_dialog_ip_tip_dismissed').history.assistantResponseMessage.reasoningContent was rejected by Kiro backend with 400 Improperly formed request. Now history drops thinking blocks (current-turn thinking still works via additionalModelRequestFields.thinking={type:'adaptive'}). Affects both Anthropic and OpenAI converter paths. Caught by E2E CASE-08/09.input_tokens now subtracts cache_read + cache_creation to match Anthropic spec (was inflating client billing display)mapModelId now falls back to MODEL_ID_MAP.default (claude-sonnet-4.5) when model is completely unrecognized; preserves forward-compat for claude-{sonnet|haiku|opus}-{ver} patterns. Previously typo'd model names returned upstream 400 Improperly formed request. Caught by E2E CASE-20.credits / responseTime / cacheReadTokens / reasoningTokens in stats — affected /v1/responses (both stream and non-stream), /v1/chat/completions non-stream, /v1/messages non-stream. Frontend log table showed - for Credits and Time columns on non-streaming requests. All 4 paths now emit the full event payload + persist to recordRequest.cache_control breakpoints, calculates cache_read_input_tokens and cache_creation_input_tokens per account, returns realistic cache usage in API responsesephemeral TTL (5min/1h)206.3M, 1096K) with hover tooltip for full valueconsole.log/warn/error into log store@tanstack/react-virtual) — handles 100K+ entries without lagtool_result content block N requires text — empty/null tool results now normalized to "(no output)" instead of throwing 400modelSupportsThinkingParam()logStreamEvents enabledsimple-task, CLAUDE_SONNET_4_20250514_V1_0, CLAUDE_HAIKU_4_5_20251001_V1_0, CLAUDE_3_7_SONNET_20250219_V1_0thinking parameter no longer causes 400 REQUEST_BODY_INVALID — all thinking requests mapped to Kiro enum { type: "adaptive" } (Kiro schema only accepts ["adaptive", "disabled"])context_management, effort, anthropic_beta no longer injected into additionalModelRequestFields — Kiro schema does not allow additional properties, only thinking is permitted--- SYSTEM PROMPT --- text in user messages (detected as prompt injection by Claude models) — now uses Kiro official Human/AI pair injection matching the official IDE behaviorclaude-opus-4.7 to a Sonnet model — matching uses model family exclusion (opus/sonnet/haiku) to prevent cross-family mismatchesListAvailableModelsestimateTokens() helperSM_AI_STUDIO_IDEconversationId stabilization — same client session reuses the same conversationId across multi-turn requests (matches official Kiro IDE behavior)X-Claude-Code-Session-Id, x-opencode-session, x-session-affinity) → body fields (conversation_id, thread_id, session_id) → history fingerprint fallback/admin/cache/clear endpoint — manually clear conversationId and model cacheredacted_thinking block support — Kiro's ReasoningContentEvent.redactedContent decoded and converted to Anthropic redacted_thinking content blocks (request input and response output)thinking parameter also mapped to Kiro additionalModelRequestFieldsInvalid token error in Kiro IDEkiro-auth-token.json, ensuring Kiro IDE always gets a valid accessTokenprofileArn is now always included in the token file, auto-derived from provider when not stored (Google/GitHub → social profile, BuilderId → builder profile)region or clientIdHash fields)profileArn, and correctly identifies social vs IdC loginisSocial detection no longer incorrectly classifies BuilderId as social loginANTHROPIC_DEFAULT_HAIKU_MODEL, ANTHROPIC_DEFAULT_OPUS_MODEL, and ANTHROPIC_DEFAULT_SONNET_MODEL fields, matching the full official config formatclaude-3.7-sonnet) now appear in one-click client configuration model listInternet Settings) and macOS (scutil --proxy) with 30s cache[#taskId] to prevent log mixing{ message, taskId } for better filteringrefreshAppJSConfig uses Promise lock to prevent concurrent workers from racing on app.js download400 Improperly formed requestCLI origin for /SendMessageStreaming, and the ineffective automatic fallback from amazonq-cli to IDE protocol endpoints was removedmachineId, provider, authMethod, accountId) to ListAvailableModelsfetch failed, token expiration, refresh failures, and UnauthorizedException are no longer counted as banned accountsAccountSuspendedException, AccountSuspended, or HTTP 423), so transient network/token errors can still be retried in later refresh cycles403 is no longer treated as a ban signal during account status checks/v1beta/models, /v1beta/models/{model}:generateContent, /v1beta/models/{model}:streamGenerateContent)amazonq-cli preferred endpoint uses SendMessageStreaming only, no fallback on failureFATAL (request problem, return directly) vs RECOVERABLE (account problem, switch to next)onPoolEmpty lazy-load callback — proxy auto-loads accounts from store on first request (fixes Mac cold-start 503)All accounts quota exhausted (X/Y exhausted, Z in cooldown))<thinking> tag detection, directly pass through native reasoningContentEvent as OpenAI reasoning_content / Claude thinking blockadditionalModelRequestFields support — passes through thinking parameter from client to Kiro API~/.local/share/kiro-cli/data.sqlite3 SQLite databaseswitchTarget settingoverageStatus field detection — correctly maps REST API "ENABLED"/"DISABLED" strings to boolean valuesresourceDetail and overageCapability to frontendchcp 65001 to dev script)claude-opus-4.7 and other dynamic models no longer downgraded/v1/models results, avoids selecting unavailable static aliasesListAvailableModels official IDsx-amzn-kiro-agent-mode headerchrome_144tlsclientwrapper API call — body as 2nd parameter, options as 3rd parameterproxy-logs.json until manually clearedEnterprise provider typeqSubscriptionType parameterx-amzn-codewhisperer-optout-preference request header/anthropic/v1/messages, /v1/messages/count_tokens, /api/event_logging/batch endpointsThis project is licensed under the AGPL-3.0 License.
Thanks to all users who use and support this project!
If this project helps you, please give it a Star ⭐!



