A continually evolving multi-user, multi-host NixOS configuration.
See the code
Where am I?
You're in a rabbit hole.
How did I get here?
The door opened; you got in.
Somewhere between then and now you discovered this cairne in the fog. I hope it is useful in some way. Inspiration, reference, or whatever you're looking for.
This is written perhaps as more of a reminder for myself than it is for you, but then again you could be future me or maybe past me stuck in a strange loop...
$ whoami
error: entity unknown or undefined
Steady...
The way out, is through.
Watch NixOS related videos on my YouTube channel. Chat with me directly on our Discord server.
April 30, 2026: This and other nix related repos by EmergentMind on GitHub are now mirrored from repos of the same name at https://codeberg.org/EmergentMind/. Depending on which domain you are visitng the commit signing before and after this change may show as unverified. Also, many of the reference URLs throughout may still point back to github until I get around to correcting them.
Flake-based multi-host, multi-user configurations for NixOS and Home-Manager
Secrets management via sops-nix and a private nix-secrets repo that is included as a flake input
Declarative, LUKS-encrypted btrfs partitions via disko
Impermanence - files that aren't explicitly persisted are deleted on reboot
Automated remote-bootstrapping of NixOS, nix-config, and private nix-secrets
Handles multiple YubiKey devices and agent forwarding for touch-based/passwordless authentication during:
Automated borg backups
NixOS and Home-Manager automation recipes
Automatic micro-vm sandboxing for agents
The roadmap of additional features is laid across functionally thematic stages that can be viewed, along with short term objectives, in the Roadmap of TODOs.
Completed features will be added here as each stage is complete.
This is a personalized configuration that has several technical requirements to build successfully. This nix-config will serve you best as a reference, learning resource, and template for crafting your own configuration. I am continuing to provide resources throughout this repository, my YouTube channel, and website to help. For you to be successful, you must also experiment and learn as you go to create a nix environment that suits your needs.
A stripped down and simplified version of this repository is available, however it does not have feature parity: nix-config-starter
For details about design concepts, constraints, and how structural elements interact, see the article and/or Youtube video Anatomy of a NixOS Config available on my website.
For a large screenshot of the concept diagram, as well as previous iterations, see Anatomy.
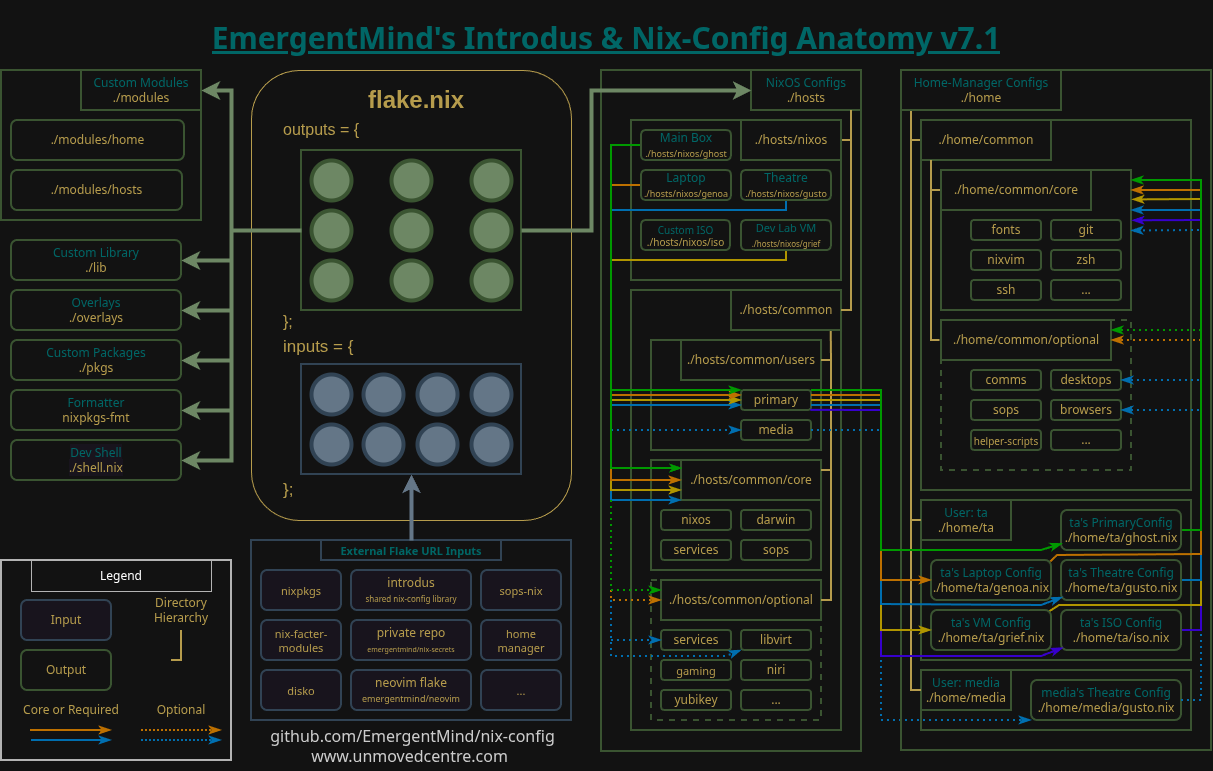
As of September 2025, we've been rethinking how to handle multiple users and the concept for Home is in a bit of flux. Some of the changes are reflected below but the latest diagram here represents the iteration prior to these changes until I have a better idea what the outcome will be and how to visually represent it.
flake.nix - Entrypoint for hosts and user home configurations. Also exposes a devshell for manual bootstrapping tasks (nix develop or nix-shell).hosts - NixOS configurations accessible via sudo nixos-rebuild switch --flake .#<host>.
common - Shared configurations consumed by the machine specific ones.
core - Configurations present across all hosts. This is a hard rule! If something isn't core, it is optional.optional - Optional configurations present across more than one host.users - Host level user configurations present across at least one host.
<user>/keys - Public keys for the user that are symlinked to ~/.sshnixos - machine specific configurations for NixOS-based hosts
genoa - ThinkPad E15 - 3.5/4.7GHz i7-1255U (6C/12T), 16GB RAMghost - Primary box - 4.8GHz Ryzen 9 5900XT (16C/32T), 64GB RAM, RX 9070XT
grief - Lab - Qemu VMgooey - stage xguppy - Remote Install Lab - Qemu VMgusto - Theatre mini pc - 3.4GHz N95 (4C/4T), 16GB RAMiso - Custom NixOS ISO that incorporates some quality of life configuration for use during installations and recoveryhome - Home-manager configurations, built automatically during host rebuilds.
common - Shared home-manager configurations consumed the user's machine specific ones.
core - Home-manager configurations present for user across all machines. This is a hard rule! If something isn't core, it is optional.optional - Optional home-manager configurations that can be added for specific machines. These can be added by category (e.g. options/media) or individually (e.g. options/media/vlc.nix) as needed.<user> - User-specific, host-specific configurations.
common - User-specific configurations common across that user's hosts.lib - Custom library used throughout the nix-config to make import paths more readable. Accessible via lib.custom.microvms - Ephemeral agent sandbox environments. The structure intentionally mimics nix-config but stays distinct seprate.
modules - Custom modules to enable special functionality and options.
home - Custom modules for home-managerhosts - Custom modules for hosts
common - Custom modules applicable to hosts on either platformdarwin - Custom modules specific to darwin-based hostsnixos - Custom modules specific to nixos-based hostsoverlays - Custom modifications to upstream packages.pkgs - Custom packages meant to be shared or upstreamed.
common - Custom packages that will work on either nixos or dariwnnixos - Custom packages specific to nixos-based hostsSecrets for this config are stored in a private repository called nix-secrets that is pulled in as a flake input and managed using the sops-nix tool.
For details on how this is accomplished, how to approach different scenarios, and troubleshooting for some common hurdles, please see my article and accompanying YouTube video NixOS Secrets Management available on my website. There is also a nix-secrets-reference repository that can be used in conjunction with the article.
Sincere thanks to all of my generous supporters!
If you find what I do helpful, please consider supporting my work using one of the links under "Sponsor this project" on the right-hand column of this page.
I intentionally keep all of my content ad-free but some platforms, such as YouTube, put ads on my videos outside of my control.
As with many personal projects, the code here tends to evolve away from what it was when the video/article content was published.
Videos - To find code relevant to when a specific video/article was published, look through tags with the word 'video' as they are commits from roughly the same time.
Darwin - To find relevant to handling hosts using both NixOS and Darwin, refer to the darwin branch. Starting in 2026, we are migrating away from Darwin support for the foreseeable future but will retain it 'as is' in the darwin branch for reference.
Those who have heavily influenced this strange journey into the unknown.
6,518 followers · starred May 2024
122 followers · starred Feb 2026
73 followers · starred Oct 2025
215 followers · starred Apr 2024
A continually evolving multi-user, multi-host NixOS configuration.
See the code Where am I?
You're in a rabbit hole.
How did I get here?
The door opened; you got in.
Somewhere between then and now you discovered this cairne in the fog. I hope it is useful in some way. Inspiration, reference, or whatever you're looking for.
This is written perhaps as more of a reminder for myself than it is for you, but then again you could be future me or maybe past me stuck in a strange loop...
$ whoami
error: entity unknown or undefined
Steady...
The way out, is through.
Watch NixOS related videos on my YouTube channel. Chat with me directly on our Discord server.
April 30, 2026: This and other nix related repos by EmergentMind on GitHub are now mirrored from repos of the same name at https://codeberg.org/EmergentMind/. Depending on which domain you are visitng the commit signing before and after this change may show as unverified. Also, many of the reference URLs throughout may still point back to github until I get around to correcting them.
Flake-based multi-host, multi-user configurations for NixOS and Home-Manager
Secrets management via sops-nix and a private nix-secrets repo that is included as a flake input
Declarative, LUKS-encrypted btrfs partitions via disko
Impermanence - files that aren't explicitly persisted are deleted on reboot
Automated remote-bootstrapping of NixOS, nix-config, and private nix-secrets
Handles multiple YubiKey devices and agent forwarding for touch-based/passwordless authentication during:
Automated borg backups
NixOS and Home-Manager automation recipes
Automatic micro-vm sandboxing for agents
The roadmap of additional features is laid across functionally thematic stages that can be viewed, along with short term objectives, in the Roadmap of TODOs.
Completed features will be added here as each stage is complete.
This is a personalized configuration that has several technical requirements to build successfully. This nix-config will serve you best as a reference, learning resource, and template for crafting your own configuration. I am continuing to provide resources throughout this repository, my YouTube channel, and website to help. For you to be successful, you must also experiment and learn as you go to create a nix environment that suits your needs.
A stripped down and simplified version of this repository is available, however it does not have feature parity: nix-config-starter
For details about design concepts, constraints, and how structural elements interact, see the article and/or Youtube video Anatomy of a NixOS Config available on my website.
For a large screenshot of the concept diagram, as well as previous iterations, see Anatomy.
As of September 2025, we've been rethinking how to handle multiple users and the concept for Home is in a bit of flux. Some of the changes are reflected below but the latest diagram here represents the iteration prior to these changes until I have a better idea what the outcome will be and how to visually represent it.
flake.nix - Entrypoint for hosts and user home configurations. Also exposes a devshell for manual bootstrapping tasks (nix develop or nix-shell).hosts - NixOS configurations accessible via sudo nixos-rebuild switch --flake .#<host>.
common - Shared configurations consumed by the machine specific ones.
core - Configurations present across all hosts. This is a hard rule! If something isn't core, it is optional.optional - Optional configurations present across more than one host.users - Host level user configurations present across at least one host.
<user>/keys - Public keys for the user that are symlinked to ~/.sshnixos - machine specific configurations for NixOS-based hosts
genoa - ThinkPad E15 - 3.5/4.7GHz i7-1255U (6C/12T), 16GB RAMghost - Primary box - 4.8GHz Ryzen 9 5900XT (16C/32T), 64GB RAM, RX 9070XT
grief - Lab - Qemu VMgooey - stage xguppy - Remote Install Lab - Qemu VMgusto - Theatre mini pc - 3.4GHz N95 (4C/4T), 16GB RAMiso - Custom NixOS ISO that incorporates some quality of life configuration for use during installations and recoveryhome - Home-manager configurations, built automatically during host rebuilds.
common - Shared home-manager configurations consumed the user's machine specific ones.
core - Home-manager configurations present for user across all machines. This is a hard rule! If something isn't core, it is optional.optional - Optional home-manager configurations that can be added for specific machines. These can be added by category (e.g. options/media) or individually (e.g. options/media/vlc.nix) as needed.<user> - User-specific, host-specific configurations.
common - User-specific configurations common across that user's hosts.lib - Custom library used throughout the nix-config to make import paths more readable. Accessible via lib.custom.microvms - Ephemeral agent sandbox environments. The structure intentionally mimics nix-config but stays distinct seprate.
modules - Custom modules to enable special functionality and options.
home - Custom modules for home-managerhosts - Custom modules for hosts
common - Custom modules applicable to hosts on either platformdarwin - Custom modules specific to darwin-based hostsnixos - Custom modules specific to nixos-based hostsoverlays - Custom modifications to upstream packages.pkgs - Custom packages meant to be shared or upstreamed.
common - Custom packages that will work on either nixos or dariwnnixos - Custom packages specific to nixos-based hostsSecrets for this config are stored in a private repository called nix-secrets that is pulled in as a flake input and managed using the sops-nix tool.
For details on how this is accomplished, how to approach different scenarios, and troubleshooting for some common hurdles, please see my article and accompanying YouTube video NixOS Secrets Management available on my website. There is also a nix-secrets-reference repository that can be used in conjunction with the article.
Sincere thanks to all of my generous supporters!
If you find what I do helpful, please consider supporting my work using one of the links under "Sponsor this project" on the right-hand column of this page.
I intentionally keep all of my content ad-free but some platforms, such as YouTube, put ads on my videos outside of my control.
As with many personal projects, the code here tends to evolve away from what it was when the video/article content was published.
Videos - To find code relevant to when a specific video/article was published, look through tags with the word 'video' as they are commits from roughly the same time.
Darwin - To find relevant to handling hosts using both NixOS and Darwin, refer to the darwin branch. Starting in 2026, we are migrating away from Darwin support for the foreseeable future but will retain it 'as is' in the darwin branch for reference.
Those who have heavily influenced this strange journey into the unknown.
6,518 followers · starred May 2024
122 followers · starred Feb 2026
73 followers · starred Oct 2025
215 followers · starred Apr 2024