
Data on the share of ESM vs CJS on the public npm registry
JavaScript
252
59 commits
updated Jun 8, 2026
README
npm-esm-vs-cjs

Data on the share of ESM vs CJS on the public npm registry.
Contents
What is this?
This repository contains (historical) data on high-impact (popular) packages and what kind of code they expose:
- ESM — such as
type: 'module'inpackage.json - dual — such as both
importandrequireconditions in export map - faux ESM —
modulefield inpackage.json, supported by some old bundlers - CJS — anything else (except for
@types/*)
When should I use this?
Use this data for rough insights on how the shift to ESM is progressing. The data isn’t perfect though.
Data
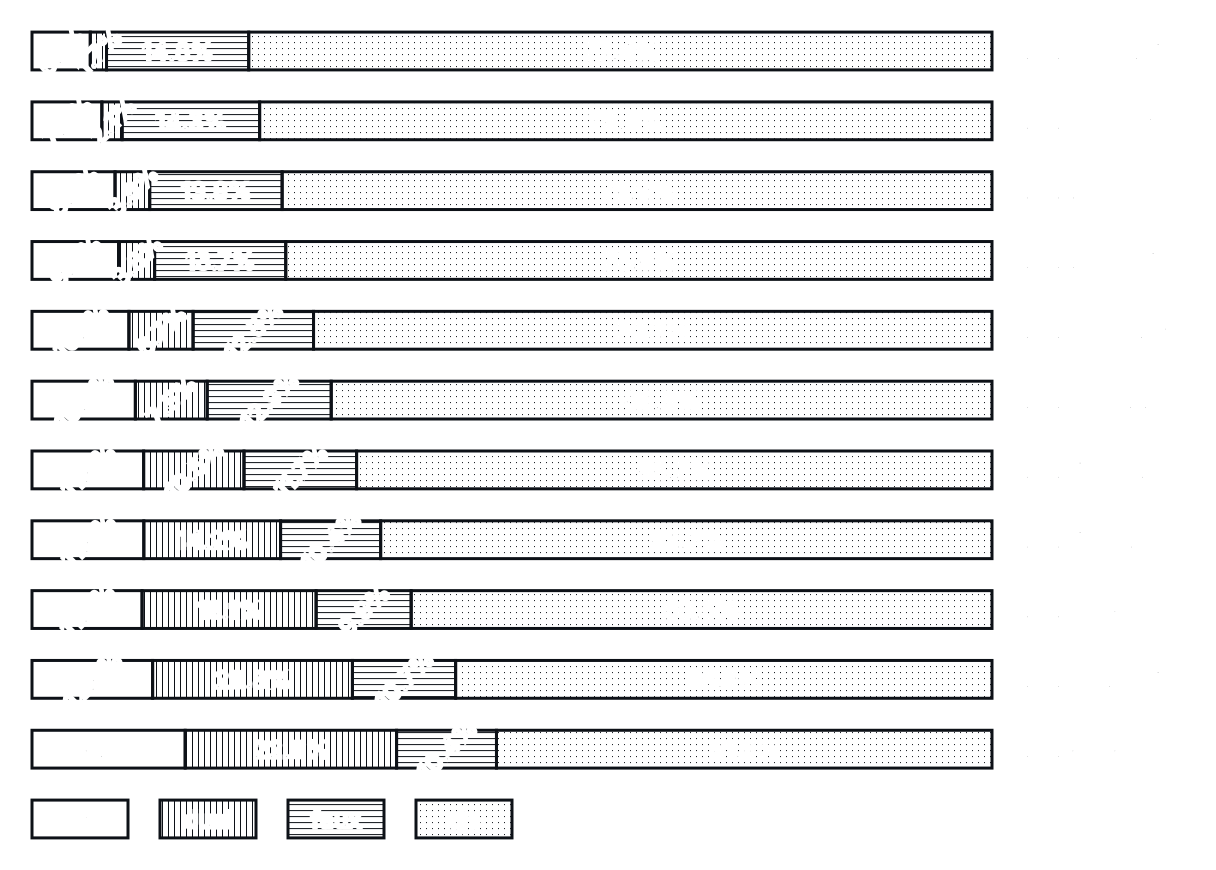
date,total,esm,dual,faux,cjs
2021-08-24,5617,341,95,832,4349
2021-11-09,5647,411,119,809,4308
2022-08-01,5734,496,207,791,4240
2022-11-04,5747,518,216,785,4228
2023-05-29,6240,630,417,783,4410
2023-11-22,6818,734,510,881,4693
2024-05-27,7042,819,736,826,4661
2024-11-27,8087,942,1152,843,5150
2025-06-05,8677,995,1573,859,5250
2025-12-04,14159,1779,2947,1522,7911
2026-06-08,16231,2590,3574,1689,8378
👉 Note: the crawl of
2025-12-04moves toecosyste.msfromlibraries.ioand npm itself, that gives a larger list of popular packages, particularly more packages that are depended on a lot.
👉 Note: the crawl of
2024-05-27adjusts several packages that were previously classified incorrectly as dual.
👉 Note: crawls from before
2022-11-04use the list of popular packages on the date of2022-11-04, as I had the results of all packages, but not which of them were popular back then. Later dates will use a list of what’s popular on that date.
👉 Note: not all of these packages are popular. There are some false-positives, such that download counts can be gamed, and that
libraries.iosometimes thinks that a fork of webpack or so is actually webpack.
👉 Note: while
@types/*packages are filtered out in the above counts, it is likely that there are other packages included that aren’t really code, particularly in the CJS category (as that’s the default).
Scripts
This repo includes scripts to crawl npm and analyze the results.
You need a NPM_TOKEN environment variable with a token to crawl npm.
script/crawl.js analyzes the package.json files of
latest releases of high-impact npm packages.
This script finishes in about 15 minutes.
You should likely first contribute to npm-high-impact though!
script/analyze.js analyzes the data files and
generates SVG and CSV files from them.
After running that,
please copy/paste the new .csv into this readme above.
Contribute
Yes please! See How to Contribute to Open Source.
Security
This package is safe.
License

Languages
JavaScript
100.0%
Data on the share of ESM vs CJS on the public npm registry
JavaScript
252
59 commits
updated Jun 8, 2026
README
npm-esm-vs-cjs
Data on the share of ESM vs CJS on the public npm registry.
Contents
What is this?
This repository contains (historical) data on high-impact (popular) packages and what kind of code they expose:
- ESM — such as
type: 'module'inpackage.json - dual — such as both
importandrequireconditions in export map - faux ESM —
modulefield inpackage.json, supported by some old bundlers - CJS — anything else (except for
@types/*)
When should I use this?
Use this data for rough insights on how the shift to ESM is progressing. The data isn’t perfect though.
Data
date,total,esm,dual,faux,cjs
2021-08-24,5617,341,95,832,4349
2021-11-09,5647,411,119,809,4308
2022-08-01,5734,496,207,791,4240
2022-11-04,5747,518,216,785,4228
2023-05-29,6240,630,417,783,4410
2023-11-22,6818,734,510,881,4693
2024-05-27,7042,819,736,826,4661
2024-11-27,8087,942,1152,843,5150
2025-06-05,8677,995,1573,859,5250
2025-12-04,14159,1779,2947,1522,7911
2026-06-08,16231,2590,3574,1689,8378
👉 Note: the crawl of
2025-12-04moves toecosyste.msfromlibraries.ioand npm itself, that gives a larger list of popular packages, particularly more packages that are depended on a lot.
👉 Note: the crawl of
2024-05-27adjusts several packages that were previously classified incorrectly as dual.
👉 Note: crawls from before
2022-11-04use the list of popular packages on the date of2022-11-04, as I had the results of all packages, but not which of them were popular back then. Later dates will use a list of what’s popular on that date.
👉 Note: not all of these packages are popular. There are some false-positives, such that download counts can be gamed, and that
libraries.iosometimes thinks that a fork of webpack or so is actually webpack.
👉 Note: while
@types/*packages are filtered out in the above counts, it is likely that there are other packages included that aren’t really code, particularly in the CJS category (as that’s the default).
Scripts
This repo includes scripts to crawl npm and analyze the results.
You need a NPM_TOKEN environment variable with a token to crawl npm.
script/crawl.js analyzes the package.json files of
latest releases of high-impact npm packages.
This script finishes in about 15 minutes.
You should likely first contribute to npm-high-impact though!
script/analyze.js analyzes the data files and
generates SVG and CSV files from them.
After running that,
please copy/paste the new .csv into this readme above.
Contribute
Yes please! See How to Contribute to Open Source.
Security
This package is safe.
License
Languages
JavaScript
100.0%