an SSO and OAuth / OIDC login solution for Nginx using the auth_request module
Go
3,284
970 commits
updated Sep 27, 2026


An SSO solution for Nginx using the auth_request module. Vouch Proxy can protect all of your websites at once.
Vouch Proxy supports many OAuth and OIDC login providers and can enforce authentication to...
Please do let us know when you have deployed Vouch Proxy with your preffered IdP or library so we can update the list.
If Vouch is running on the same host as the Nginx reverse proxy the response time from the /validate endpoint to Nginx should be less than 1ms.
Vouch Proxy (VP) forces visitors to login and authenticate with an IdP (such as one of the services listed above) before allowing them access to a website.
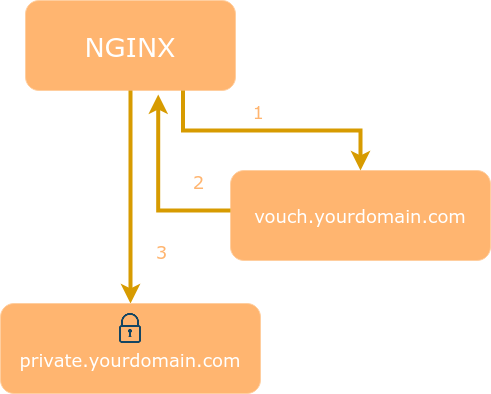
VP can also be used as a Single Sign On (SSO) solution to protect all web applications in the same domain.
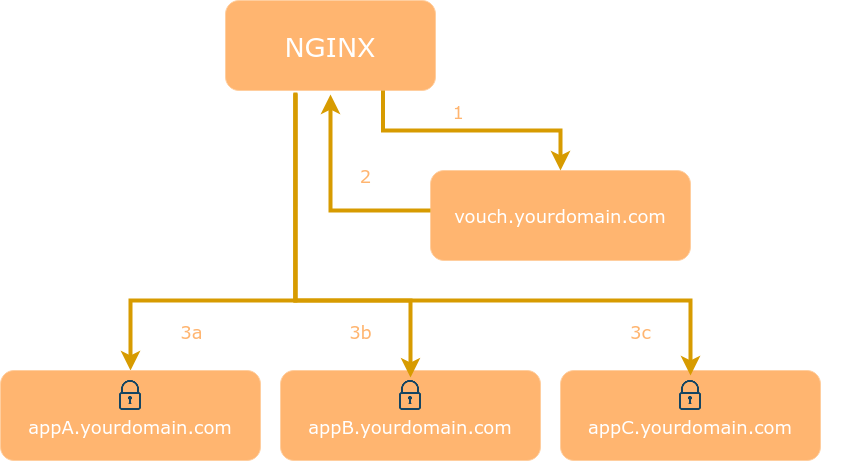
After a visitor logs in Vouch Proxy allows access to the protected websites for several hours. Every request is checked by VP to ensure that it is valid.
VP can send the visitor's email, name and other information which the IdP provides (including access tokens) to the web application as HTTP headers. VP can be used to replace application user management entirely.
Vouch Proxy relies on the ability to share a cookie between the Vouch Proxy server and the application it's protecting. Typically this will be done by running Vouch on a subdomain such as vouch.yourdomain.com with apps running at app1.yourdomain.com and app2.yourdomain.com. The protected domain is .yourdomain.com and the Vouch Proxy cookie must be set in this domain by setting vouch.domains to include yourdomain.com or sometimes by setting vouch.cookie.domain to yourdomain.com.
cp ./config/config.yml_example_$OAUTH_PROVIDER ./config/config.yml/auth endpointThe following Nginx config assumes..
vouch.yourdomain.com and protectedapp.yourdomain.com are running on the same serverhttps and have valid certs (if not, change to listen 80 and set vouch.cookie.secure to false)server {
listen 443 ssl http2;
server_name protectedapp.yourdomain.com;
root /var/www/html/;
ssl_certificate /etc/letsencrypt/live/protectedapp.yourdomain.com/fullchain.pem;
ssl_certificate_key /etc/letsencrypt/live/protectedapp.yourdomain.com/privkey.pem;
# send all requests to the `/validate` endpoint for authorization
auth_request /validate;
location = /validate {
# forward the /validate request to Vouch Proxy
proxy_pass http://127.0.0.1:9090/validate;
# be sure to pass the original host header
proxy_set_header Host $http_host;
# Vouch Proxy only acts on the request headers
proxy_pass_request_body off;
proxy_set_header Content-Length "";
# optionally add X-Vouch-User as returned by Vouch Proxy along with the request
auth_request_set $auth_resp_x_vouch_user $upstream_http_x_vouch_user;
# optionally add X-Vouch-IdP-Claims-* custom claims you are tracking
# auth_request_set $auth_resp_x_vouch_idp_claims_groups $upstream_http_x_vouch_idp_claims_groups;
# auth_request_set $auth_resp_x_vouch_idp_claims_given_name $upstream_http_x_vouch_idp_claims_given_name;
# optinally add X-Vouch-IdP-AccessToken or X-Vouch-IdP-IdToken
# auth_request_set $auth_resp_x_vouch_idp_accesstoken $upstream_http_x_vouch_idp_accesstoken;
# auth_request_set $auth_resp_x_vouch_idp_idtoken $upstream_http_x_vouch_idp_idtoken;
# these return values are used by the @error401 call
auth_request_set $auth_resp_jwt $upstream_http_x_vouch_jwt;
auth_request_set $auth_resp_err $upstream_http_x_vouch_err;
auth_request_set $auth_resp_failcount $upstream_http_x_vouch_failcount;
# Vouch Proxy can run behind the same Nginx reverse proxy
# may need to comply to "upstream" server naming
# proxy_pass http://vouch.yourdomain.com/validate;
# proxy_set_header Host $http_host;
}
# if validate returns `401 not authorized` then forward the request to the error401block
error_page 401 = @error401;
location @error401 {
# redirect to Vouch Proxy for login
return 302 https://vouch.yourdomain.com/login?url=$scheme://$http_host$request_uri&vouch-failcount=$auth_resp_failcount&X-Vouch-Token=$auth_resp_jwt&error=$auth_resp_err;
# you usually *want* to redirect to Vouch running behind the same Nginx config proteced by https
# but to get started you can just forward the end user to the port that vouch is running on
# return 302 http://vouch.yourdomain.com:9090/login?url=$scheme://$http_host$request_uri&vouch-failcount=$auth_resp_failcount&X-Vouch-Token=$auth_resp_jwt&error=$auth_resp_err;
}
location / {
# forward authorized requests to your service protectedapp.yourdomain.com
proxy_pass http://127.0.0.1:8080;
# you may need to set these variables in this block as per https://github.com/vouch/vouch-proxy/issues/26#issuecomment-425215810
# auth_request_set $auth_resp_x_vouch_user $upstream_http_x_vouch_user;
# auth_request_set $auth_resp_x_vouch_idp_claims_groups $upstream_http_x_vouch_idp_claims_groups;
# auth_request_set $auth_resp_x_vouch_idp_claims_given_name $upstream_http_x_vouch_idp_claims_given_name;
# set user header (usually an email)
proxy_set_header X-Vouch-User $auth_resp_x_vouch_user;
# optionally pass any custom claims you are tracking
# proxy_set_header X-Vouch-IdP-Claims-Groups $auth_resp_x_vouch_idp_claims_groups;
# proxy_set_header X-Vouch-IdP-Claims-Given_Name $auth_resp_x_vouch_idp_claims_given_name;
# optionally pass the accesstoken or idtoken
# proxy_set_header X-Vouch-IdP-AccessToken $auth_resp_x_vouch_idp_accesstoken;
# proxy_set_header X-Vouch-IdP-IdToken $auth_resp_x_vouch_idp_idtoken;
}
}
If Vouch is configured behind the same nginx reverseproxy (perhaps so you can configure ssl) be sure to pass the Host header properly, otherwise the JWT cookie cannot be set into the domain
server {
    listen 443 ssl http2;
    server_name vouch.yourdomain.com;
    ssl_certificate /etc/letsencrypt/live/vouch.yourdomain.com/fullchain.pem;
    ssl_certificate_key /etc/letsencrypt/live/vouch.yourdomain.com/privkey.pem;

    location / {
      proxy_pass http://127.0.0.1:9090;
      # be sure to pass the original host header
      proxy_set_header Host $http_host;
    }
}
As of v0.33.0 Vouch Proxy can be served within an Nginx location (path) by configuring vouch.document_root: /vp_in_a_path
This avoids the need to setup a separate domain for Vouch Proxy such as vouch.yourdomain.com. For example VP login will be served from https://protectedapp.yourdomain.com/vp_in_a_path/login
server {
    listen 443 ssl http2;
    server_name protectedapp.yourdomain.com;

    ssl_certificate /etc/letsencrypt/live/protectedapp.yourdomain.com/fullchain.pem;
    ssl_certificate_key /etc/letsencrypt/live/protectedapp.yourdomain.com/privkey.pem;

    # This location serves all Vouch Proxy endpoints as /vp_in_a_path/$uri
    #   including /vp_in_a_path/validate, /vp_in_a_path/login, /vp_in_a_path/logout, /vp_in_a_path/auth, /vp_in_a_path/auth/$STATE, etc
    location /vp_in_a_path {
      proxy_pass http://127.0.0.1:9090; # must not! have a slash at the end
      proxy_set_header Host $http_host;
      proxy_pass_request_body off;
      proxy_set_header Content-Length "";

      # these return values are used by the @error401 call
      auth_request_set $auth_resp_jwt $upstream_http_x_vouch_jwt;
      auth_request_set $auth_resp_err $upstream_http_x_vouch_err;
      auth_request_set $auth_resp_failcount $upstream_http_x_vouch_failcount;
    }

    # if /vp_in_a_path/validate returns `401 not authorized` then forward the request to the error401block
    error_page 401 = @error401;

    location @error401 {
        # redirect to Vouch Proxy for login
        return 302 https://protectedapp.yourdomain.com/vp_in_a_path/login?url=$scheme://$http_host$request_uri&vouch-failcount=$auth_resp_failcount&X-Vouch-Token=$auth_resp_jwt&error=$auth_resp_err;
    }

    location / {
      auth_request /vp_in_a_path/validate;
      proxy_pass http://127.0.0.1:8080;
      # see the Nginx config above for additional headers which can be set from Vouch Proxy
    }
}
Additional Nginx configurations can be found in the examples directory.
Here's a minimal setup using Google's OAuth...
VOUCH_DOMAINS=yourdomain.com \
  OAUTH_PROVIDER=google \
  OAUTH_CLIENT_ID=1234 \
  OAUTH_CLIENT_SECRET=secretsecret \
  OAUTH_CALLBACK_URL=https://vouch.yourdomain.com/auth \
  ./vouch-proxy
Environmental variable names are documented in config/config.yml_example
All lists with multiple values must be comma separated: VOUCH_DOMAINS="yourdomain.com,yourotherdomain.com"
The variable VOUCH_CONFIG can be used to set an alternate location for the configuration file. VOUCH_ROOT can be used to set an alternate root directory for Vouch Proxy to look for support files.
All Vouch Proxy configuration items are documented in config/config.yml_example
/validate response in NginxOPTIONS requests when protecting an API with Vouch ProxyHTTP_PROXY to relay Vouch Proxy IdP requests through an outbound proxy serversystemd startup of Vouch Proxysatisfy any;Please do help us to expand this list.
With Vouch Proxy you can request various scopes (standard and custom) to obtain more information about the user or gain access to the provider's APIs. Internally, Vouch Proxy launches a requests to user_info_url after successful authentication. The required claims are extracted from the provider's response and stored in the VP cookie.
⚠️ Additional claims and tokens will be added to the VP cookie and can make it large
The VP cookie may be split into several cookies to accomdate browser cookie size limits. But if you need it, you need it. Large cookies and headers require Nginx to be configured with larger buffers. See large_client_header_buffers and proxy_buffer_size for more information.
scopes and claims in Vouch Proxy with NginxConfigure Vouch Proxy for Nginx and your IdP as normal (See: Installation and Configuration)
Set the necessary scopes in the oauth section of the vouch-proxy config.yml (example config)
idtoken: X-Vouch-IdP-IdToken in the headers section of vouch-proxy's config.yml/validate endpoint in a modern browserX-Vouch-IdP-IdToken headerscopes in the oauth section of your config.yml or reconfigure your oauth providerSet the necessary claims in the header section of the vouch-proxy config.yml
/validate endpoint in a modern browserX-Vouch-IdP-Claims-<ClaimName>idtoken: X-Vouch-IdP-IdToken from the headers section of vouch-proxy's config.yml if you don't need itUse auth_request_set after auth_request inside the protected location in the nginx server.conf
Consume the claim (example nginx config)
docker run -d \
    -p 9090:9090 \
    --name vouch-proxy \
    -v ${PWD}/config:/config \
    quay.io/vouch/vouch-proxy
or
docker run -d \
    -p 9090:9090 \
    --name vouch-proxy \
    -e VOUCH_DOMAINS=yourdomain.com \
    -e OAUTH_PROVIDER=google \
    -e OAUTH_CLIENT_ID=1234 \
    -e OAUTH_CLIENT_SECRET=secretsecret \
    -e OAUTH_CALLBACK_URL=https://vouch.yourdomain.com/auth \
    quay.io/vouch/vouch-proxy
As of v0.36.0 the docker process in the container runs as user vouch with UID 999 and GID 999. You may need to set the permissions of /config/config.yml and /config/secret to correspond to be readable by this user, or otherwise use docker run --user $UID:$GID ... or perhaps build the docker container from source and use the available ARGs for UID and GID.
Automated container builds for each Vouch Proxy release are available from quay.io. Each release produces..
a minimal go binary container built from Dockerfile
quay.io/vouch/vouch-proxy:latestquay.io/vouch/vouch-proxy:x.y.z such as quay.io/vouch/vouch-proxy:0.28.0an alpine based container built from Dockerfile.alpine
quay.io/vouch/vouch-proxy:alpine-latestquay.io/vouch/vouch-proxy:alpine-x.y.zAs of v0.43.0 both of these images are Multi-platform builds supporting linux/amd64 and linux/arm64.
Vouch Proxy arm images are available on Docker Hub
voucher/vouch-proxy:latest-armIf you are using kubernetes with nginx-ingress, you can configure your ingress with the following annotations (note quoting the auth-signin annotation):
    nginx.ingress.kubernetes.io/auth-signin: "https://vouch.yourdomain.com/login?url=$scheme://$http_host$request_uri&vouch-failcount=$auth_resp_failcount&X-Vouch-Token=$auth_resp_jwt&error=$auth_resp_err"
    nginx.ingress.kubernetes.io/auth-url: https://vouch.yourdomain.com/validate
    nginx.ingress.kubernetes.io/auth-response-headers: X-Vouch-User
    nginx.ingress.kubernetes.io/auth-snippet: |
      # these return values are used by the @error401 call
      auth_request_set $auth_resp_jwt $upstream_http_x_vouch_jwt;
      auth_request_set $auth_resp_err $upstream_http_x_vouch_err;
      auth_request_set $auth_resp_failcount $upstream_http_x_vouch_failcount;
      # when VP is hosted externally to k8s ensure the SSL cert is valid to avoid MITM risk
      # proxy_ssl_trusted_certificate /etc/ssl/certs/ca-certificates.crt;
      # proxy_ssl_session_reuse on;
      # proxy_ssl_verify_depth 2;
      # proxy_ssl_verify on;
Helm Charts are maintained by punkle, martina-if and halkeye and are available at https://github.com/vouch/helm-charts
  ./do.sh goget
  ./do.sh build
  ./vouch-proxy
As of v0.29.0 all templates, static assets and configuration defaults in .defaults.yml are built into the static binary using go:embed directives.
As of v0.11.0 additional checks are in place to reduce the attack surface of url redirection.
The passed URL...
http or httpsvouch.domains list or the vouch.cookie.domain (if either of those are configured)The Vouch Proxy /logout endpoint accepts a url parameter in the query string which can be used to 302 redirect a user to your orignal OAuth provider/IDP/OIDC provider's revocation_endpoint
https://vouch.oursites.com/logout?url=https://oauth2.googleapis.com/revoke
this url must be present in the configuration file on the list vouch.post_logout_redirect_uris
# in order to prevent redirection attacks all redirected URLs to /logout must be specified
# the URL must still be passed to Vouch Proxy as https://vouch.yourdomain.com/logout?url=${ONE OF THE URLS BELOW}
post_logout_redirect_uris:
  # your apps login page
  - https://yourdomain.com/login
  # your IdPs logout enpoint
  # from https://accounts.google.com/.well-known/openid-configuration
  - https://oauth2.googleapis.com/revoke
  # you may be daisy chaining to your IdP
  - https://myorg.okta.com/oauth2/123serverid/v1/logout?post_logout_redirect_uri=http://myapp.yourdomain.com/login
Note that your IdP will likely carry their own, separate post_logout_redirect_uri list.
logout resources..
Getting the stars to align between Nginx, Vouch Proxy and your IdP can be tricky. We want to help you get up and running as quickly as possible. The most common problem is..
Double check that you are running Vouch Proxy and your apps on a common domain that can share cookies. For example, vouch.yourdomain.com and app.yourdomain.com can share cookies on the .yourdomain.com domain. (It will not work if you are trying to use vouch.yourdomain.org and app.yourdomain.net.)
You may need to explicitly define the domain that the cookie should be set on. You can do this in the config file by setting the option:
vouch:
  cookie:
    # force the domain of the cookie to set
    domain: yourdomain.com
If you continue to have trouble, try the following:
turn on vouch.testing: true. This will slow down the loop.
set vouch.logLevel: debug.
the Host: header in the http request, the oauth.callback_url and the configured vouch.domains must all align so that the cookie that carries the JWT can be placed properly into the browser and then returned on each request
it helps to think like a cookie.
siteA.yourdomain.com and siteB.yourdomain.com protected by Vouch Proxy, you want the Vouch Proxy cookie to be set into .yourdomain.comvouch.yourdomain.com the cookie will not be able to be seen by dev.anythingelse.comvouch.cookie.secure: falseplease see the issues which have been closed that mention redirect
Please submit a new issue in the following fashion..
TLDR:
vouch.testing: truevouch.logLevel: debug./vouch-proxy capturing the output..
/validate/login - even if the error is here/auth/validate - capture everythinggist../do.sh bug_report is your friendvouch.testing: true and set vouch.logLevel: debug../do.sh bug_report secretdomain.com secretpass [anothersecret..] which will create a redacted version of your config and logs removing each of those strings
A bug report can be generated from a docker environment using the quay.io/vouch/vouch-proxy:alpine image...
docker run --name vouch_proxy -v $PWD/config:/config -v $PWD/certs:/certs -it --rm --entrypoint /do.sh quay.io/vouch/vouch-proxy:alpine bug_report yourdomain.com anotherdomain.com someothersecret
We'd love to have you contribute! Please refer to our contribution guidelines for details.
OpenResty® is a full-fledged web platform that integrates the standard Nginx core, LuaJIT, many carefully written Lua libraries, lots of high quality 3rd-party Nginx modules, and most of their external dependencies.
You can replace nginx with OpenResty fairly easily.
With OpenResty and Lua it is possible to provide customized and advanced authorization on any header or claims vouch passes down.
OpenResty and configs for a variety of scenarios are available in the examples directory.
Bob visits https://private.oursites.com
the Nginx reverse proxy...
auth_request module configured for the /validate path/validate is configured to proxy_pass requests to the authentication service at https://vouch.oursites.com/validate
/validate returns...
https://vouch.oursites.com/login?url=https://private.oursites.comVouch Proxy https://vouch.oursites.com/validate
proxy_pass200 OK to Nginx, which will allow access (bob notices nothing)401 NotAuthorized to Nginx (which forwards the request on to login)Bob is first forwarded briefly to https://vouch.oursites.com/login?url=https://private.oursites.com
https://private.oursites.com from the query string in session variable $requestedURL$STATE nonceBob logs into his Google account using Oauth
https://vouch.oursites.com/auth?state=$STATEBob is forwarded to https://vouch.oursites.com/auth?state=$STATE
$requestedURL and 302 redirect bob back to https://private.oursites.comNote that outside of some innocuos redirection, Bob only ever sees https://private.oursites.com and the Google Login screen in his browser. While Vouch does interact with Bob's browser several times, it is just to set cookies, and if the 302 redirects work properly Bob will log in quickly.
Once the JWT is set, Bob will be authorized for all other sites which are configured to use https://vouch.oursites.com/validate from the auth_request Nginx module.
The next time Bob is forwarded to google for login, since he has already authorized the Vouch Proxy OAuth app, Google immediately forwards him back and sets the cookie and sends him on his merry way. In some browsers such as Chrome, Bob may not even notice that he logged in using Vouch Proxy.
Overall
Maintained
Code review
Go module
Latest release
Releases this year
(top 24 of 51)
140 followers · starred May 2022
119 followers · starred Mar 2023
2,910 followers · starred Apr 2023
32 followers · starred Oct 2025
an SSO and OAuth / OIDC login solution for Nginx using the auth_request module
Go
3,284
970 commits
updated Sep 27, 2026
An SSO solution for Nginx using the auth_request module. Vouch Proxy can protect all of your websites at once.
Vouch Proxy supports many OAuth and OIDC login providers and can enforce authentication to...
Please do let us know when you have deployed Vouch Proxy with your preffered IdP or library so we can update the list.
If Vouch is running on the same host as the Nginx reverse proxy the response time from the /validate endpoint to Nginx should be less than 1ms.
Vouch Proxy (VP) forces visitors to login and authenticate with an IdP (such as one of the services listed above) before allowing them access to a website.
VP can also be used as a Single Sign On (SSO) solution to protect all web applications in the same domain.
After a visitor logs in Vouch Proxy allows access to the protected websites for several hours. Every request is checked by VP to ensure that it is valid.
VP can send the visitor's email, name and other information which the IdP provides (including access tokens) to the web application as HTTP headers. VP can be used to replace application user management entirely.
Vouch Proxy relies on the ability to share a cookie between the Vouch Proxy server and the application it's protecting. Typically this will be done by running Vouch on a subdomain such as vouch.yourdomain.com with apps running at app1.yourdomain.com and app2.yourdomain.com. The protected domain is .yourdomain.com and the Vouch Proxy cookie must be set in this domain by setting vouch.domains to include yourdomain.com or sometimes by setting vouch.cookie.domain to yourdomain.com.
cp ./config/config.yml_example_$OAUTH_PROVIDER ./config/config.yml/auth endpointThe following Nginx config assumes..
vouch.yourdomain.com and protectedapp.yourdomain.com are running on the same serverhttps and have valid certs (if not, change to listen 80 and set vouch.cookie.secure to false)server {
listen 443 ssl http2;
server_name protectedapp.yourdomain.com;
root /var/www/html/;
ssl_certificate /etc/letsencrypt/live/protectedapp.yourdomain.com/fullchain.pem;
ssl_certificate_key /etc/letsencrypt/live/protectedapp.yourdomain.com/privkey.pem;
# send all requests to the `/validate` endpoint for authorization
auth_request /validate;
location = /validate {
# forward the /validate request to Vouch Proxy
proxy_pass http://127.0.0.1:9090/validate;
# be sure to pass the original host header
proxy_set_header Host $http_host;
# Vouch Proxy only acts on the request headers
proxy_pass_request_body off;
proxy_set_header Content-Length "";
# optionally add X-Vouch-User as returned by Vouch Proxy along with the request
auth_request_set $auth_resp_x_vouch_user $upstream_http_x_vouch_user;
# optionally add X-Vouch-IdP-Claims-* custom claims you are tracking
# auth_request_set $auth_resp_x_vouch_idp_claims_groups $upstream_http_x_vouch_idp_claims_groups;
# auth_request_set $auth_resp_x_vouch_idp_claims_given_name $upstream_http_x_vouch_idp_claims_given_name;
# optinally add X-Vouch-IdP-AccessToken or X-Vouch-IdP-IdToken
# auth_request_set $auth_resp_x_vouch_idp_accesstoken $upstream_http_x_vouch_idp_accesstoken;
# auth_request_set $auth_resp_x_vouch_idp_idtoken $upstream_http_x_vouch_idp_idtoken;
# these return values are used by the @error401 call
auth_request_set $auth_resp_jwt $upstream_http_x_vouch_jwt;
auth_request_set $auth_resp_err $upstream_http_x_vouch_err;
auth_request_set $auth_resp_failcount $upstream_http_x_vouch_failcount;
# Vouch Proxy can run behind the same Nginx reverse proxy
# may need to comply to "upstream" server naming
# proxy_pass http://vouch.yourdomain.com/validate;
# proxy_set_header Host $http_host;
}
# if validate returns `401 not authorized` then forward the request to the error401block
error_page 401 = @error401;
location @error401 {
# redirect to Vouch Proxy for login
return 302 https://vouch.yourdomain.com/login?url=$scheme://$http_host$request_uri&vouch-failcount=$auth_resp_failcount&X-Vouch-Token=$auth_resp_jwt&error=$auth_resp_err;
# you usually *want* to redirect to Vouch running behind the same Nginx config proteced by https
# but to get started you can just forward the end user to the port that vouch is running on
# return 302 http://vouch.yourdomain.com:9090/login?url=$scheme://$http_host$request_uri&vouch-failcount=$auth_resp_failcount&X-Vouch-Token=$auth_resp_jwt&error=$auth_resp_err;
}
location / {
# forward authorized requests to your service protectedapp.yourdomain.com
proxy_pass http://127.0.0.1:8080;
# you may need to set these variables in this block as per https://github.com/vouch/vouch-proxy/issues/26#issuecomment-425215810
# auth_request_set $auth_resp_x_vouch_user $upstream_http_x_vouch_user;
# auth_request_set $auth_resp_x_vouch_idp_claims_groups $upstream_http_x_vouch_idp_claims_groups;
# auth_request_set $auth_resp_x_vouch_idp_claims_given_name $upstream_http_x_vouch_idp_claims_given_name;
# set user header (usually an email)
proxy_set_header X-Vouch-User $auth_resp_x_vouch_user;
# optionally pass any custom claims you are tracking
# proxy_set_header X-Vouch-IdP-Claims-Groups $auth_resp_x_vouch_idp_claims_groups;
# proxy_set_header X-Vouch-IdP-Claims-Given_Name $auth_resp_x_vouch_idp_claims_given_name;
# optionally pass the accesstoken or idtoken
# proxy_set_header X-Vouch-IdP-AccessToken $auth_resp_x_vouch_idp_accesstoken;
# proxy_set_header X-Vouch-IdP-IdToken $auth_resp_x_vouch_idp_idtoken;
}
}
If Vouch is configured behind the same nginx reverseproxy (perhaps so you can configure ssl) be sure to pass the Host header properly, otherwise the JWT cookie cannot be set into the domain
server {
    listen 443 ssl http2;
    server_name vouch.yourdomain.com;
    ssl_certificate /etc/letsencrypt/live/vouch.yourdomain.com/fullchain.pem;
    ssl_certificate_key /etc/letsencrypt/live/vouch.yourdomain.com/privkey.pem;

    location / {
      proxy_pass http://127.0.0.1:9090;
      # be sure to pass the original host header
      proxy_set_header Host $http_host;
    }
}
As of v0.33.0 Vouch Proxy can be served within an Nginx location (path) by configuring vouch.document_root: /vp_in_a_path
This avoids the need to setup a separate domain for Vouch Proxy such as vouch.yourdomain.com. For example VP login will be served from https://protectedapp.yourdomain.com/vp_in_a_path/login
server {
    listen 443 ssl http2;
    server_name protectedapp.yourdomain.com;

    ssl_certificate /etc/letsencrypt/live/protectedapp.yourdomain.com/fullchain.pem;
    ssl_certificate_key /etc/letsencrypt/live/protectedapp.yourdomain.com/privkey.pem;

    # This location serves all Vouch Proxy endpoints as /vp_in_a_path/$uri
    #   including /vp_in_a_path/validate, /vp_in_a_path/login, /vp_in_a_path/logout, /vp_in_a_path/auth, /vp_in_a_path/auth/$STATE, etc
    location /vp_in_a_path {
      proxy_pass http://127.0.0.1:9090; # must not! have a slash at the end
      proxy_set_header Host $http_host;
      proxy_pass_request_body off;
      proxy_set_header Content-Length "";

      # these return values are used by the @error401 call
      auth_request_set $auth_resp_jwt $upstream_http_x_vouch_jwt;
      auth_request_set $auth_resp_err $upstream_http_x_vouch_err;
      auth_request_set $auth_resp_failcount $upstream_http_x_vouch_failcount;
    }

    # if /vp_in_a_path/validate returns `401 not authorized` then forward the request to the error401block
    error_page 401 = @error401;

    location @error401 {
        # redirect to Vouch Proxy for login
        return 302 https://protectedapp.yourdomain.com/vp_in_a_path/login?url=$scheme://$http_host$request_uri&vouch-failcount=$auth_resp_failcount&X-Vouch-Token=$auth_resp_jwt&error=$auth_resp_err;
    }

    location / {
      auth_request /vp_in_a_path/validate;
      proxy_pass http://127.0.0.1:8080;
      # see the Nginx config above for additional headers which can be set from Vouch Proxy
    }
}
Additional Nginx configurations can be found in the examples directory.
Here's a minimal setup using Google's OAuth...
VOUCH_DOMAINS=yourdomain.com \
  OAUTH_PROVIDER=google \
  OAUTH_CLIENT_ID=1234 \
  OAUTH_CLIENT_SECRET=secretsecret \
  OAUTH_CALLBACK_URL=https://vouch.yourdomain.com/auth \
  ./vouch-proxy
Environmental variable names are documented in config/config.yml_example
All lists with multiple values must be comma separated: VOUCH_DOMAINS="yourdomain.com,yourotherdomain.com"
The variable VOUCH_CONFIG can be used to set an alternate location for the configuration file. VOUCH_ROOT can be used to set an alternate root directory for Vouch Proxy to look for support files.
All Vouch Proxy configuration items are documented in config/config.yml_example
/validate response in NginxOPTIONS requests when protecting an API with Vouch ProxyHTTP_PROXY to relay Vouch Proxy IdP requests through an outbound proxy serversystemd startup of Vouch Proxysatisfy any;Please do help us to expand this list.
With Vouch Proxy you can request various scopes (standard and custom) to obtain more information about the user or gain access to the provider's APIs. Internally, Vouch Proxy launches a requests to user_info_url after successful authentication. The required claims are extracted from the provider's response and stored in the VP cookie.
⚠️ Additional claims and tokens will be added to the VP cookie and can make it large
The VP cookie may be split into several cookies to accomdate browser cookie size limits. But if you need it, you need it. Large cookies and headers require Nginx to be configured with larger buffers. See large_client_header_buffers and proxy_buffer_size for more information.
scopes and claims in Vouch Proxy with NginxConfigure Vouch Proxy for Nginx and your IdP as normal (See: Installation and Configuration)
Set the necessary scopes in the oauth section of the vouch-proxy config.yml (example config)
idtoken: X-Vouch-IdP-IdToken in the headers section of vouch-proxy's config.yml/validate endpoint in a modern browserX-Vouch-IdP-IdToken headerscopes in the oauth section of your config.yml or reconfigure your oauth providerSet the necessary claims in the header section of the vouch-proxy config.yml
/validate endpoint in a modern browserX-Vouch-IdP-Claims-<ClaimName>idtoken: X-Vouch-IdP-IdToken from the headers section of vouch-proxy's config.yml if you don't need itUse auth_request_set after auth_request inside the protected location in the nginx server.conf
Consume the claim (example nginx config)
docker run -d \
    -p 9090:9090 \
    --name vouch-proxy \
    -v ${PWD}/config:/config \
    quay.io/vouch/vouch-proxy
or
docker run -d \
    -p 9090:9090 \
    --name vouch-proxy \
    -e VOUCH_DOMAINS=yourdomain.com \
    -e OAUTH_PROVIDER=google \
    -e OAUTH_CLIENT_ID=1234 \
    -e OAUTH_CLIENT_SECRET=secretsecret \
    -e OAUTH_CALLBACK_URL=https://vouch.yourdomain.com/auth \
    quay.io/vouch/vouch-proxy
As of v0.36.0 the docker process in the container runs as user vouch with UID 999 and GID 999. You may need to set the permissions of /config/config.yml and /config/secret to correspond to be readable by this user, or otherwise use docker run --user $UID:$GID ... or perhaps build the docker container from source and use the available ARGs for UID and GID.
Automated container builds for each Vouch Proxy release are available from quay.io. Each release produces..
a minimal go binary container built from Dockerfile
quay.io/vouch/vouch-proxy:latestquay.io/vouch/vouch-proxy:x.y.z such as quay.io/vouch/vouch-proxy:0.28.0an alpine based container built from Dockerfile.alpine
quay.io/vouch/vouch-proxy:alpine-latestquay.io/vouch/vouch-proxy:alpine-x.y.zAs of v0.43.0 both of these images are Multi-platform builds supporting linux/amd64 and linux/arm64.
Vouch Proxy arm images are available on Docker Hub
voucher/vouch-proxy:latest-armIf you are using kubernetes with nginx-ingress, you can configure your ingress with the following annotations (note quoting the auth-signin annotation):
    nginx.ingress.kubernetes.io/auth-signin: "https://vouch.yourdomain.com/login?url=$scheme://$http_host$request_uri&vouch-failcount=$auth_resp_failcount&X-Vouch-Token=$auth_resp_jwt&error=$auth_resp_err"
    nginx.ingress.kubernetes.io/auth-url: https://vouch.yourdomain.com/validate
    nginx.ingress.kubernetes.io/auth-response-headers: X-Vouch-User
    nginx.ingress.kubernetes.io/auth-snippet: |
      # these return values are used by the @error401 call
      auth_request_set $auth_resp_jwt $upstream_http_x_vouch_jwt;
      auth_request_set $auth_resp_err $upstream_http_x_vouch_err;
      auth_request_set $auth_resp_failcount $upstream_http_x_vouch_failcount;
      # when VP is hosted externally to k8s ensure the SSL cert is valid to avoid MITM risk
      # proxy_ssl_trusted_certificate /etc/ssl/certs/ca-certificates.crt;
      # proxy_ssl_session_reuse on;
      # proxy_ssl_verify_depth 2;
      # proxy_ssl_verify on;
Helm Charts are maintained by punkle, martina-if and halkeye and are available at https://github.com/vouch/helm-charts
  ./do.sh goget
  ./do.sh build
  ./vouch-proxy
As of v0.29.0 all templates, static assets and configuration defaults in .defaults.yml are built into the static binary using go:embed directives.
As of v0.11.0 additional checks are in place to reduce the attack surface of url redirection.
The passed URL...
http or httpsvouch.domains list or the vouch.cookie.domain (if either of those are configured)The Vouch Proxy /logout endpoint accepts a url parameter in the query string which can be used to 302 redirect a user to your orignal OAuth provider/IDP/OIDC provider's revocation_endpoint
https://vouch.oursites.com/logout?url=https://oauth2.googleapis.com/revoke
this url must be present in the configuration file on the list vouch.post_logout_redirect_uris
# in order to prevent redirection attacks all redirected URLs to /logout must be specified
# the URL must still be passed to Vouch Proxy as https://vouch.yourdomain.com/logout?url=${ONE OF THE URLS BELOW}
post_logout_redirect_uris:
  # your apps login page
  - https://yourdomain.com/login
  # your IdPs logout enpoint
  # from https://accounts.google.com/.well-known/openid-configuration
  - https://oauth2.googleapis.com/revoke
  # you may be daisy chaining to your IdP
  - https://myorg.okta.com/oauth2/123serverid/v1/logout?post_logout_redirect_uri=http://myapp.yourdomain.com/login
Note that your IdP will likely carry their own, separate post_logout_redirect_uri list.
logout resources..
Getting the stars to align between Nginx, Vouch Proxy and your IdP can be tricky. We want to help you get up and running as quickly as possible. The most common problem is..
Double check that you are running Vouch Proxy and your apps on a common domain that can share cookies. For example, vouch.yourdomain.com and app.yourdomain.com can share cookies on the .yourdomain.com domain. (It will not work if you are trying to use vouch.yourdomain.org and app.yourdomain.net.)
You may need to explicitly define the domain that the cookie should be set on. You can do this in the config file by setting the option:
vouch:
  cookie:
    # force the domain of the cookie to set
    domain: yourdomain.com
If you continue to have trouble, try the following:
turn on vouch.testing: true. This will slow down the loop.
set vouch.logLevel: debug.
the Host: header in the http request, the oauth.callback_url and the configured vouch.domains must all align so that the cookie that carries the JWT can be placed properly into the browser and then returned on each request
it helps to think like a cookie.
siteA.yourdomain.com and siteB.yourdomain.com protected by Vouch Proxy, you want the Vouch Proxy cookie to be set into .yourdomain.comvouch.yourdomain.com the cookie will not be able to be seen by dev.anythingelse.comvouch.cookie.secure: falseplease see the issues which have been closed that mention redirect
Please submit a new issue in the following fashion..
TLDR:
vouch.testing: truevouch.logLevel: debug./vouch-proxy capturing the output..
/validate/login - even if the error is here/auth/validate - capture everythinggist../do.sh bug_report is your friendvouch.testing: true and set vouch.logLevel: debug../do.sh bug_report secretdomain.com secretpass [anothersecret..] which will create a redacted version of your config and logs removing each of those strings
A bug report can be generated from a docker environment using the quay.io/vouch/vouch-proxy:alpine image...
docker run --name vouch_proxy -v $PWD/config:/config -v $PWD/certs:/certs -it --rm --entrypoint /do.sh quay.io/vouch/vouch-proxy:alpine bug_report yourdomain.com anotherdomain.com someothersecret
We'd love to have you contribute! Please refer to our contribution guidelines for details.
OpenResty® is a full-fledged web platform that integrates the standard Nginx core, LuaJIT, many carefully written Lua libraries, lots of high quality 3rd-party Nginx modules, and most of their external dependencies.
You can replace nginx with OpenResty fairly easily.
With OpenResty and Lua it is possible to provide customized and advanced authorization on any header or claims vouch passes down.
OpenResty and configs for a variety of scenarios are available in the examples directory.
Bob visits https://private.oursites.com
the Nginx reverse proxy...
auth_request module configured for the /validate path/validate is configured to proxy_pass requests to the authentication service at https://vouch.oursites.com/validate
/validate returns...
https://vouch.oursites.com/login?url=https://private.oursites.comVouch Proxy https://vouch.oursites.com/validate
proxy_pass200 OK to Nginx, which will allow access (bob notices nothing)401 NotAuthorized to Nginx (which forwards the request on to login)Bob is first forwarded briefly to https://vouch.oursites.com/login?url=https://private.oursites.com
https://private.oursites.com from the query string in session variable $requestedURL$STATE nonceBob logs into his Google account using Oauth
https://vouch.oursites.com/auth?state=$STATEBob is forwarded to https://vouch.oursites.com/auth?state=$STATE
$requestedURL and 302 redirect bob back to https://private.oursites.comNote that outside of some innocuos redirection, Bob only ever sees https://private.oursites.com and the Google Login screen in his browser. While Vouch does interact with Bob's browser several times, it is just to set cookies, and if the 302 redirects work properly Bob will log in quickly.
Once the JWT is set, Bob will be authorized for all other sites which are configured to use https://vouch.oursites.com/validate from the auth_request Nginx module.
The next time Bob is forwarded to google for login, since he has already authorized the Vouch Proxy OAuth app, Google immediately forwards him back and sets the cookie and sends him on his merry way. In some browsers such as Chrome, Bob may not even notice that he logged in using Vouch Proxy.
Overall
Maintained
Code review
Go module
Latest release
Releases this year
(top 24 of 51)
140 followers · starred May 2022
119 followers · starred Mar 2023
2,910 followers · starred Apr 2023
32 followers · starred Oct 2025