Harden-Runner is a CI/CD security agent that works like an EDR for GitHub Actions runners. It monitors network egress, file integrity, and process activity on those runners, detecting threats in real-time.
See the code

Corporate laptops and production servers typically have robust security monitoring in place to reduce risk and meet compliance requirements. However, CI/CD runners, which handle sensitive information like secrets for cloud environments and create production builds, often lack such security measures. This oversight has led to significant supply chain attacks, including the SolarWinds and Codecov breaches.
Traditional security monitoring and EDR solutions are ineffective for CI/CD runners due to their ephemeral nature. These tools also lack the necessary context to correlate events with specific workflow runs in a CI/CD environment.
StepSecurity Harden-Runner addresses this gap by providing security monitoring tailored for CI/CD runners, with support for Linux, Windows, and macOS runners. This approach brings CI/CD runners under the same level of security scrutiny as other critical systems, addressing a significant gap in the software supply chain.
Harden-Runner secures over 25 million CI/CD workflow runs every week, protecting thousands of pipelines, including those from popular open-source projects by Microsoft, Google, and CISA. See how top projects are using Harden-Runner and explore the insights: ➡️ Who's using Harden-Runner?
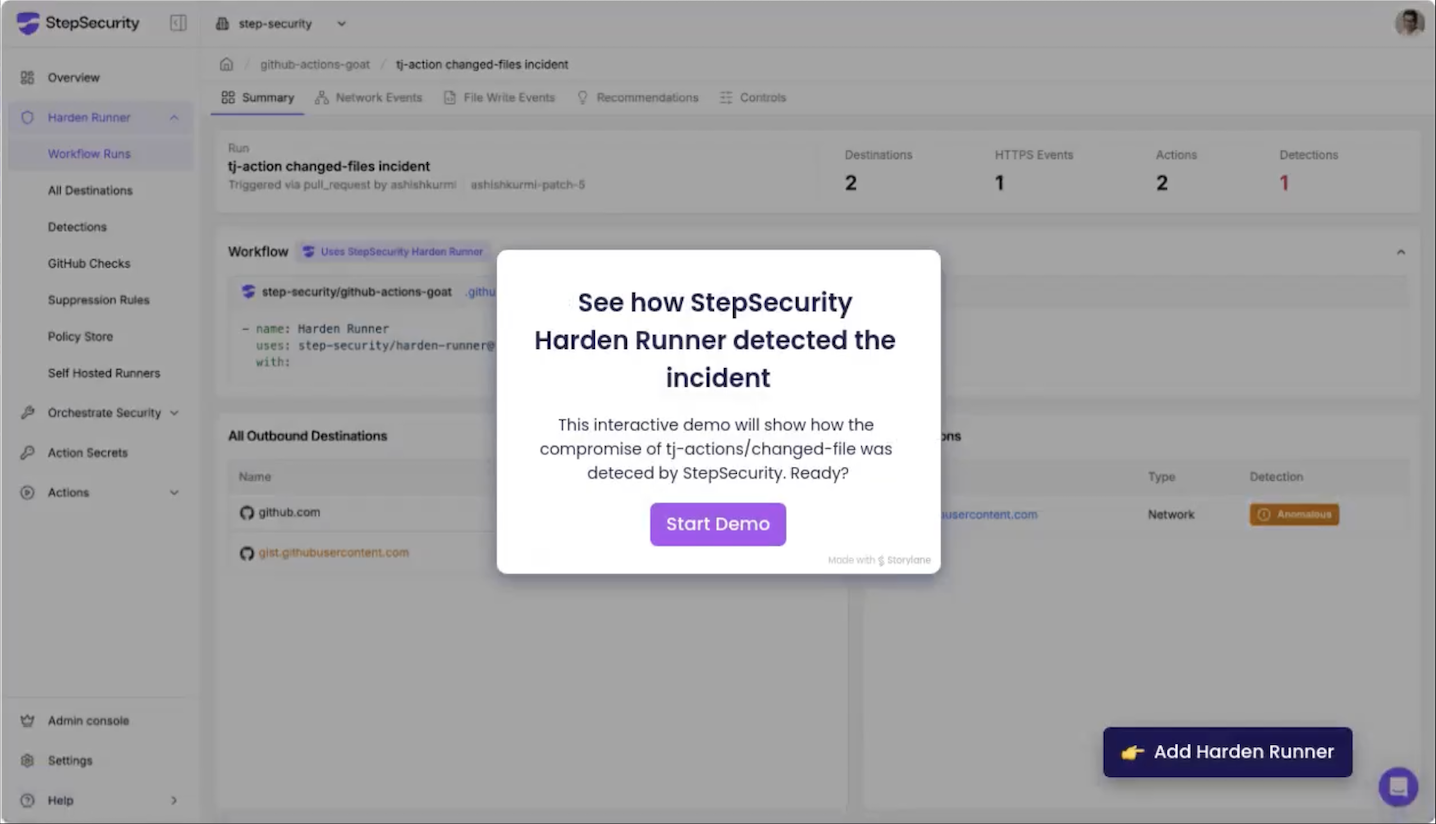
Learn how Harden-Runner works through the video below, which shows how it detected the tj-actions/changed-files compromise. View the interactive demo here.
This guide walks you through the steps to set up and use Harden-Runner in your CI/CD workflows. For more details, refer to the official documentation.
[!NOTE] The Community tier is free for public repositories on GitHub-hosted runners and includes the core feature set. Advanced features, private repositories, and self-hosted runners (including ARC) require the Enterprise tier. See Features and Pricing Tiers for what is in each tier.
To integrate Harden-Runner, follow these steps:
.github/workflows/<workflow-name>.yml).steps:
- name: Harden Runner
uses: step-security/harden-runner@05e31511f85b41b11d1cf0ef85d0992719546e2c # v2.21.0
with:
egress-policy: audit
Tip: Automate this step by pasting your workflow into the StepSecurity online tool
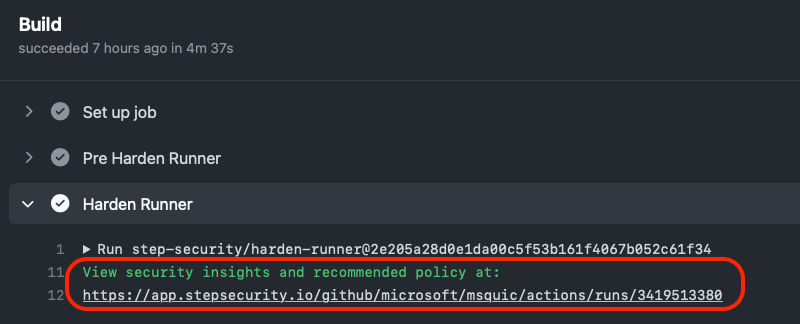
Run your workflow. Once completed:
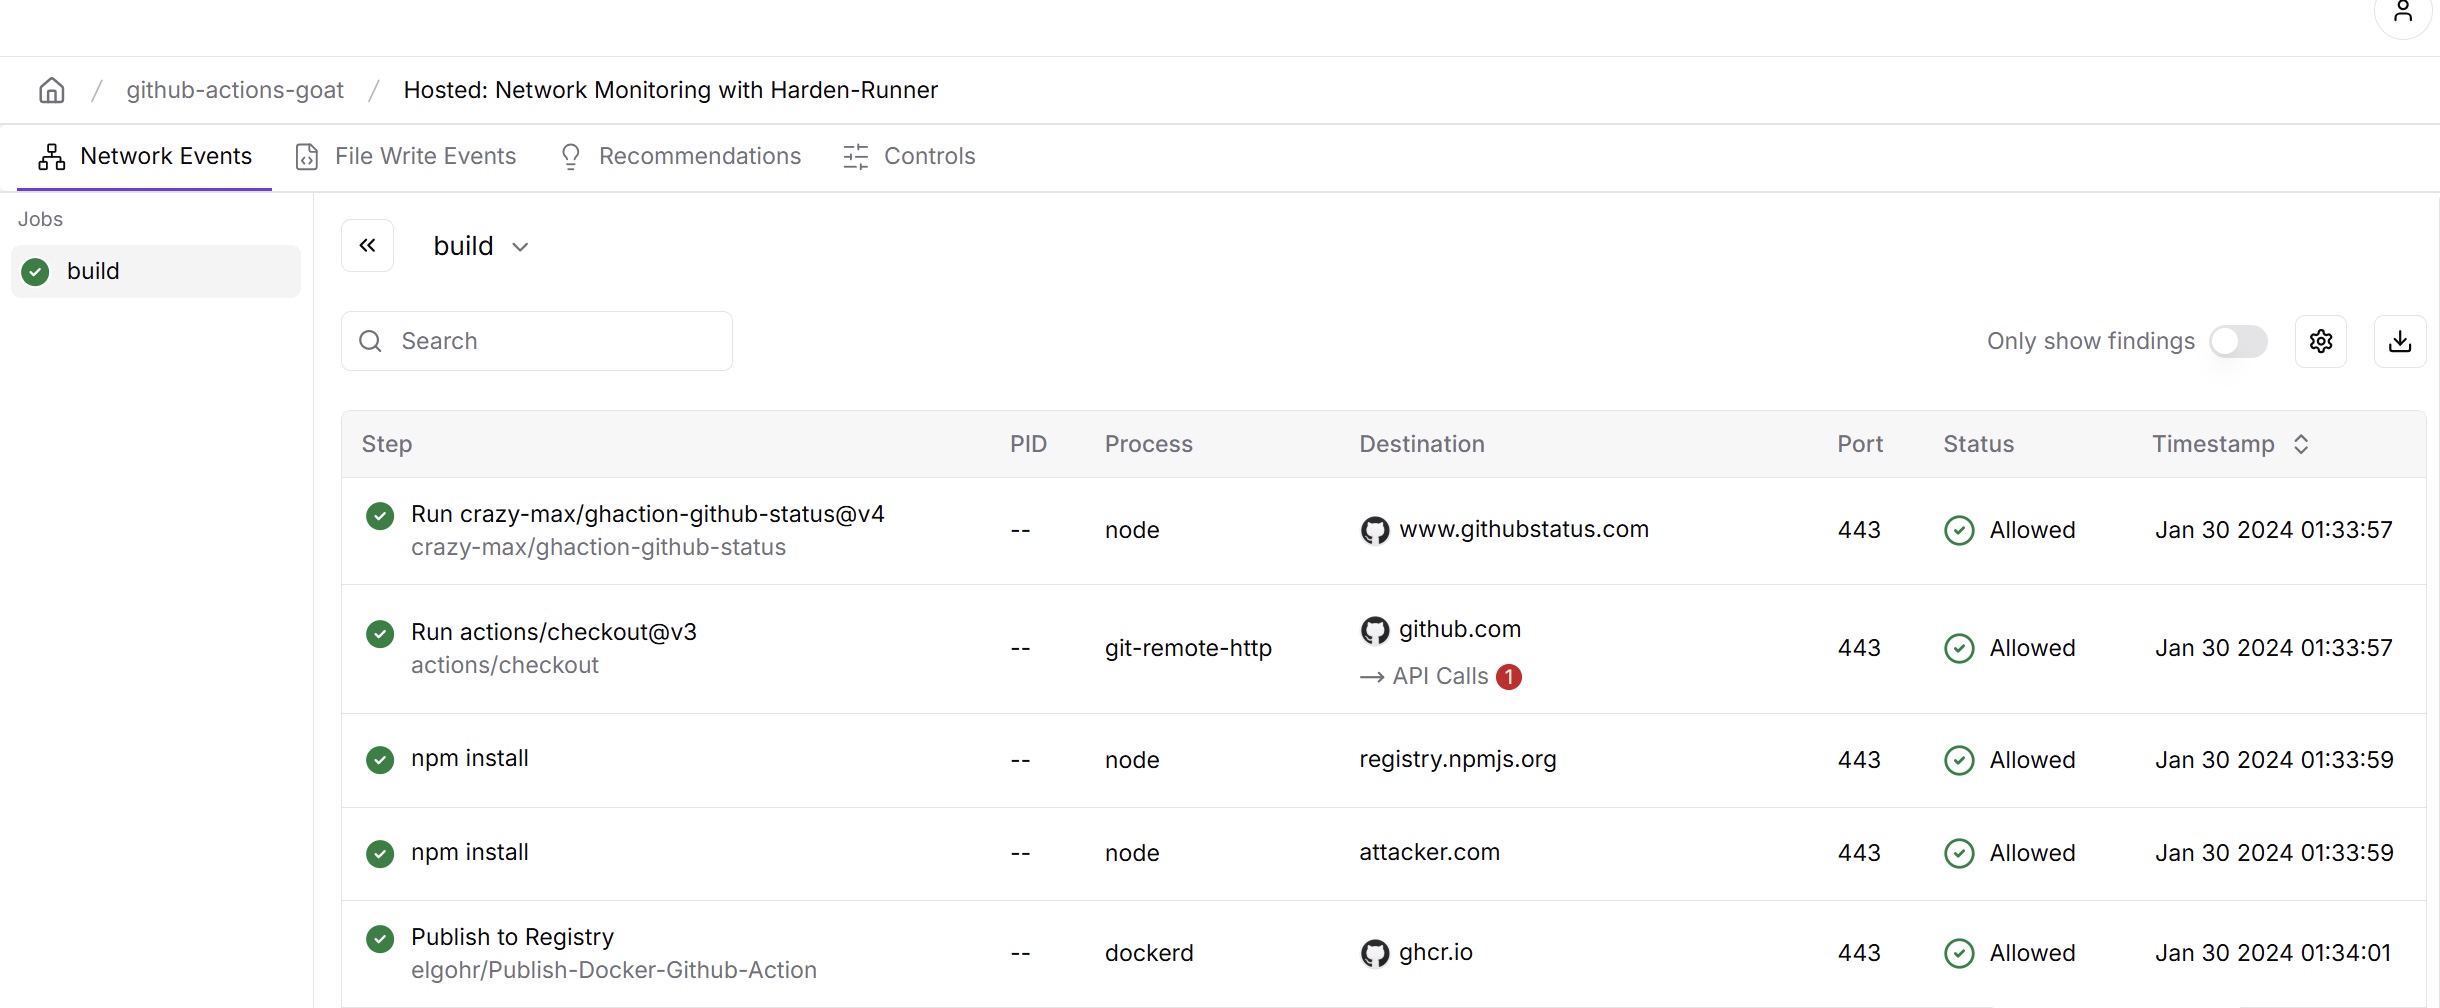
GITHUB_TOKEN permissions.Harden-Runner offers a comprehensive suite of features to enhance the security of your CI/CD workflows, available in two tiers: Community (free) and Enterprise (paid). Two things determine what you get: where your workflows run decides whether the free tier is available at all, and your tier decides which features you get. The feature lists below show what is in each tier.
| Where your workflows run | What's available |
|---|---|
| Public repositories on GitHub-hosted runners | Community features free; Enterprise features require a paid plan |
| Private repositories (any runner type) | Enterprise (paid) only |
| Self-hosted runners, including ARC and bare metal (public or private repositories) | Enterprise (paid) only |
[!IMPORTANT] Self-hosted runners require an Enterprise subscription, even for public repositories. Without a subscription, the Harden-Runner action is a no-op on self-hosted runners: the step succeeds and your workflow passes, but nothing is monitored and no insights are generated. To enable Harden-Runner on your self-hosted runners, start a free trial.
Available for public repositories running on GitHub-hosted runners:
egress-policy: audit mode.Includes all features in the Community tier, plus:
For a detailed comparison and more information, please visit our Pricing Page.
Explore the full feature set in the Features Documentation.
Many popular third-party GitHub Actions are abandoned or stuck on outdated runtimes. StepSecurity publishes Maintained Actions: drop-in replacements that are actively maintained, security-reviewed, and kept current, including updates to the Node 24 runtime.
Harden-Runner is trusted by over 11,000 leading open-source projects and enterprises, including Microsoft, Google, Kubernetes, and more.
 |  |  |  |  |  |  |  |
|---|---|---|---|---|---|---|---|
| CISA Explore | Microsoft Explore | Google Explore | DataDog Explore | Intel Explore | Kubernetes Explore | Node.js Explore | AWS Explore |
Harden-Runner is designed to work seamlessly across a variety of runner environments, providing consistent security insights and protections regardless of where your workflows execute. For self-hosted runners, audit mode is deployed directly to the runner infrastructure without requiring any changes to your existing workflows. For more details, refer to the official documentation.
| Environment Type | Compatibility | Audit Mode Deployment | Workflow Changes for Audit/Block Mode | Free Community Tier |
|---|---|---|---|---|
| GitHub-hosted runners (Linux) | ✅ Full support | Add Harden-Runner Action to workflow | Yes | ✅ Public repos (Community features only) |
| GitHub-hosted runners (Windows, macOS) | ✅ Audit mode only | Add Harden-Runner Action to workflow | Yes | ✅ Public repos (Community features only) |
| Self-hosted VM runners | ✅ Full support | Include agent in runner image | No | ❌ Enterprise subscription required |
| Self-hosted bare-metal runners | ✅ Full support | Install agent as a service | No | ❌ Enterprise subscription required |
| Actions Runner Controller (ARC) | ✅ Full support | Deploy as DaemonSet | No | ❌ Enterprise subscription required |
| RunsOn Runners | ✅ Full support | Pre-integrated | No | ❌ Enterprise subscription required |
[!NOTE] If you use GitHub Enterprise Server (GHES), set
customerandserver-namefor TLS checks and policy fetching.
For an ephemeral Linux VM without the agent already installed, add this as the first job step, using the customer and server names registered with StepSecurity:
- uses: step-security/harden-runner@v2
  with:
    deploy-on-self-hosted-vm: true
    customer: your-stepsecurity-customer
    server-name: your-ghes-server
    egress-policy: audit
This requires a StepSecurity subscription with TLS inspection and self-hosted VM support enabled. The action uploads the job's events and prints agent logs during its post step.
Want to know the technical details? Dive into the architecture of Harden-Runner and its integrations for GitHub-hosted and self-hosted runners in our How Harden-Runner Works Documentation.
While Harden-Runner offers powerful features, there are certain limitations. See the complete list in Known Limitations.
Join the conversation! For questions, ideas, or feedback, visit our Discussions Page.
For enterprise support, email [email protected]. Interested in using Harden-Runner in other CI/CD platforms? Reach out to [email protected].
Harden-Runner is open source. See the LICENSE file for details.
(top 24 of 77)
6,963 followers · starred Mar 2025
5,148 followers · starred Sep 2025
1,520 followers · starred Oct 2023
1,261 followers · starred Mar 2023
Harden-Runner is a CI/CD security agent that works like an EDR for GitHub Actions runners. It monitors network egress, file integrity, and process activity on those runners, detecting threats in real-time.
See the code
Corporate laptops and production servers typically have robust security monitoring in place to reduce risk and meet compliance requirements. However, CI/CD runners, which handle sensitive information like secrets for cloud environments and create production builds, often lack such security measures. This oversight has led to significant supply chain attacks, including the SolarWinds and Codecov breaches.
Traditional security monitoring and EDR solutions are ineffective for CI/CD runners due to their ephemeral nature. These tools also lack the necessary context to correlate events with specific workflow runs in a CI/CD environment.
StepSecurity Harden-Runner addresses this gap by providing security monitoring tailored for CI/CD runners, with support for Linux, Windows, and macOS runners. This approach brings CI/CD runners under the same level of security scrutiny as other critical systems, addressing a significant gap in the software supply chain.
Harden-Runner secures over 25 million CI/CD workflow runs every week, protecting thousands of pipelines, including those from popular open-source projects by Microsoft, Google, and CISA. See how top projects are using Harden-Runner and explore the insights: ➡️ Who's using Harden-Runner?
Learn how Harden-Runner works through the video below, which shows how it detected the tj-actions/changed-files compromise. View the interactive demo here.
This guide walks you through the steps to set up and use Harden-Runner in your CI/CD workflows. For more details, refer to the official documentation.
[!NOTE] The Community tier is free for public repositories on GitHub-hosted runners and includes the core feature set. Advanced features, private repositories, and self-hosted runners (including ARC) require the Enterprise tier. See Features and Pricing Tiers for what is in each tier.
To integrate Harden-Runner, follow these steps:
.github/workflows/<workflow-name>.yml).steps:
- name: Harden Runner
uses: step-security/harden-runner@05e31511f85b41b11d1cf0ef85d0992719546e2c # v2.21.0
with:
egress-policy: audit
Tip: Automate this step by pasting your workflow into the StepSecurity online tool
Run your workflow. Once completed:
GITHUB_TOKEN permissions.Harden-Runner offers a comprehensive suite of features to enhance the security of your CI/CD workflows, available in two tiers: Community (free) and Enterprise (paid). Two things determine what you get: where your workflows run decides whether the free tier is available at all, and your tier decides which features you get. The feature lists below show what is in each tier.
| Where your workflows run | What's available |
|---|---|
| Public repositories on GitHub-hosted runners | Community features free; Enterprise features require a paid plan |
| Private repositories (any runner type) | Enterprise (paid) only |
| Self-hosted runners, including ARC and bare metal (public or private repositories) | Enterprise (paid) only |
[!IMPORTANT] Self-hosted runners require an Enterprise subscription, even for public repositories. Without a subscription, the Harden-Runner action is a no-op on self-hosted runners: the step succeeds and your workflow passes, but nothing is monitored and no insights are generated. To enable Harden-Runner on your self-hosted runners, start a free trial.
Available for public repositories running on GitHub-hosted runners:
egress-policy: audit mode.Includes all features in the Community tier, plus:
For a detailed comparison and more information, please visit our Pricing Page.
Explore the full feature set in the Features Documentation.
Many popular third-party GitHub Actions are abandoned or stuck on outdated runtimes. StepSecurity publishes Maintained Actions: drop-in replacements that are actively maintained, security-reviewed, and kept current, including updates to the Node 24 runtime.
Harden-Runner is trusted by over 11,000 leading open-source projects and enterprises, including Microsoft, Google, Kubernetes, and more.
| | | | | | | |
|---|---|---|---|---|---|---|---|
| CISA Explore | Microsoft Explore | Google Explore | DataDog Explore | Intel Explore | Kubernetes Explore | Node.js Explore | AWS Explore |
Harden-Runner is designed to work seamlessly across a variety of runner environments, providing consistent security insights and protections regardless of where your workflows execute. For self-hosted runners, audit mode is deployed directly to the runner infrastructure without requiring any changes to your existing workflows. For more details, refer to the official documentation.
| Environment Type | Compatibility | Audit Mode Deployment | Workflow Changes for Audit/Block Mode | Free Community Tier |
|---|---|---|---|---|
| GitHub-hosted runners (Linux) | ✅ Full support | Add Harden-Runner Action to workflow | Yes | ✅ Public repos (Community features only) |
| GitHub-hosted runners (Windows, macOS) | ✅ Audit mode only | Add Harden-Runner Action to workflow | Yes | ✅ Public repos (Community features only) |
| Self-hosted VM runners | ✅ Full support | Include agent in runner image | No | ❌ Enterprise subscription required |
| Self-hosted bare-metal runners | ✅ Full support | Install agent as a service | No | ❌ Enterprise subscription required |
| Actions Runner Controller (ARC) | ✅ Full support | Deploy as DaemonSet | No | ❌ Enterprise subscription required |
| RunsOn Runners | ✅ Full support | Pre-integrated | No | ❌ Enterprise subscription required |
[!NOTE] If you use GitHub Enterprise Server (GHES), set
customerandserver-namefor TLS checks and policy fetching.
For an ephemeral Linux VM without the agent already installed, add this as the first job step, using the customer and server names registered with StepSecurity:
- uses: step-security/harden-runner@v2
  with:
    deploy-on-self-hosted-vm: true
    customer: your-stepsecurity-customer
    server-name: your-ghes-server
    egress-policy: audit
This requires a StepSecurity subscription with TLS inspection and self-hosted VM support enabled. The action uploads the job's events and prints agent logs during its post step.
Want to know the technical details? Dive into the architecture of Harden-Runner and its integrations for GitHub-hosted and self-hosted runners in our How Harden-Runner Works Documentation.
While Harden-Runner offers powerful features, there are certain limitations. See the complete list in Known Limitations.
Join the conversation! For questions, ideas, or feedback, visit our Discussions Page.
For enterprise support, email [email protected]. Interested in using Harden-Runner in other CI/CD platforms? Reach out to [email protected].
Harden-Runner is open source. See the LICENSE file for details.
(top 24 of 77)
6,963 followers · starred Mar 2025
5,148 followers · starred Sep 2025
1,520 followers · starred Oct 2023
1,261 followers · starred Mar 2023



