
:busts_in_silhouette: A bash-tool to store your private data inside a git repository.
See the codeREADME
git-secret


What is git-secret?
git-secret is a bash tool which stores private data inside a git repo.
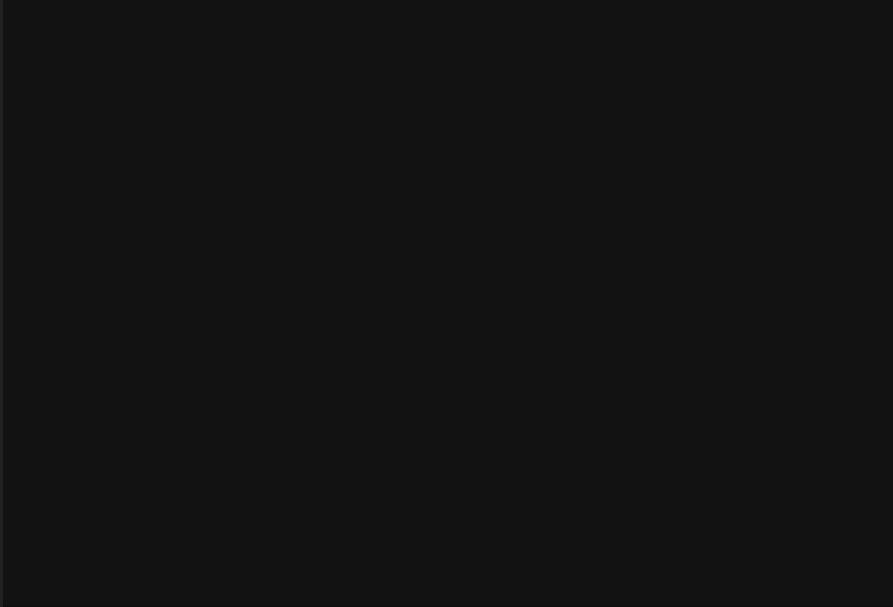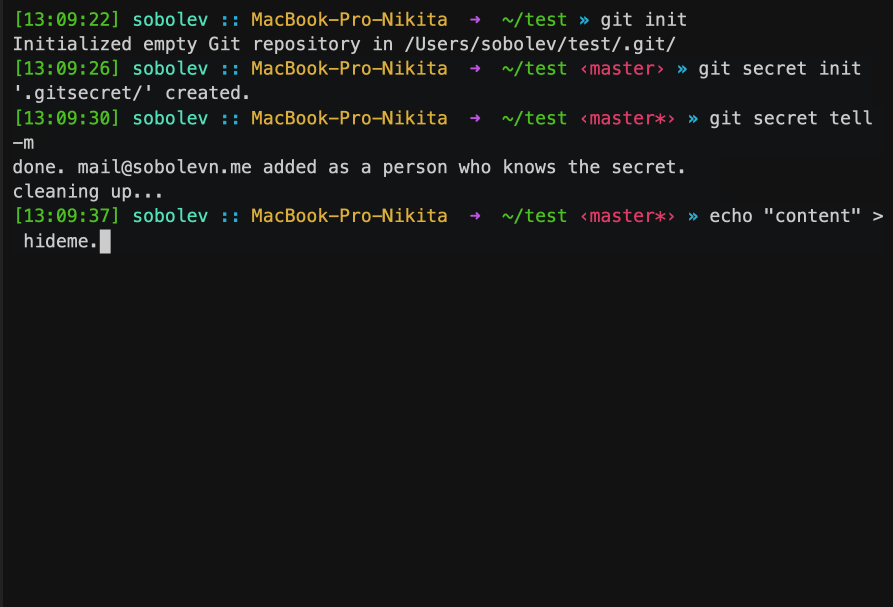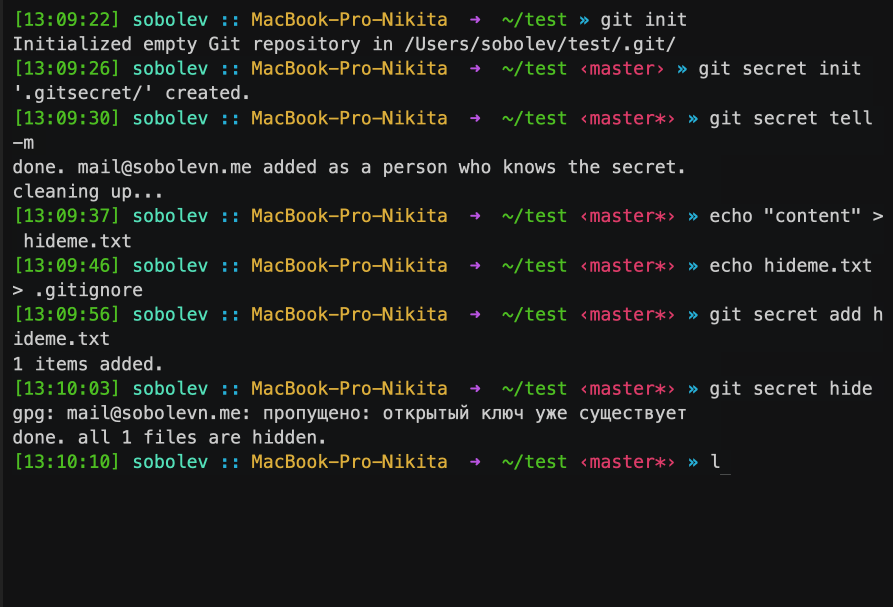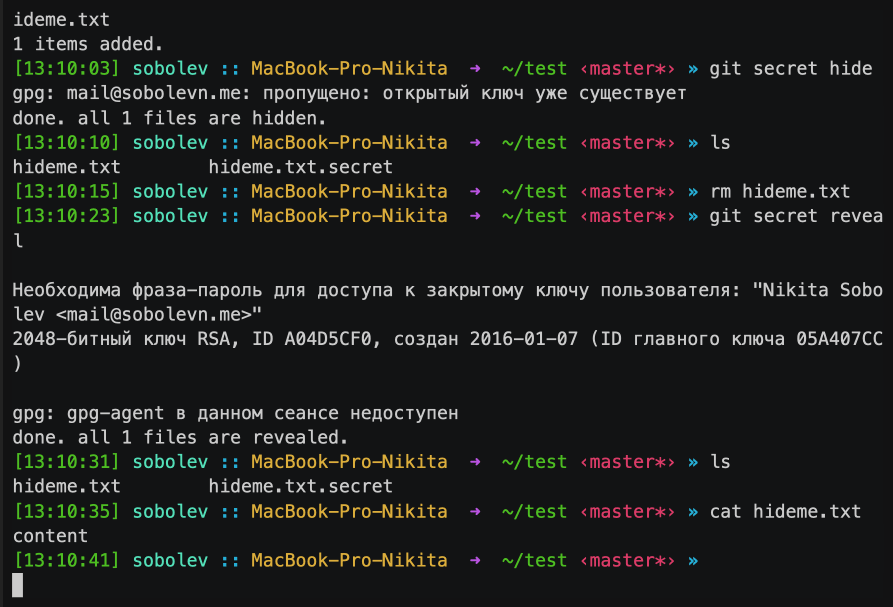
git-secret encrypts files with permitted users' public keys,
allowing users you trust to access encrypted data using pgp and their secret keys.
With git-secret, changes to access rights are simplified, and private-public key issues are handled for you.
When someone's permission is revoked, secrets do not need to be changed with git-secret -
just remove their key from the repo's keyring using git secret removeperson their@email.com,
re-encrypt the files, and they won't be able to decrypt secrets anymore.
If you think the user might have copied the secrets or keys when they had access, then
you should also change the secrets.
Preview
Installation
git-secret supports brew, just type: brew install git-secret
It also supports apt and yum. You can also use make if you want to.
See the installation section for the details.
Requirements
git-secret relies on several external packages:
bashsince3.2.57(it is hard to tell the correctpatchrelease)gawksince4.0.2gitsince1.8.3.1gpgsincegnupg 1.4tognupg 2.Xsha256sumsince8.21(on freebsd and MacOSshasumis used instead)
Contributing
Do you want to help the project? Find an issue and send a PR. It is more than welcomed! See CONTRIBUTING.md on how to do that.
Security
In order to encrypt (git-secret hide -m) files only when modified, the path
mappings file tracks sha256sum checksums of the files added (git-secret add) to
git-secret's path mappings filesystem database. Although, the chances of
encountering a sha collision are low, it is recommend that you pad files with
random data for greater security. Or avoid using the -m option altogether.
If your secret file holds more data than just a single password these
precautions should not be necessary, but could be followed for greater
security.
If you found any security related issues, please do not disclose it in public. Send an email to mail@sobolevn.me
Changelog
git-secret uses semver. See CHANGELOG.md.
Packagers
Thanks to all the people and groups who package git-secret for easier install on particular OSes and distributions!

Here are some packagings of git-secret that we're aware of:
- https://formulae.brew.sh/formula/git-secret
- https://packages.ubuntu.com/bionic/git-secret
- https://src.fedoraproject.org/rpms/git-secret
- https://aur.archlinux.org/packages/git-secret/
- https://pkgs.alpinelinux.org/package/edge/testing/x86/git-secret
- https://packages.debian.org/sid/git-secret
- https://github.com/void-linux/void-packages/blob/master/srcpkgs/git-secret/template
Such packages are considered 'downstream' because the git-secret code 'flows' from the git-secret repository
to the various rpm/deb/dpkg/etc packages that are created for specific OSes and distributions.
We have also added notes specifically for packagers in CONTRIBUTING.md.
Sponsors
Support this project by becoming a sponsor. Your logo will show up here with a link to your website. [Become a sponsor]

Backers
Thanks to all our backers!

Contributors
This project exists thanks to all the people who contribute. [Contribute].

License
MIT. See LICENSE.md for details.
Thanks
Special thanks to Elio Qoshi from ura for the awesome logo.
Significant stargazers
(top 24 of 35)

868 followers · starred Aug 2022
322 followers · starred May 2017
534 followers · starred Dec 2019

115 followers · starred Jun 2020
Similar repos


Languages
Shell
92.4%
Dockerfile
4.5%
Makefile
3.2%
:busts_in_silhouette: A bash-tool to store your private data inside a git repository.
See the codeREADME
git-secret
What is git-secret?
git-secret is a bash tool which stores private data inside a git repo.
git-secret encrypts files with permitted users' public keys,
allowing users you trust to access encrypted data using pgp and their secret keys.
With git-secret, changes to access rights are simplified, and private-public key issues are handled for you.
When someone's permission is revoked, secrets do not need to be changed with git-secret -
just remove their key from the repo's keyring using git secret removeperson their@email.com,
re-encrypt the files, and they won't be able to decrypt secrets anymore.
If you think the user might have copied the secrets or keys when they had access, then
you should also change the secrets.
Preview
Installation
git-secret supports brew, just type: brew install git-secret
It also supports apt and yum. You can also use make if you want to.
See the installation section for the details.
Requirements
git-secret relies on several external packages:
bashsince3.2.57(it is hard to tell the correctpatchrelease)gawksince4.0.2gitsince1.8.3.1gpgsincegnupg 1.4tognupg 2.Xsha256sumsince8.21(on freebsd and MacOSshasumis used instead)
Contributing
Do you want to help the project? Find an issue and send a PR. It is more than welcomed! See CONTRIBUTING.md on how to do that.
Security
In order to encrypt (git-secret hide -m) files only when modified, the path
mappings file tracks sha256sum checksums of the files added (git-secret add) to
git-secret's path mappings filesystem database. Although, the chances of
encountering a sha collision are low, it is recommend that you pad files with
random data for greater security. Or avoid using the -m option altogether.
If your secret file holds more data than just a single password these
precautions should not be necessary, but could be followed for greater
security.
If you found any security related issues, please do not disclose it in public. Send an email to mail@sobolevn.me
Changelog
git-secret uses semver. See CHANGELOG.md.
Packagers
Thanks to all the people and groups who package git-secret for easier install on particular OSes and distributions!
Here are some packagings of git-secret that we're aware of:
- https://formulae.brew.sh/formula/git-secret
- https://packages.ubuntu.com/bionic/git-secret
- https://src.fedoraproject.org/rpms/git-secret
- https://aur.archlinux.org/packages/git-secret/
- https://pkgs.alpinelinux.org/package/edge/testing/x86/git-secret
- https://packages.debian.org/sid/git-secret
- https://github.com/void-linux/void-packages/blob/master/srcpkgs/git-secret/template
Such packages are considered 'downstream' because the git-secret code 'flows' from the git-secret repository
to the various rpm/deb/dpkg/etc packages that are created for specific OSes and distributions.
We have also added notes specifically for packagers in CONTRIBUTING.md.
Sponsors
Support this project by becoming a sponsor. Your logo will show up here with a link to your website. [Become a sponsor]
Backers
Thanks to all our backers!
Contributors
This project exists thanks to all the people who contribute. [Contribute].
License
MIT. See LICENSE.md for details.
Thanks
Special thanks to Elio Qoshi from ura for the awesome logo.
Similar repos
Significant stargazers
(top 24 of 35)
868 followers · starred Aug 2022
322 followers · starred May 2017
534 followers · starred Dec 2019
115 followers · starred Jun 2020
Languages
Shell
92.4%
Dockerfile
4.5%
Makefile
3.2%