Security sensor for realtime threat detection and protection
See the code
Security sensor for realtime threat detection and protection
Get Started »
Docs
•
Rules
•
Filaments
•
Download
•
Discussions
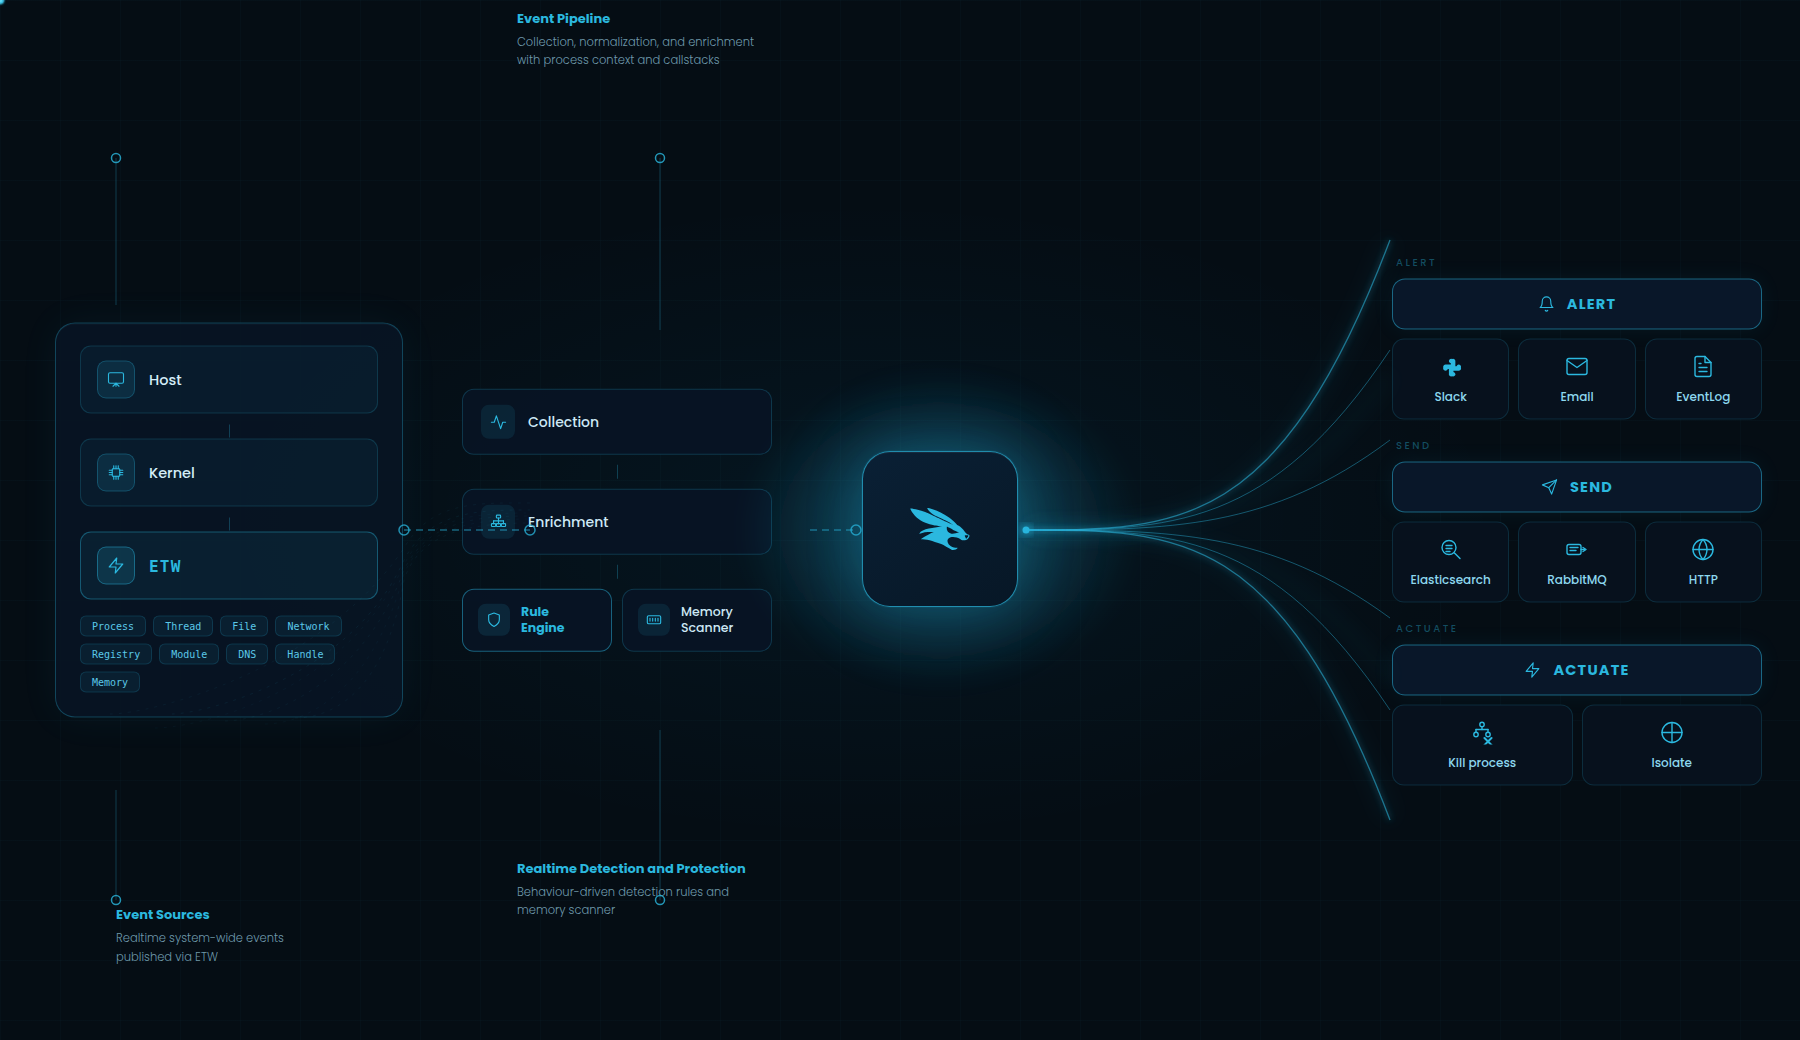
Fibratus detects and eradicates advanced attacker tradecraft, malware, and emerging threats by scrutinizing and asserting a wide spectrum of system events against a behavior-driven rule engine and YARA memory scanner.
Events can be routed to a wide range of output sinks or written to capture files for local inspection and forensic analysis. With filaments, you can extend Fibratus with your own tooling and tap into the full power of the Python ecosystem.
In a nutshell, the Fibratus mantra is built on three pillars: realtime behavior detection, memory scanning, and forensics.
The fastest way to install Fibratus is to run the following command from an elevated PowerShell terminal:
irm https://install.fibratus.io | iex
That's it. The installer downloads and sets up the latest version of Fibratus.
Once installed, follow the Quick Start to see Fibratus detect your first security event in real time.
Prefer a manual installation? See the Installation Guide for alternative installation methods and detailed instructions.
Go beyond the quick start and learn how Fibratus works under the hood. Explore the fundamentals, understand how Fibratus observes system activity, and learn how to build rules that detect and respond to threats.
We love contributions. To start contributing to Fibratus, please read our contribution guidelines.
Free code signing provided by SignPath.io, certificate by SignPath Foundation. All releases are automatically signed.
Developed with ❤️ by Nedim Šabić Šabić and contributors
Overall
Maintained
Code review
Go module
Latest release
Releases this year
415 followers · starred Jul 2016
606 followers · starred Apr 2021
341 followers · starred Apr 2024
368 followers · starred Dec 2020
Security sensor for realtime threat detection and protection
See the code
Security sensor for realtime threat detection and protection
Get Started »
Docs
•
Rules
•
Filaments
•
Download
•
Discussions
Fibratus detects and eradicates advanced attacker tradecraft, malware, and emerging threats by scrutinizing and asserting a wide spectrum of system events against a behavior-driven rule engine and YARA memory scanner.
Events can be routed to a wide range of output sinks or written to capture files for local inspection and forensic analysis. With filaments, you can extend Fibratus with your own tooling and tap into the full power of the Python ecosystem.
In a nutshell, the Fibratus mantra is built on three pillars: realtime behavior detection, memory scanning, and forensics.
The fastest way to install Fibratus is to run the following command from an elevated PowerShell terminal:
irm https://install.fibratus.io | iex
That's it. The installer downloads and sets up the latest version of Fibratus.
Once installed, follow the Quick Start to see Fibratus detect your first security event in real time.
Prefer a manual installation? See the Installation Guide for alternative installation methods and detailed instructions.
Go beyond the quick start and learn how Fibratus works under the hood. Explore the fundamentals, understand how Fibratus observes system activity, and learn how to build rules that detect and respond to threats.
We love contributions. To start contributing to Fibratus, please read our contribution guidelines.
Free code signing provided by SignPath.io, certificate by SignPath Foundation. All releases are automatically signed.
Developed with ❤️ by Nedim Šabić Šabić and contributors
Overall
Maintained
Code review
Go module
Latest release
Releases this year
415 followers · starred Jul 2016
606 followers · starred Apr 2021
341 followers · starred Apr 2024
368 followers · starred Dec 2020