
Open-source, enterprise-grade threat modeling platform
See the codeSee what people are saying
README
Precogly



[!IMPORTANT] Precogly is now an OWASP project! OWASP is the world's largest open-source application security community, and Precogly is proud to be part of it.
The open-source alternative to commercial threat modeling platforms
Quick Start
  git clone --branch v0.4.0 https://github.com/precogly/precogly.git
  cd precogly
  docker compose up --build
Open http://localhost:5173 and log in with admin@precogly.dev / admin123. Two further demo accounts are seeded so roles and multi-tenancy can be exercised locally; the seed prints all three when it finishes.
Documentation
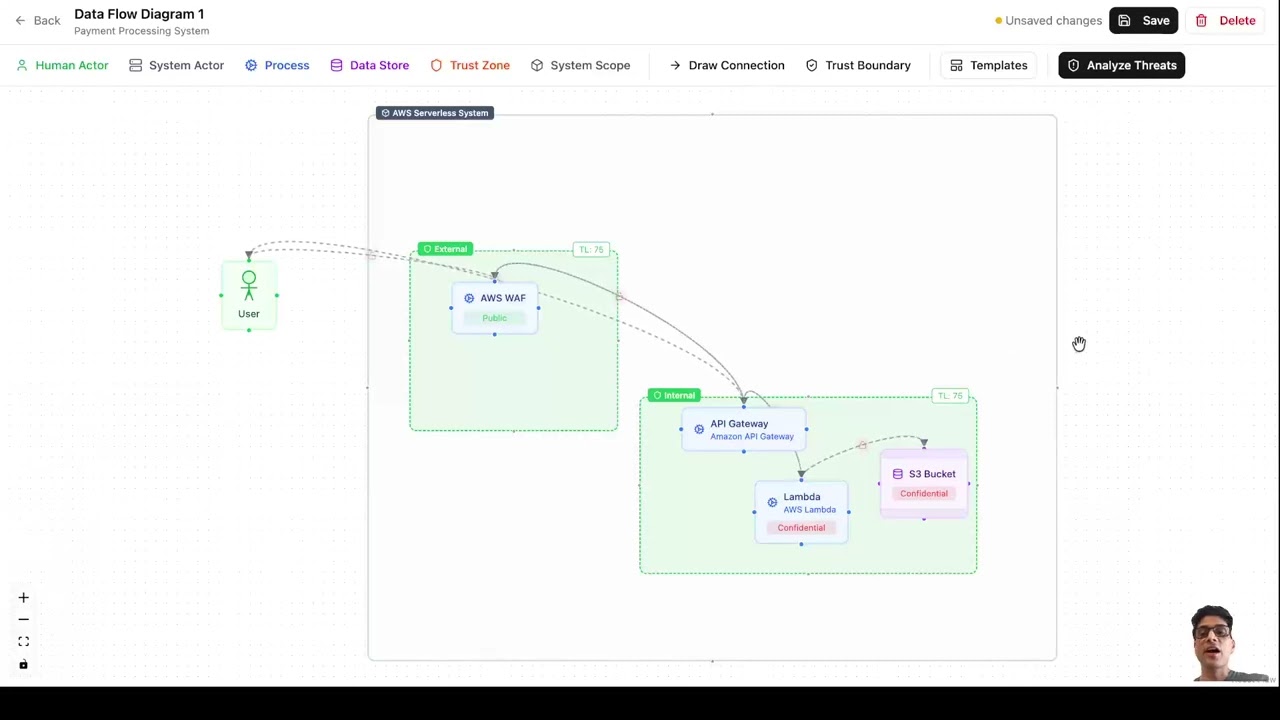
Video Walkthrough
Why Precogly?
Open-source threat modeling tools lack enterprise features. Commercial tools come with heavy price tags and vendor lock-in.
Precogly bridges this gap and democratizes threat modeling for every org in the world.
Key Features
- Import and export TM-BOM style JSON files - improves interoperability with other threat modeling platforms
- A threat modeling workspace allows for team collaboration
- An advanced DFD editor (allows for nested components, trust zones with trust boundaries and much more)
- Community library packs with links to taxonomies like MITRE ATT&CK, CAPEC, LINDDUN, STRIDE etc. - allows your team to quickly create high quality threat models
Who is Precogly for?
- Security architects looking to scale threat modeling in their orgs.
- Vibe coding security engineers who need a well-architected CRUD foundation on which they can build their AI threat modeling assistants.
- Threat modeling consultants and trainers looking for a platform that supports reference images, team collaboration, and structured threat modeling programs.
- Compliance professionals looking to link threat modeling with security requirements coming from standards like ASVS or laws like CRA and DORA
Precogly is designed for enterprise workflows, but smaller organizations can also find value in the DFD editor, library packs, and collaborative workspace.
How is Precogly different?
- Compliance-aware — Built-in traceability to DORA, CRA, ASVS, NIST CSF, SOC 2, and more. Threats can link to security taxonomies, while countermeasures map to framework requirements.
- Structured library packs — Not just brainstorming. Curated packs with components, threats, countermeasures, and taxonomy links (MITRE ATT&CK, CAPEC, CWE, STRIDE) give your team a structured starting point.
- AI-agent ready architecture — A clean REST API with full OpenAPI docs, designed to be a foundation for AI-powered threat modeling assistants.
- Pack ecosystem — Community and official packs for AWS, Azure, GCP, banking, and compliance frameworks. Extend or create your own.
Our AI Philosophy
- AI agents need CRUD scaffolding — Before AI generates a single threat, the platform must let you create, store, update, and track its core objects.
- Ahead-of-time AI > just-in-time AI — You can point AI at a system during threat modeling, or use it ahead of time to build curated threat libraries linked to standards. The second wins. Fewer hallucinations, more consistency.
- The journey of understanding is the threat model — The value of the threat model lives in the shared comprehension that humans build along the way. That needs a common interface where humans and agents work from the same picture.
Tech Stack
- Frontend: React 19, TypeScript, Tailwind CSS, shadcn/ui, React Flow
- Backend: Django 5.2, Django REST Framework, PostgreSQL 16
- Infrastructure: Docker, nginx (production)
Roadmap
- 0.3: DFD Editor Features (released July 2026)
- 0.4: MCP and AI Agents Support (released September 2026)
- 0.5: Threat Modeling Program Management and TM-BOM Alignment
- See threat modeling coverage and risk management progress across the organization
- Report on risk ownership, treatment status and overdue actions by business unit, team and product
- Align program management with the Threat Modeling Capabilities, especially the Measurement and Program Management areas
- Align Precogly's system representation with the TM-BOM System concepts in the upcoming CycloneDX 2.0
- 0.6: Risk Management
- Record risks from threat modeling, vulnerabilities and assessments in one risk register
- Assign risk owners, record treatment decisions and track residual risk
- Run risk assessments and produce reports that support compliance, including the EU CRA
- 0.7: Security Controls Management
- Show auditors that security controls are in place and working
- Define verification steps and record evidence
- Maintain control libraries at product and organization levels
- Integrate with development and security tools, starting with GitHub and DefectDojo
- Apply ISO/IEC 27034 concepts across applications, infrastructure and devices
See the GitHub milestones for current and upcoming release work.
Security
To report a vulnerability, please see our Security Policy.
Contributing
- Open an issue
- Contribute a library pack
- Contribute to the codebase
If you find Precogly useful, give the project a star!
Community
Join the conversation:
- Discord
- #project-precogly on OWASP Slack (get an invite)
Need Help? Contact the Developer
Special Thanks
A special thanks to Jeroen Verwoest for generously sharing his knowledge about threat modeling at an enterprise-scale in a compliance-heavy environment.
License
Apache 2.0
Significant stargazers

469 followers · starred May 2026

56 followers · starred Aug 2026

36 followers · starred Apr 2026
Similar repos


Open-source, enterprise-grade threat modeling platform
See the codeSee what people are saying
README
Precogly
[!IMPORTANT] Precogly is now an OWASP project! OWASP is the world's largest open-source application security community, and Precogly is proud to be part of it.
The open-source alternative to commercial threat modeling platforms
Quick Start
  git clone --branch v0.4.0 https://github.com/precogly/precogly.git
  cd precogly
  docker compose up --build
Open http://localhost:5173 and log in with admin@precogly.dev / admin123. Two further demo accounts are seeded so roles and multi-tenancy can be exercised locally; the seed prints all three when it finishes.
Documentation
Video Walkthrough
Why Precogly?
Open-source threat modeling tools lack enterprise features. Commercial tools come with heavy price tags and vendor lock-in.
Precogly bridges this gap and democratizes threat modeling for every org in the world.
Key Features
- Import and export TM-BOM style JSON files - improves interoperability with other threat modeling platforms
- A threat modeling workspace allows for team collaboration
- An advanced DFD editor (allows for nested components, trust zones with trust boundaries and much more)
- Community library packs with links to taxonomies like MITRE ATT&CK, CAPEC, LINDDUN, STRIDE etc. - allows your team to quickly create high quality threat models
Who is Precogly for?
- Security architects looking to scale threat modeling in their orgs.
- Vibe coding security engineers who need a well-architected CRUD foundation on which they can build their AI threat modeling assistants.
- Threat modeling consultants and trainers looking for a platform that supports reference images, team collaboration, and structured threat modeling programs.
- Compliance professionals looking to link threat modeling with security requirements coming from standards like ASVS or laws like CRA and DORA
Precogly is designed for enterprise workflows, but smaller organizations can also find value in the DFD editor, library packs, and collaborative workspace.
How is Precogly different?
- Compliance-aware — Built-in traceability to DORA, CRA, ASVS, NIST CSF, SOC 2, and more. Threats can link to security taxonomies, while countermeasures map to framework requirements.
- Structured library packs — Not just brainstorming. Curated packs with components, threats, countermeasures, and taxonomy links (MITRE ATT&CK, CAPEC, CWE, STRIDE) give your team a structured starting point.
- AI-agent ready architecture — A clean REST API with full OpenAPI docs, designed to be a foundation for AI-powered threat modeling assistants.
- Pack ecosystem — Community and official packs for AWS, Azure, GCP, banking, and compliance frameworks. Extend or create your own.
Our AI Philosophy
- AI agents need CRUD scaffolding — Before AI generates a single threat, the platform must let you create, store, update, and track its core objects.
- Ahead-of-time AI > just-in-time AI — You can point AI at a system during threat modeling, or use it ahead of time to build curated threat libraries linked to standards. The second wins. Fewer hallucinations, more consistency.
- The journey of understanding is the threat model — The value of the threat model lives in the shared comprehension that humans build along the way. That needs a common interface where humans and agents work from the same picture.
Tech Stack
- Frontend: React 19, TypeScript, Tailwind CSS, shadcn/ui, React Flow
- Backend: Django 5.2, Django REST Framework, PostgreSQL 16
- Infrastructure: Docker, nginx (production)
Roadmap
- 0.3: DFD Editor Features (released July 2026)
- 0.4: MCP and AI Agents Support (released September 2026)
- 0.5: Threat Modeling Program Management and TM-BOM Alignment
- See threat modeling coverage and risk management progress across the organization
- Report on risk ownership, treatment status and overdue actions by business unit, team and product
- Align program management with the Threat Modeling Capabilities, especially the Measurement and Program Management areas
- Align Precogly's system representation with the TM-BOM System concepts in the upcoming CycloneDX 2.0
- 0.6: Risk Management
- Record risks from threat modeling, vulnerabilities and assessments in one risk register
- Assign risk owners, record treatment decisions and track residual risk
- Run risk assessments and produce reports that support compliance, including the EU CRA
- 0.7: Security Controls Management
- Show auditors that security controls are in place and working
- Define verification steps and record evidence
- Maintain control libraries at product and organization levels
- Integrate with development and security tools, starting with GitHub and DefectDojo
- Apply ISO/IEC 27034 concepts across applications, infrastructure and devices
See the GitHub milestones for current and upcoming release work.
Security
To report a vulnerability, please see our Security Policy.
Contributing
- Open an issue
- Contribute a library pack
- Contribute to the codebase
If you find Precogly useful, give the project a star!
Community
Join the conversation:
- Discord
- #project-precogly on OWASP Slack (get an invite)
Need Help? Contact the Developer
Special Thanks
A special thanks to Jeroen Verwoest for generously sharing his knowledge about threat modeling at an enterprise-scale in a compliance-heavy environment.
License
Apache 2.0
Similar repos
Significant stargazers
469 followers · starred May 2026
56 followers · starred Aug 2026
36 followers · starred Apr 2026