outflanknl/RedELK

Red Team's SIEM - tool for Red Teams used for tracking and alarming about Blue Team activities as well as better usability in long term operations.

Python

2,683

1,086 commits

updated Oct 10, 2026

See the code

README

Build docker base image (dev) Build docker elasticsearch image (dev) Build docker jupyter image (dev) Build docker kibana image (dev) Build docker logstash image (dev)

RedELK

The Red Team's SIEM - a tool for Red Teams for tracking and alarming about Blue Team activities as well as enhanced usability in long term operations.

  1. Enhanced usability and overview for the red team operators by creating a central location where all relevant operational logs from multiple teamservers are collected and enriched. This is great for historic searching within the operation as well as giving a read-only view on the operation (e.g. for the White Team). Especially useful for multi-scenario, multi-teamserver, multi-member and multi-month operations. Also, super easy ways for viewing all screenshots, IOCs, keystrokes output, etc. \o/
  2. Spot the Blue Team by having a central location where all traffic logs from redirectors are collected and enriched. Using specific queries its now possible to detect that the Blue Team is investigating your infrastructure.

Background info

Check the wiki for info on usage or one the blog posts or presentations listed below:

Installation

Check the wiki for manual installation manual. There are also Ansible playbooks maintained by others:

Conceptual overview

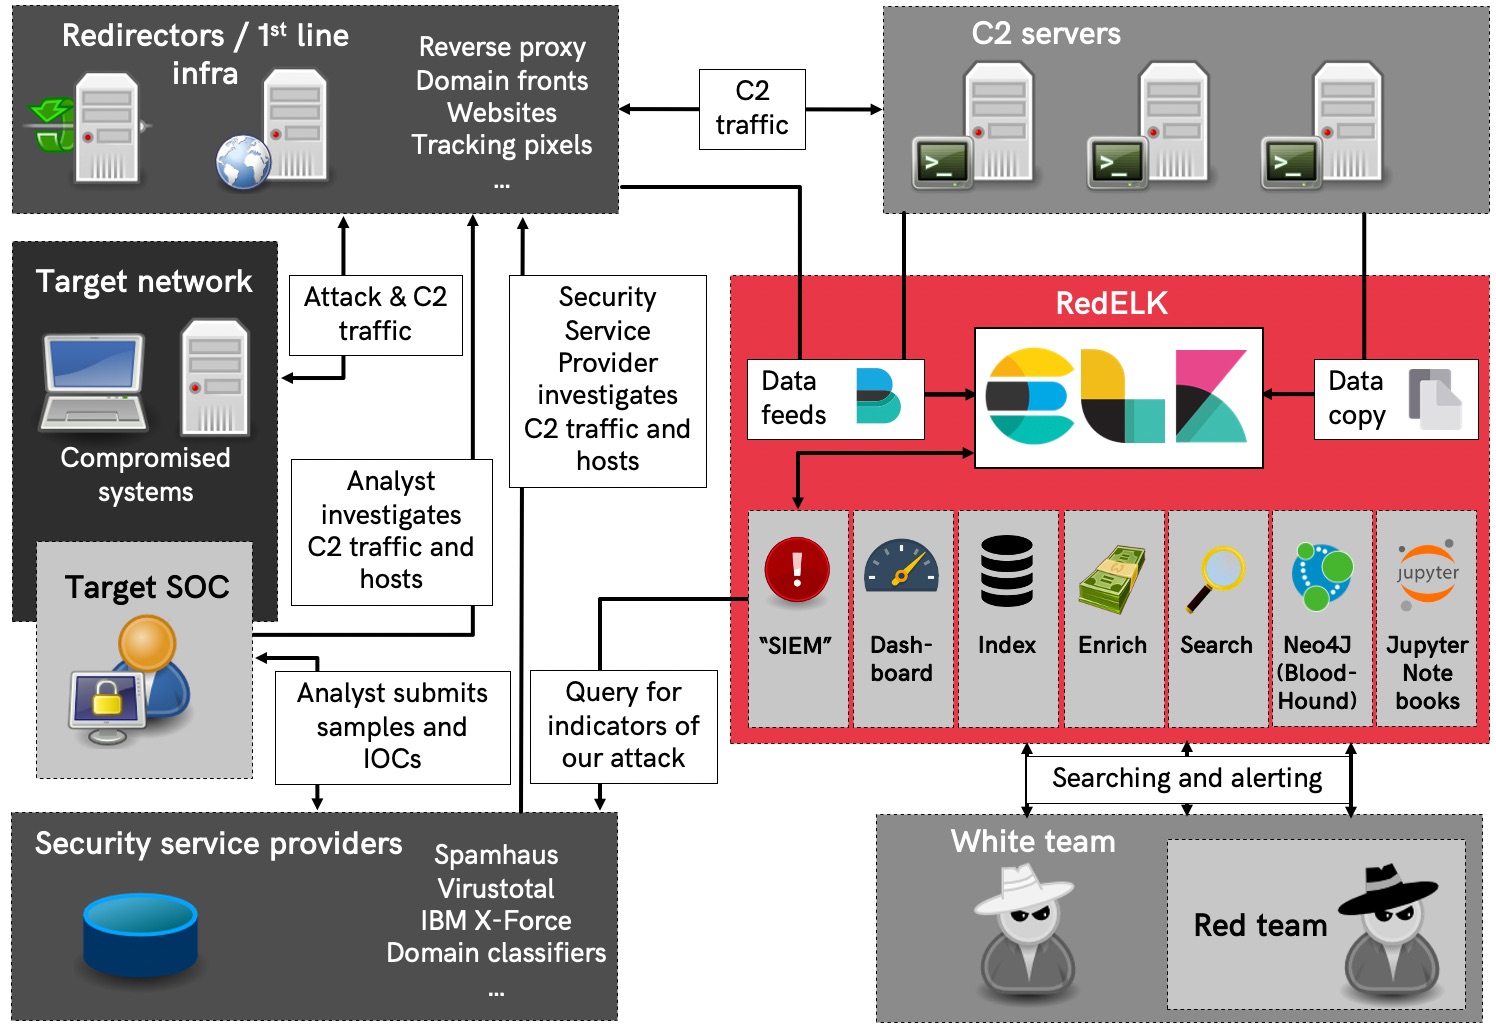
Here's a conceptual overview of how RedELK works.

Authors and contribution

This project is developed and maintained by:

We welcome contributions! Contributions can be both in code, as well as in ideas you might have for further development, alarms, usability improvements, etc.

elastic
elasticsearch
kibana
logstash
monitoring
red-teaming
security
siem

outflanknl/RedELK

Red Team's SIEM - tool for Red Teams used for tracking and alarming about Blue Team activities as well as better usability in long term operations.

Python

2,683

1,086 commits

updated Oct 10, 2026

See the code

README

Build docker base image (dev) Build docker elasticsearch image (dev) Build docker jupyter image (dev) Build docker kibana image (dev) Build docker logstash image (dev)

RedELK

The Red Team's SIEM - a tool for Red Teams for tracking and alarming about Blue Team activities as well as enhanced usability in long term operations.

  1. Enhanced usability and overview for the red team operators by creating a central location where all relevant operational logs from multiple teamservers are collected and enriched. This is great for historic searching within the operation as well as giving a read-only view on the operation (e.g. for the White Team). Especially useful for multi-scenario, multi-teamserver, multi-member and multi-month operations. Also, super easy ways for viewing all screenshots, IOCs, keystrokes output, etc. \o/
  2. Spot the Blue Team by having a central location where all traffic logs from redirectors are collected and enriched. Using specific queries its now possible to detect that the Blue Team is investigating your infrastructure.

Background info

Check the wiki for info on usage or one the blog posts or presentations listed below:

Installation

Check the wiki for manual installation manual. There are also Ansible playbooks maintained by others:

Conceptual overview

Here's a conceptual overview of how RedELK works.
Authors and contribution

This project is developed and maintained by:

We welcome contributions! Contributions can be both in code, as well as in ideas you might have for further development, alarms, usability improvements, etc.

elastic
elasticsearch
kibana
logstash
monitoring
red-teaming
security
siem

Project health

Overall

3.5/10

Maintained

0/10

Code review

0/10
OpenSSF Scorecard

Significant stargazers

YR Chen

63 followers · starred Mar 2024

Henri

79 followers · starred Feb 2019

Chris Goes

110 followers · starred Nov 2023

Mark C.

317 followers · starred Jun 2022
