lightweight, dependency-free bash script for security, performance auditing and infrastructure monitoring of Linux servers.
See the codeA comprehensive Bash script for auditing the security and performance of your VPS (Virtual Private Server). This tool performs various security checks and provides a detailed report with recommendations for improvements.
nuverlabs.com/vps-audit · a Nuver Labs project
pwquality.conf)sudo privilegesufwsystemdnetstat/ssgrepawkwget https://raw.githubusercontent.com/Nuver-Labs/vps-audit/main/vps-audit.sh
# or
curl -O https://raw.githubusercontent.com/Nuver-Labs/vps-audit/main/vps-audit.sh
chmod +x vps-audit.sh
Run the script with sudo privileges:
sudo ./vps-audit.sh
The script will:
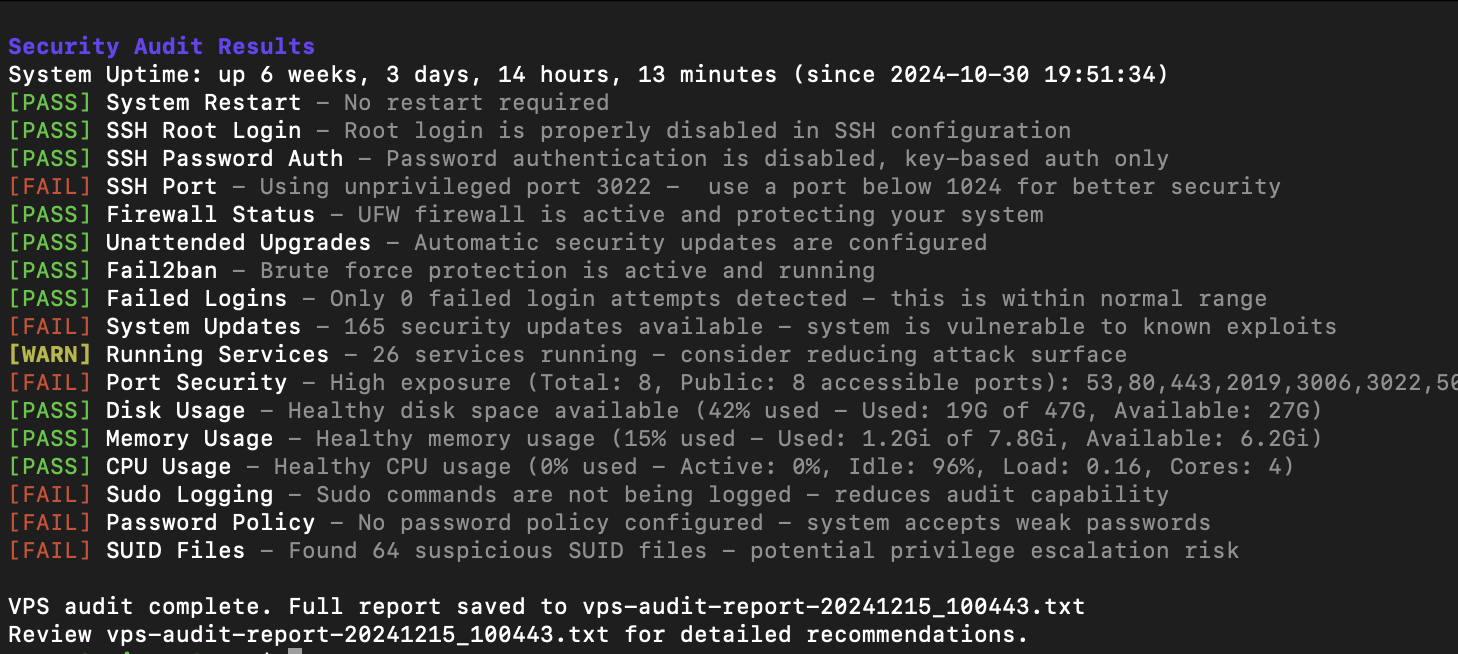
vps-audit-report-[TIMESTAMP].txtThe script provides two types of output:
[PASS] SSH Root Login - Root login is properly disabled in SSH configuration
[WARN] SSH Port - Using default port 22 - consider changing to a non-standard port
[FAIL] Firewall Status - UFW firewall is not active - your system is exposed
The script's behavior, file paths, and scoring limits are fully controlled by variables defined in the Configuration section at the top of the script file.
These variables define the numerical limits that trigger a WARN or FAIL status.
| Variable | Default Value | Check | Description |
|---|---|---|---|
RESOURCE_WARN | 50 | Resource Usage | WARN if Disk/Memory/CPU usage is between 50-80%. |
RESOURCE_FAIL | 80 | Resource Usage | FAIL if Disk/Memory/CPU usage is more than 80%. |
SERVICES_WARN | 20 | Running Services | WARN if between 20-40 services are running. |
SERVICES_FAIL | 40 | Running Services | FAIL if more than 40 services are running. |
LOGINS_WARN | 10 | Failed Logins | WARN if between 10-50 failed login attempts are detected. |
LOGINS_FAIL | 50 | Failed Logins | FAIL if more than 50 failed login attempts are detected. |
OPEN_PORTS_WARN | 10 | Open Ports | WARN if between 10-20 listening ports are found. |
OPEN_PORTS_FAIL | 20 | Open Ports | FAIL if more than 20 listening ports are found. |
PASSWORD_MINLEN | 12 | Password Policy | PASS if minlen in pwquality.conf is at least this value. |
These variables control where the report is saved and the file permissions.
| Variable | Default Value | Description |
|---|---|---|
DEFAULT_REPORT_DIR | . (The current directory) | The directory where the report file will be saved. |
ENABLE_CHOWN | false | If true, sets ownership of the report file and (if newly created) the report directory to REPORT_CHOWN_OWNER. |
REPORT_CHOWN_OWNER | ${SUDO_USER:-$(id -un)}:<their group> | The target user:group for chown. Defaults to the user who invoked sudo, so reports are not left owned by root. |
REPORT_FILENAME | vps-audit-report-$(TIMESTAMP).txt | The template name for the generated report file. |
You can adjust the paths the script uses to check critical configuration files:
| Variable | Default Value | Description |
|---|---|---|
OS_RELEASE_FILE | /etc/os-release | Path to the Operating System release file. |
REBOOT_REQUIRED_FILE | /var/run/reboot-required | File indicating a system restart is needed. |
SSH_CONFIG_FILE | /etc/ssh/sshd_config | Main SSH daemon configuration file. |
AUTH_LOG_FILE | /var/log/auth.log | Log file checked for failed login attempts. |
SUDOERS_FILE | /etc/sudoers | File checked for sudo logging configuration. |
PASSWORD_QUALITY_CONF | /etc/security/pwquality.conf | Password complexity policy configuration file. |
FAIL2BAN_CONFIG_DIR | /etc/fail2ban | Fail2ban config directory, read to verify the SSH jail port. |
Feel free to submit issues and enhancement requests!
This project is licensed under the MIT License - see the LICENSE file for details.
vps-audit is built and maintained by Nuver Labs.
While this script helps identify common security issues, it should not be your only security measure. Always:
For support, please:
Stay secure! 🔒
269 followers · starred Aug 2026
37 followers · starred Mar 2025
231 followers · starred Aug 2026
30 followers · starred Dec 2024
lightweight, dependency-free bash script for security, performance auditing and infrastructure monitoring of Linux servers.
See the codeA comprehensive Bash script for auditing the security and performance of your VPS (Virtual Private Server). This tool performs various security checks and provides a detailed report with recommendations for improvements.
nuverlabs.com/vps-audit · a Nuver Labs project
pwquality.conf)sudo privilegesufwsystemdnetstat/ssgrepawkwget https://raw.githubusercontent.com/Nuver-Labs/vps-audit/main/vps-audit.sh
# or
curl -O https://raw.githubusercontent.com/Nuver-Labs/vps-audit/main/vps-audit.sh
chmod +x vps-audit.sh
Run the script with sudo privileges:
sudo ./vps-audit.sh
The script will:
vps-audit-report-[TIMESTAMP].txtThe script provides two types of output:
[PASS] SSH Root Login - Root login is properly disabled in SSH configuration
[WARN] SSH Port - Using default port 22 - consider changing to a non-standard port
[FAIL] Firewall Status - UFW firewall is not active - your system is exposed
The script's behavior, file paths, and scoring limits are fully controlled by variables defined in the Configuration section at the top of the script file.
These variables define the numerical limits that trigger a WARN or FAIL status.
| Variable | Default Value | Check | Description |
|---|---|---|---|
RESOURCE_WARN | 50 | Resource Usage | WARN if Disk/Memory/CPU usage is between 50-80%. |
RESOURCE_FAIL | 80 | Resource Usage | FAIL if Disk/Memory/CPU usage is more than 80%. |
SERVICES_WARN | 20 | Running Services | WARN if between 20-40 services are running. |
SERVICES_FAIL | 40 | Running Services | FAIL if more than 40 services are running. |
LOGINS_WARN | 10 | Failed Logins | WARN if between 10-50 failed login attempts are detected. |
LOGINS_FAIL | 50 | Failed Logins | FAIL if more than 50 failed login attempts are detected. |
OPEN_PORTS_WARN | 10 | Open Ports | WARN if between 10-20 listening ports are found. |
OPEN_PORTS_FAIL | 20 | Open Ports | FAIL if more than 20 listening ports are found. |
PASSWORD_MINLEN | 12 | Password Policy | PASS if minlen in pwquality.conf is at least this value. |
These variables control where the report is saved and the file permissions.
| Variable | Default Value | Description |
|---|---|---|
DEFAULT_REPORT_DIR | . (The current directory) | The directory where the report file will be saved. |
ENABLE_CHOWN | false | If true, sets ownership of the report file and (if newly created) the report directory to REPORT_CHOWN_OWNER. |
REPORT_CHOWN_OWNER | ${SUDO_USER:-$(id -un)}:<their group> | The target user:group for chown. Defaults to the user who invoked sudo, so reports are not left owned by root. |
REPORT_FILENAME | vps-audit-report-$(TIMESTAMP).txt | The template name for the generated report file. |
You can adjust the paths the script uses to check critical configuration files:
| Variable | Default Value | Description |
|---|---|---|
OS_RELEASE_FILE | /etc/os-release | Path to the Operating System release file. |
REBOOT_REQUIRED_FILE | /var/run/reboot-required | File indicating a system restart is needed. |
SSH_CONFIG_FILE | /etc/ssh/sshd_config | Main SSH daemon configuration file. |
AUTH_LOG_FILE | /var/log/auth.log | Log file checked for failed login attempts. |
SUDOERS_FILE | /etc/sudoers | File checked for sudo logging configuration. |
PASSWORD_QUALITY_CONF | /etc/security/pwquality.conf | Password complexity policy configuration file. |
FAIL2BAN_CONFIG_DIR | /etc/fail2ban | Fail2ban config directory, read to verify the SSH jail port. |
Feel free to submit issues and enhancement requests!
This project is licensed under the MIT License - see the LICENSE file for details.
vps-audit is built and maintained by Nuver Labs.
While this script helps identify common security issues, it should not be your only security measure. Always:
For support, please:
Stay secure! 🔒
269 followers · starred Aug 2026
37 followers · starred Mar 2025
231 followers · starred Aug 2026
30 followers · starred Dec 2024