
Maven central doesn't do SSL when serving you JARs. Dilettante is a MiTM proxy for exploiting that.
Python
159
12 commits
updated Feb 6, 2025
README
Dilettante
More information on my blog here
It turns out that Maven Central only lets you use SSL if you purchase an authentication token for a donation of $10. They claim this $10 will go to the Apache project, but that's besides the point.
SSL encryption requires a separate authentication token. To see what I mean, try opening http://central.maven.org/maven2/org/springframework/ and https://central.maven.org/maven2/org/springframework/ in your browser. This means that package managers like Clojure's lein, Scala's sbt, and maven itself when not specially configured will download JARs without any SSL.
Dilettante is a man in the middle proxy that injects malicious codes into JARs served by Maven Central.
Usage
-
Get in a position where you can man-in-the-middle HTTP traffic. Some hints:
- Buy a wifi router, call it "Starbucks Wifi"
- Install ettercap
- Happen to be an ISP
- Something something
-
Run
dilettante.py -
Proxy your target's http traffic through
localhost:8080- You can do an easy PoC of this by setting the
<proxy>setting in~/.m2/settings.xml
- You can do an easy PoC of this by setting the
Results
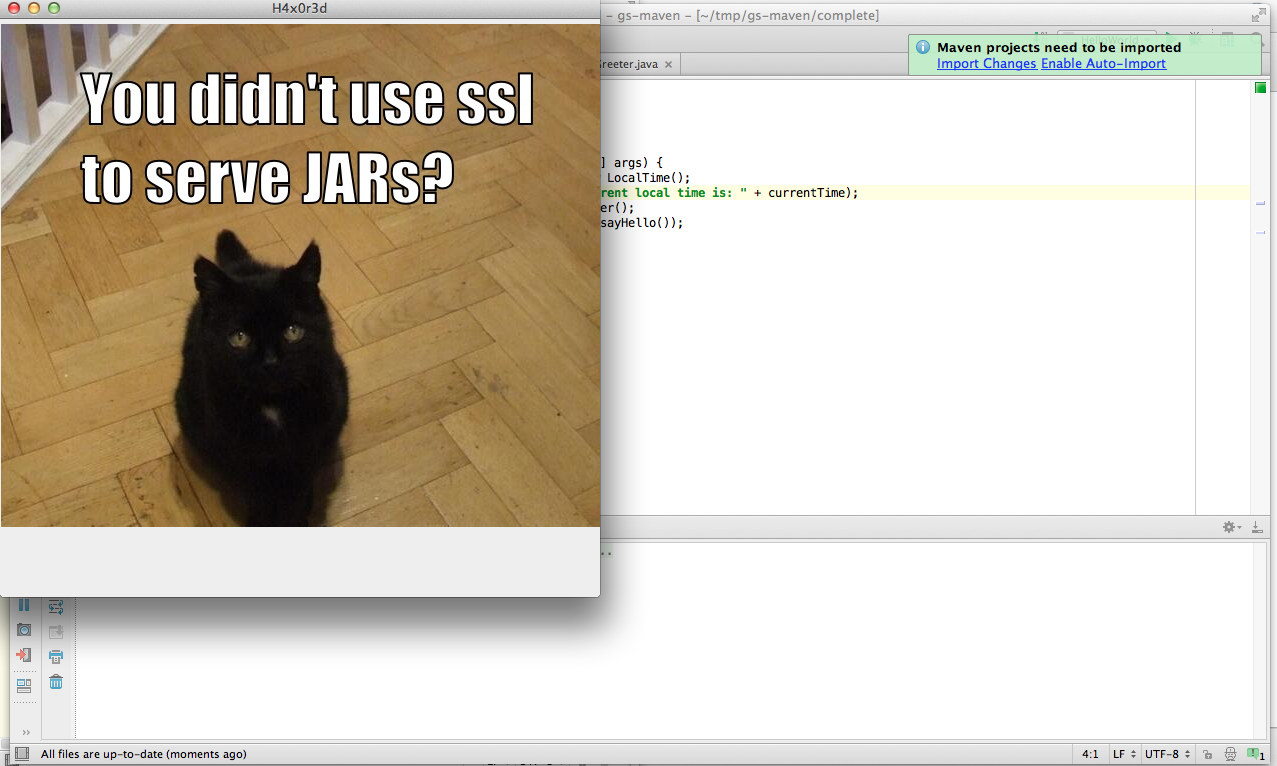
Your victims will get a friendly image when they execute any Java code that uses a JAR that passed through dilettante.
You can see a video here
Contributors

12 commits
Languages
Python
88.9%
Java
11.1%
Maven central doesn't do SSL when serving you JARs. Dilettante is a MiTM proxy for exploiting that.
Python
159
12 commits
updated Feb 6, 2025
README
Dilettante
More information on my blog here
It turns out that Maven Central only lets you use SSL if you purchase an authentication token for a donation of $10. They claim this $10 will go to the Apache project, but that's besides the point.
SSL encryption requires a separate authentication token. To see what I mean, try opening http://central.maven.org/maven2/org/springframework/ and https://central.maven.org/maven2/org/springframework/ in your browser. This means that package managers like Clojure's lein, Scala's sbt, and maven itself when not specially configured will download JARs without any SSL.
Dilettante is a man in the middle proxy that injects malicious codes into JARs served by Maven Central.
Usage
-
Get in a position where you can man-in-the-middle HTTP traffic. Some hints:
- Buy a wifi router, call it "Starbucks Wifi"
- Install ettercap
- Happen to be an ISP
- Something something
-
Run
dilettante.py -
Proxy your target's http traffic through
localhost:8080- You can do an easy PoC of this by setting the
<proxy>setting in~/.m2/settings.xml
- You can do an easy PoC of this by setting the
Results
Your victims will get a friendly image when they execute any Java code that uses a JAR that passed through dilettante.
You can see a video here
Contributors
12 commits
Languages
Python
88.9%
Java
11.1%