This is a collection of tools you may like if you are interested in reverse engineering and/or malware analysis on x86 and x64 Windows systems. After installing this program, you'll have two ways to access the tools:
retoolkit icon in the Desktop.retoolkit. This way the selected file is
passed as argument to the desired program.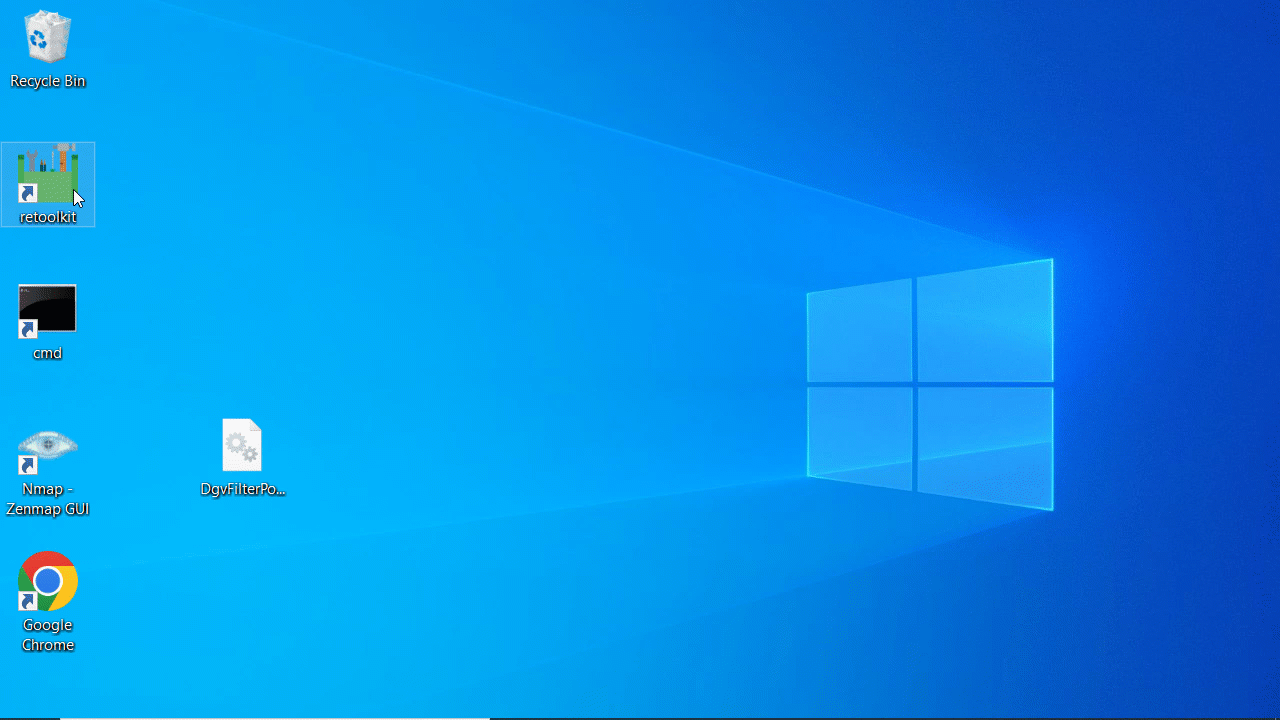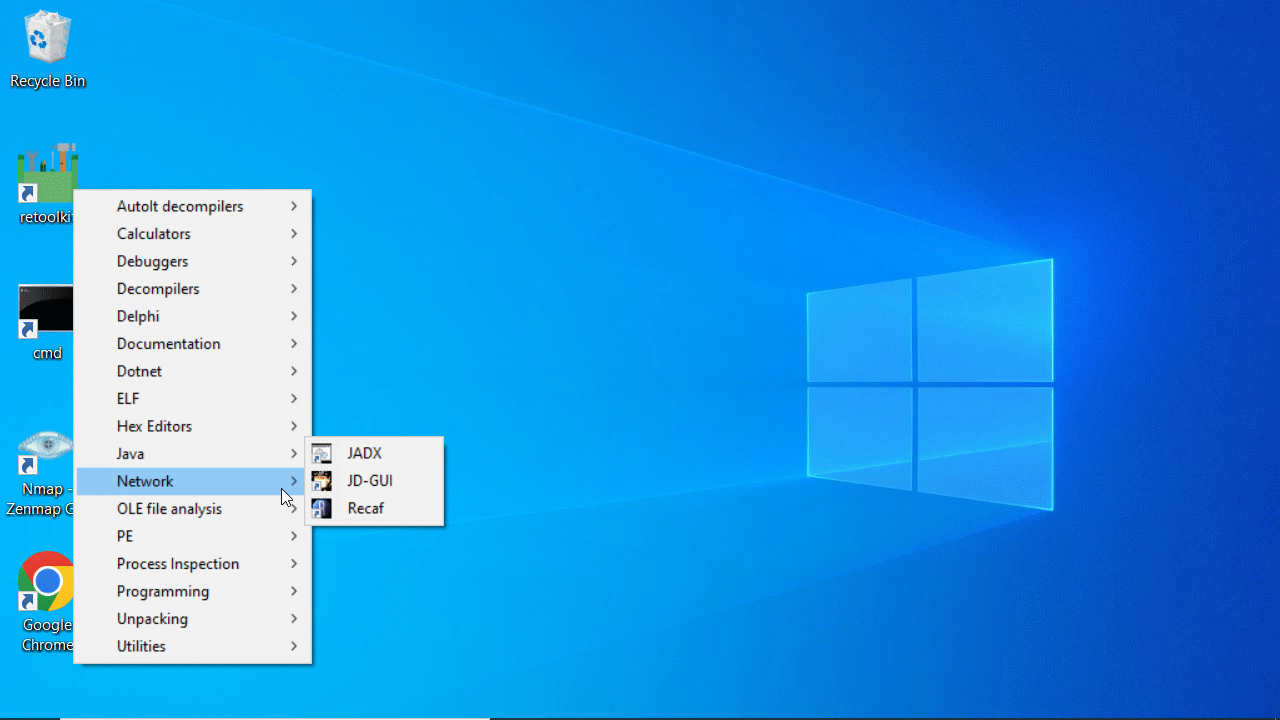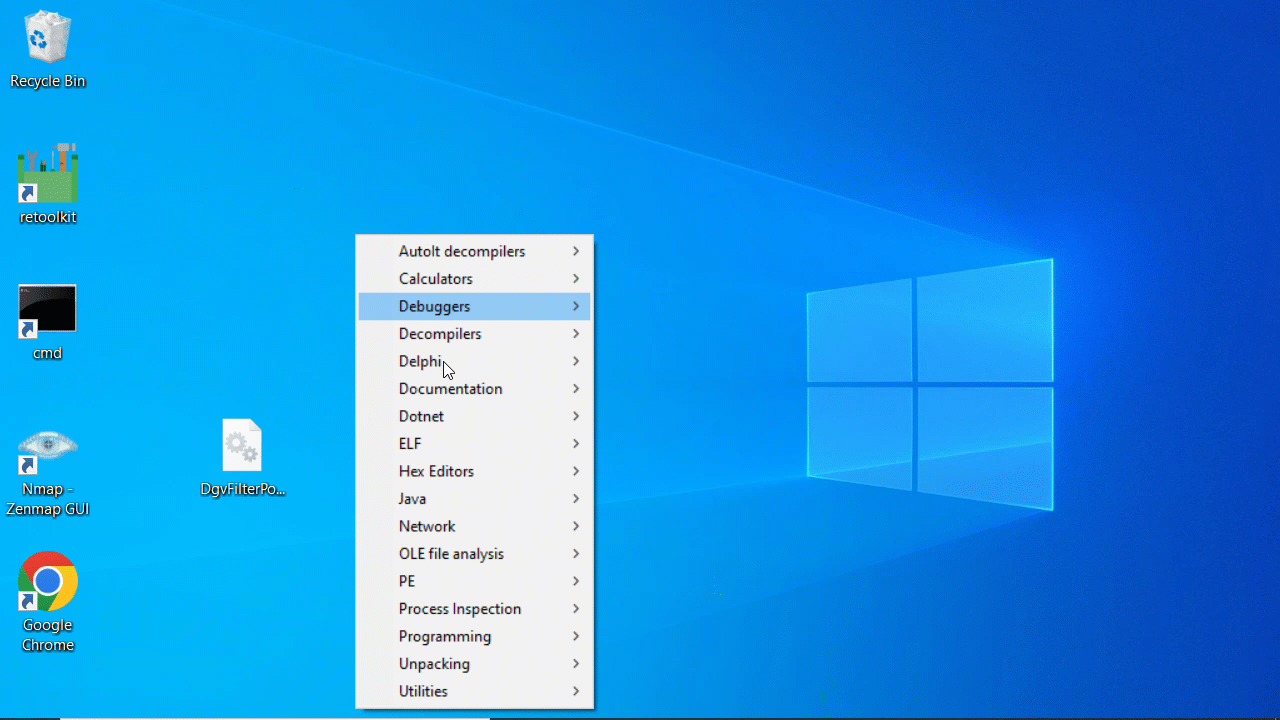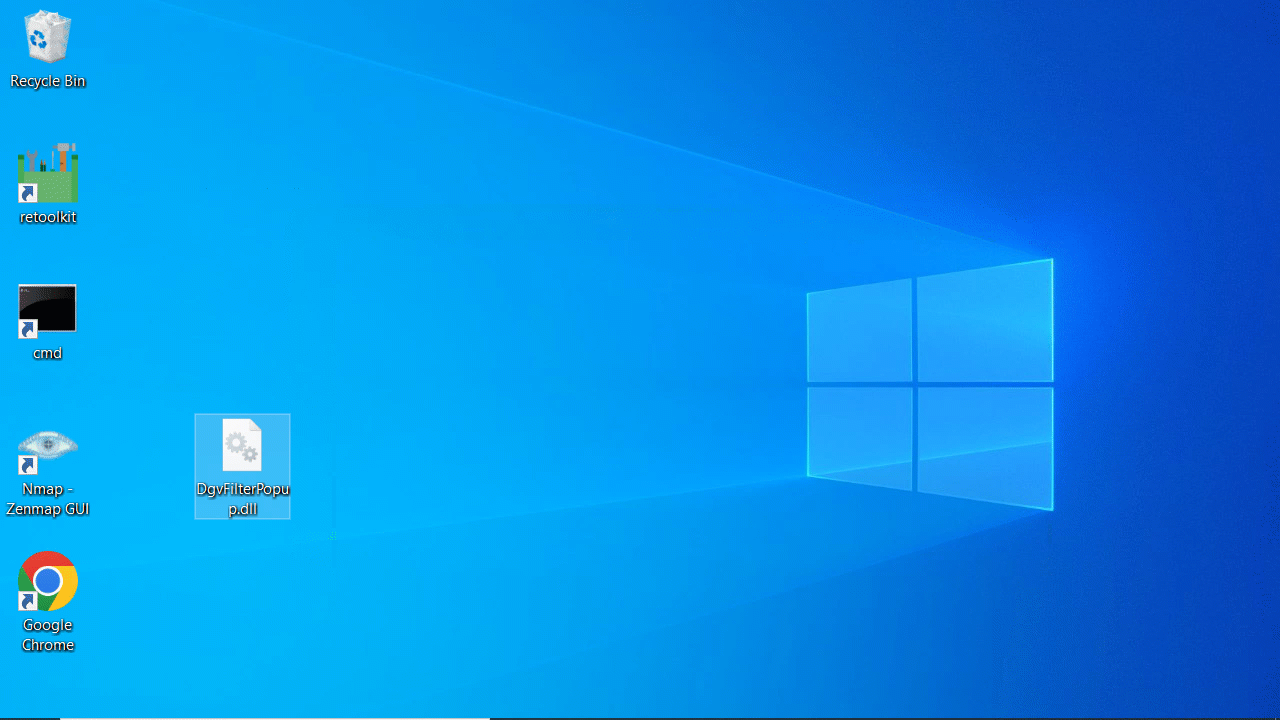
You don't. Obviously, you can download such tools from their own website and install them by yourself in a new VM. But if you download retoolkit, it will probably save you some time. Additionally, the tools come pre-configured so you'll find things like x64dbg with a few plugins, command-line tools working from any directory, etc. You may like it if you're setting up a new analysis VM.
The *.iss files you see here are the source code for our setup program built with Inno Setup. To download the real thing, you have to go to the Releases section and download the setup program.
Have a look at the wiki for a detailed list. By the way, you won't find cracked software there.
I don't know. Some included tools are not open source and come from shady places. You should use it exclusively in virtual machines and under your own responsibility.
Yeah, I prefer to analyze malware without antivirus software installed, but it's up to you. If you want to disable Windows Defender, see this page.
It depends. The idea is to keep it simple. We won't add a tool just because it's not here yet. But if you think there's a good reason to do so, and the license allows us to redistribute the software, please open an issue here if it doesn't exist yet.
See CHANGELOG.md.
This project is inspired by (but not copied from) a toolkit that has been distributed in reverse engineering forums over the years called "Cracker Tools by yildo". I couldn't find an official source for it, although a web search will reveal various copies and references.
The key differences are:
727 followers · starred Aug 2025
2,382 followers · starred Jun 2023
2,811 followers · starred Mar 2021
67 followers · starred May 2022
This is a collection of tools you may like if you are interested in reverse engineering and/or malware analysis on x86 and x64 Windows systems. After installing this program, you'll have two ways to access the tools:
retoolkit icon in the Desktop.retoolkit. This way the selected file is
passed as argument to the desired program.
You don't. Obviously, you can download such tools from their own website and install them by yourself in a new VM. But if you download retoolkit, it will probably save you some time. Additionally, the tools come pre-configured so you'll find things like x64dbg with a few plugins, command-line tools working from any directory, etc. You may like it if you're setting up a new analysis VM.
The *.iss files you see here are the source code for our setup program built with Inno Setup. To download the real thing, you have to go to the Releases section and download the setup program.
Have a look at the wiki for a detailed list. By the way, you won't find cracked software there.
I don't know. Some included tools are not open source and come from shady places. You should use it exclusively in virtual machines and under your own responsibility.
Yeah, I prefer to analyze malware without antivirus software installed, but it's up to you. If you want to disable Windows Defender, see this page.
It depends. The idea is to keep it simple. We won't add a tool just because it's not here yet. But if you think there's a good reason to do so, and the license allows us to redistribute the software, please open an issue here if it doesn't exist yet.
See CHANGELOG.md.
This project is inspired by (but not copied from) a toolkit that has been distributed in reverse engineering forums over the years called "Cracker Tools by yildo". I couldn't find an official source for it, although a web search will reveal various copies and references.
The key differences are:
727 followers · starred Aug 2025
2,382 followers · starred Jun 2023
2,811 followers · starred Mar 2021
67 followers · starred May 2022