
Hyperswitch Encryption Service is an open source Encryption, Decryption and Key Management Service
Rust
29
65 commits
updated Sep 21, 2026
README
Cripta
Overview
A lightweight performant service to Encrypt and Decrypt your data and manage your Encryption Keys in a secure Storage.
The encryption service mainly has following functionalities:-
- Encryption and Decryption: Encrypt and decrypt data using secure algorithms and the managed DEKs.
- Key Management: Generate and Store Keys per entity which will be encrypted by a master key and stored in a secured manner.
- Key Rotation: Rotate DEKs on-demand to enhance security and comply with organizational policies.
How does it work
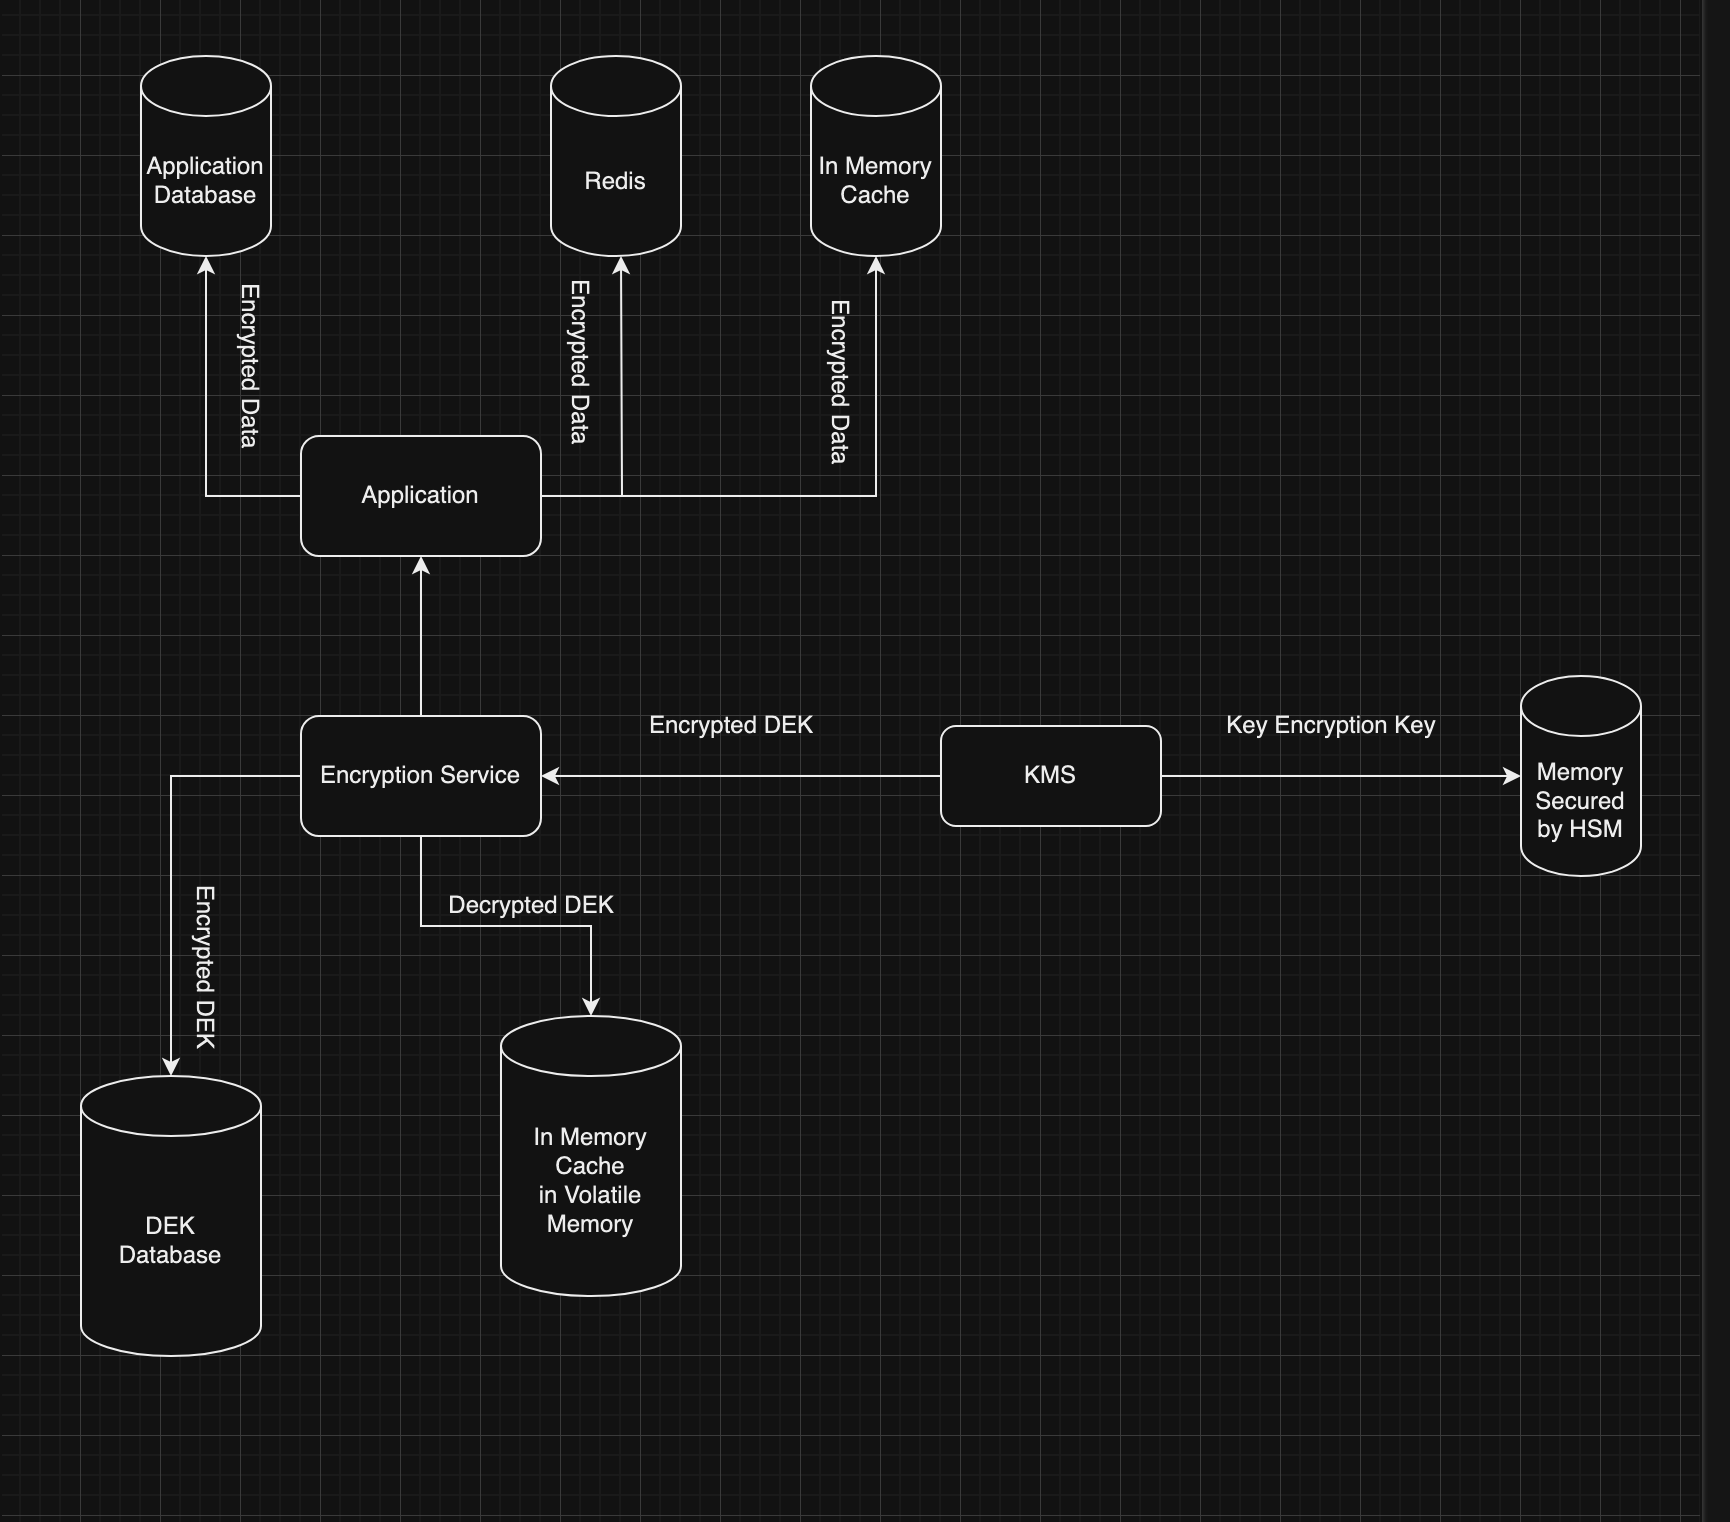
- Application communicates with the service to create a key for the specific entity.
- Next time application has to encrypt/decrypt the data related to the entity, it has to send the entity identifier and the base64-encoded data, the Key Manager will encrypt/decrypt it for the application.
- All the communication between application and the encryption service are authorised by Mutual TLS
- All the Data Encryption Keys are Encrypted by either a securely generated local AES-256 Key or a hosted Key Management Service (AWS KMS, GCP Cloud KMS, HashiCorp Vault), selected at runtime via the
secrets.managerconfig value.
beginner-friendly
finance
hacktoberfest
open-source
rust
security
Contributors


Similar repos


Languages
Rust
97.0%
Shell
2.1%
Hyperswitch Encryption Service is an open source Encryption, Decryption and Key Management Service
Rust
29
65 commits
updated Sep 21, 2026
README
Cripta
Overview
A lightweight performant service to Encrypt and Decrypt your data and manage your Encryption Keys in a secure Storage.
The encryption service mainly has following functionalities:-
- Encryption and Decryption: Encrypt and decrypt data using secure algorithms and the managed DEKs.
- Key Management: Generate and Store Keys per entity which will be encrypted by a master key and stored in a secured manner.
- Key Rotation: Rotate DEKs on-demand to enhance security and comply with organizational policies.
How does it work
- Application communicates with the service to create a key for the specific entity.
- Next time application has to encrypt/decrypt the data related to the entity, it has to send the entity identifier and the base64-encoded data, the Key Manager will encrypt/decrypt it for the application.
- All the communication between application and the encryption service are authorised by Mutual TLS
- All the Data Encryption Keys are Encrypted by either a securely generated local AES-256 Key or a hosted Key Management Service (AWS KMS, GCP Cloud KMS, HashiCorp Vault), selected at runtime via the
secrets.managerconfig value.
beginner-friendly
finance
hacktoberfest
open-source
rust
security
Similar repos
Contributors
Languages
Rust
97.0%
Shell
2.1%