
Open source toolkit created to enable easy adoption of software enclaves
See the codeREADME
Enclaver is an open source toolkit created to enable easy adoption of software enclaves, for new and existing backend software.
Enclaves provide several critical features for operating software which processes sensitive data, including:
- Isolation: Enclaves enable a deny-by-default approach to accessing process memory. Software running in an enclave can expose interfaces for accessing specific data, while disallowing humans or other software on the same computer from reading arbitrary data from memory.
- Attestation: Enclaves make it possible to determine the exact identity and configuration of software running in an enclave.
- Network Restrictions: External communication is limited and controlled. The network policy is built into the image and therefore the software attestation.
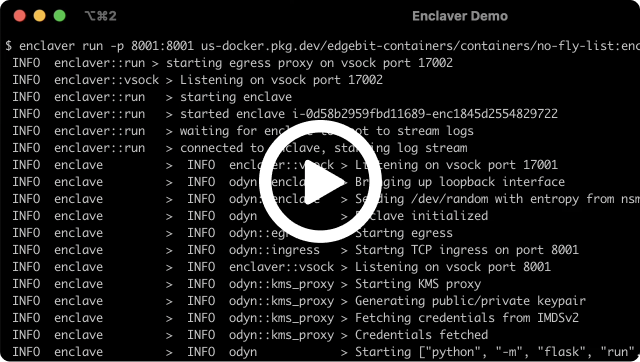
These demos show off how your apps can use these unique features to improve privacy and security:
- Run a simple Python app that represents a microservice or security-centric function
- Run Hashicorp Vault to fully isolate it after it's unsealed
Project State
Enclaver is currently in beta and should be used cautiously in production. Enclaver currently only supports AWS Nitro Enclaves; support for Azure Confidential VMs, GCP Confidential VMs, and arbitrary SGX and OP-TEE enclaves is on the roadmap.
Architecture
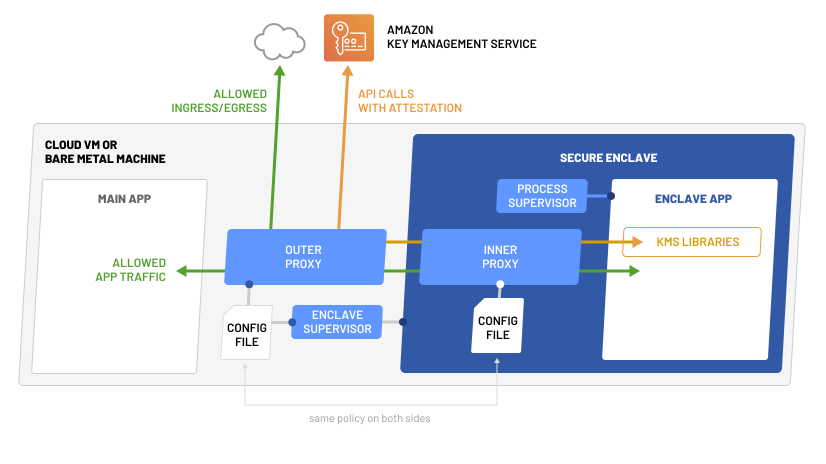
Read the architecture doc for the full details. Enclaver consists of 3 interrelated pieces of software:
enclaverCLI for build and run- “Outer Proxy” + Enclave Supervisor
- “Inner Proxy” + Process Supervisor
FAQ
See the FAQ for common questions and a comparison of Enclaver to similar technologies.
Reporting Security Bugs
Report security bugs confidentially at security@enclaver.io
Contributors


Similar repos


Languages
Rust
97.5%
Open source toolkit created to enable easy adoption of software enclaves
See the codeREADME
Enclaver is an open source toolkit created to enable easy adoption of software enclaves, for new and existing backend software.
Enclaves provide several critical features for operating software which processes sensitive data, including:
- Isolation: Enclaves enable a deny-by-default approach to accessing process memory. Software running in an enclave can expose interfaces for accessing specific data, while disallowing humans or other software on the same computer from reading arbitrary data from memory.
- Attestation: Enclaves make it possible to determine the exact identity and configuration of software running in an enclave.
- Network Restrictions: External communication is limited and controlled. The network policy is built into the image and therefore the software attestation.
These demos show off how your apps can use these unique features to improve privacy and security:
- Run a simple Python app that represents a microservice or security-centric function
- Run Hashicorp Vault to fully isolate it after it's unsealed
Project State
Enclaver is currently in beta and should be used cautiously in production. Enclaver currently only supports AWS Nitro Enclaves; support for Azure Confidential VMs, GCP Confidential VMs, and arbitrary SGX and OP-TEE enclaves is on the roadmap.
Architecture
Read the architecture doc for the full details. Enclaver consists of 3 interrelated pieces of software:
enclaverCLI for build and run- “Outer Proxy” + Enclave Supervisor
- “Inner Proxy” + Process Supervisor
FAQ
See the FAQ for common questions and a comparison of Enclaver to similar technologies.
Reporting Security Bugs
Report security bugs confidentially at security@enclaver.io
Similar repos
Contributors
Languages
Rust
97.5%