
🪓 High-Speed Log Analysis & Forensics Tool - Part of NullSec Toolkit
C
83
7 commits
updated Apr 16, 2026
README
🪓 LogReaper v1.0
High-Speed Log Analysis & Forensics Tool




Blazing-fast log analysis for incident response, threat hunting, and forensic investigations
🎬 Demo
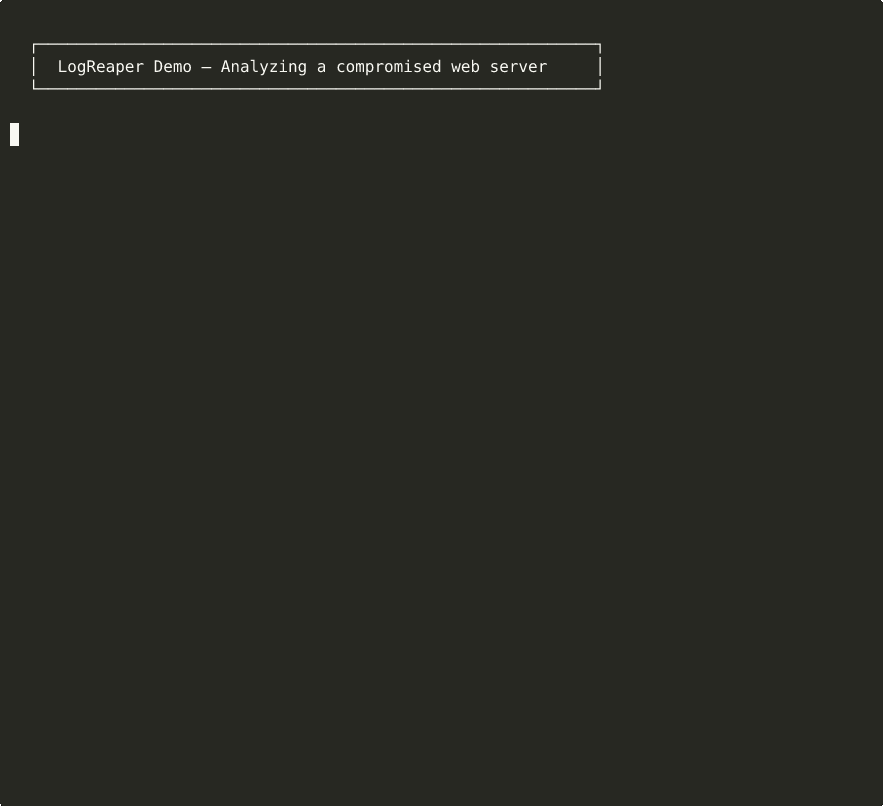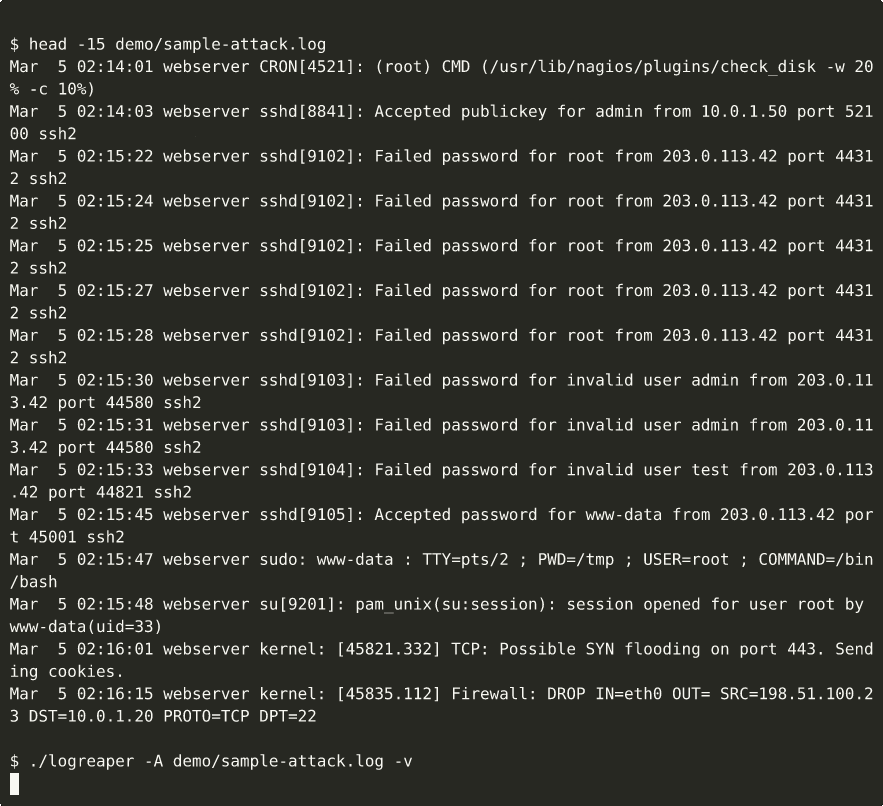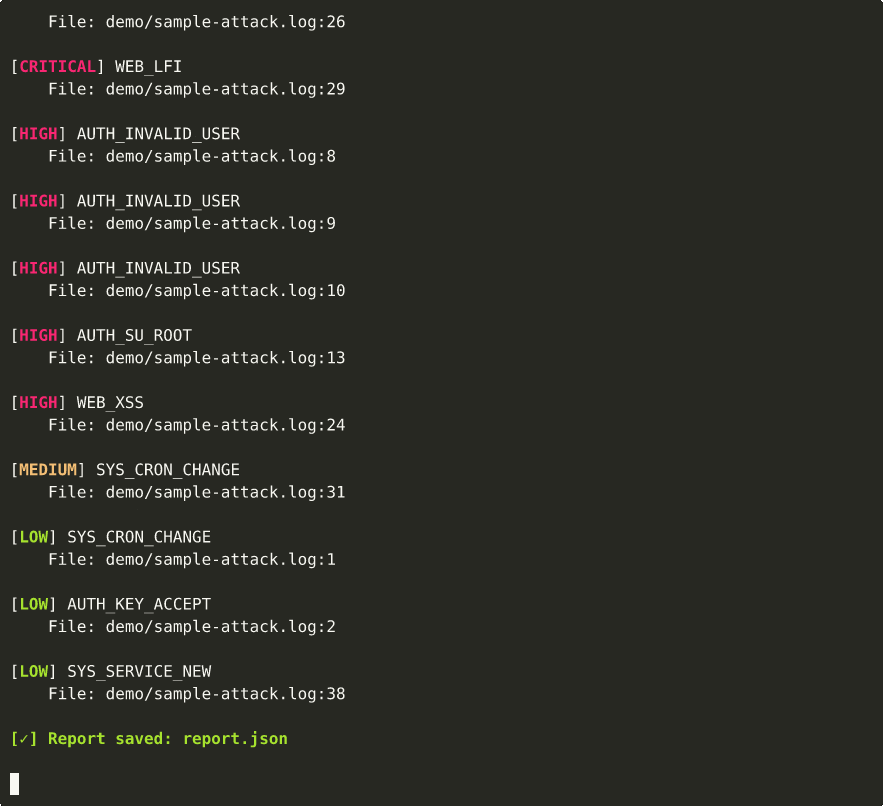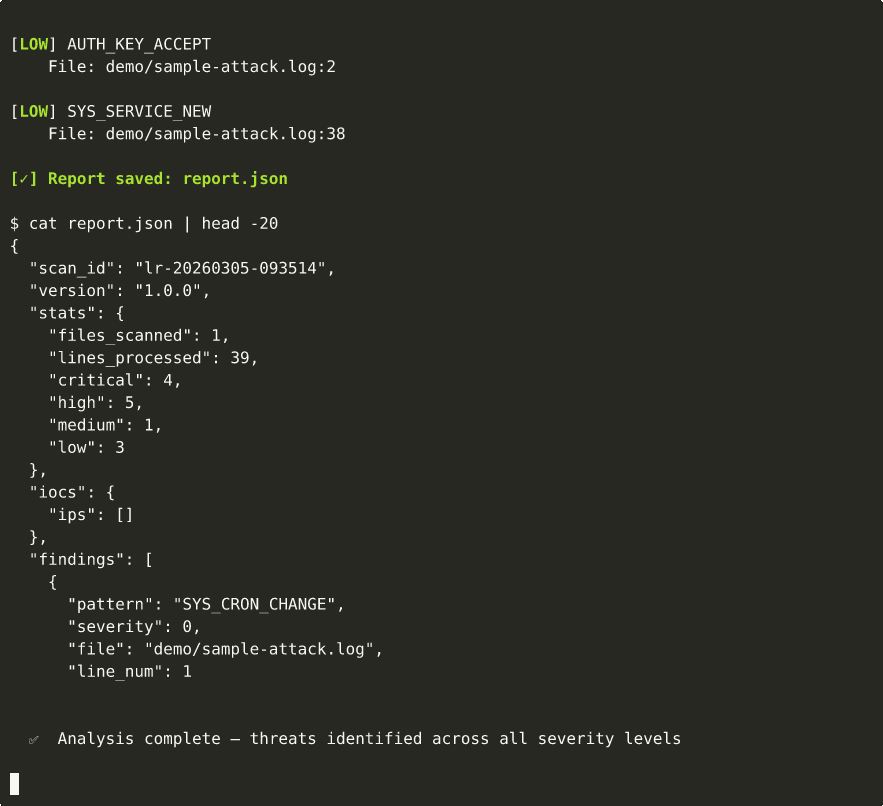
LogReaper scanning a compromised web server — detecting SQLi, XSS, LFI, brute force, and privilege escalation in seconds
Try it yourself: A sample attack log is included at
demo/sample-attack.log./logreaper -A demo/sample-attack.log -v
💻 Tech Stack
Core


Log Sources


Output Formats


🎯 Features
🔬 Analysis Modules (8)
|
📋 Supported Logs (25+)
|
🚀 Quick Start
Installation
# Clone and build
git clone https://github.com/bad-antics/nullsec-logreaper
cd nullsec-logreaper
make

# Install system-wide (optional)
sudo make install
Basic Usage
# Analyze auth logs for brute force
./logreaper -a /var/log/auth.log

# Hunt for web attacks
./logreaper -w /var/log/nginx/access.log

# Full system analysis with timeline
./logreaper -t /var/log/

# Real-time monitoring
./logreaper -l /var/log/syslog

# Extract IOCs to JSON
./logreaper -i /var/log/ -o iocs.json
📊 Detection Patterns
Authentication Threats
| Pattern | Description | Severity |
|---|---|---|
AUTH_BRUTE_SSH | SSH brute force attempts | 🔴 High |
AUTH_SUDO_ABUSE | Unusual sudo usage | 🟡 Medium |
AUTH_SU_ROOT | Privilege escalation via su | 🔴 High |
AUTH_FAIL_BURST | Rapid auth failures | 🔴 High |
AUTH_NEW_USER | New user created | 🟡 Medium |
AUTH_PASSWD_CHG | Password changed | 🟡 Medium |
Web Attack Signatures
| Pattern | Description | Severity |
|---|---|---|
WEB_SQLI | SQL injection attempts | 🔴 Critical |
WEB_XSS | Cross-site scripting | 🔴 High |
WEB_LFI | Local file inclusion | 🔴 Critical |
WEB_RFI | Remote file inclusion | 🔴 Critical |
WEB_PATH_TRAV | Path traversal (../) | 🔴 High |
WEB_CMD_INJ | Command injection | 🔴 Critical |
WEB_SCANNER | Automated scanner detected | 🟡 Medium |
System Anomalies
| Pattern | Description | Severity |
|---|---|---|
SYS_KERNEL_MOD | Kernel module loaded | 🟡 Medium |
SYS_SELINUX_OFF | SELinux disabled | 🔴 High |
SYS_CRON_CHANGE | Cron job modified | 🟡 Medium |
SYS_SERVICE_NEW | New systemd service | 🟡 Medium |
SYS_MOUNT_EXEC | Exec mount option | 🟡 Medium |
📈 Output Formats
JSON Report
{
  "scan_id": "lr-20250127-143022",
  "total_events": 15847,
  "threats_found": 23,
  "timeline": [...],
  "iocs": {
    "ips": ["192.168.1.100", "10.0.0.5"],
    "domains": ["evil.example.com"],
    "hashes": []
  },
  "findings": [...]
}
Terminal Output
║                    🪓 LogReaper v1.0                         ║
║  Target: /var/log/auth.log                                   ║
║  Lines:  15,847                                              ║
║  Period: 2025-01-20 → 2025-01-27                             ║
║  🔴 CRITICAL  │ 3                                            ║
║  🟠 HIGH      │ 12                                           ║
║  🟡 MEDIUM    │ 8                                            ║
║  🟢 LOW       │ 0                                            ║

[!] AUTH_BRUTE_SSH detected
    Time:   2025-01-26 14:32:15
    Source: 192.168.1.100
    Count:  847 attempts in 5 minutes
    User:   root, admin, ubuntu
🔧 Advanced Usage
Timeline Correlation
# Build attack timeline from multiple sources
./logreaper -t \
    /var/log/auth.log \
    /var/log/nginx/access.log \
    /var/log/syslog \
    -o timeline.json
IOC Extraction for SIEM
# Extract IOCs in Splunk-compatible format
./logreaper -i /var/log/ --format splunk > iocs.txt

# Extract for ELK Stack
./logreaper -i /var/log/ --format elastic | curl -X POST ...
Integration with RKHunt
# Run LogReaper → pipe suspicious IPs to firewall
./logreaper -a /var/log/auth.log --extract-ips | \
    xargs -I {} iptables -A INPUT -s {} -j DROP

# Correlate with RKHunt findings
./logreaper -s /var/log/syslog | grep -f <(rkhunt --list-iocs)
🛠️ Build Options
# Standard build
make

# Build with debug symbols
make DEBUG=1

# Build with PCRE2 regex (faster patterns)
make PCRE2=1

# Build static binary
make STATIC=1

# Cross-compile for ARM64
make ARCH=aarch64
📁 Project Structure
nullsec-logreaper/
├── src/
│   ├── main.c           # Entry point, arg parsing
│   ├── parser.c         # Log format parsers
│   ├── analyzer.c       # Pattern matching engine
│   ├── timeline.c       # Event correlation
│   ├── output.c         # Report generation
│   ├── patterns.h       # Detection signatures
│   └── utils.c          # Helper functions
├── patterns/
│   ├── auth.rules       # Authentication patterns
│   ├── web.rules        # Web attack signatures
│   └── system.rules     # System anomaly patterns
├── Makefile
├── LICENSE
└── README.md
🔗 NullSec Toolkit Integration
LogReaper works seamlessly with other NullSec tools:
| Tool | Integration |
|---|---|
| RKHunt | Correlate rootkit indicators with log anomalies |
| Specter | Feed extracted IOCs for threat intelligence |
| NetSniff | Combine network + log analysis |
| MemScan | Timeline memory artifacts with system logs |
📜 License
MIT License - See LICENSE for details.
Part of the NullSec Toolkit
"From logs to leads."
Contributors

7 commits
Similar repos


Languages
C
97.8%
Makefile
2.2%
🪓 High-Speed Log Analysis & Forensics Tool - Part of NullSec Toolkit
C
83
7 commits
updated Apr 16, 2026
README
🪓 LogReaper v1.0
High-Speed Log Analysis & Forensics Tool
Blazing-fast log analysis for incident response, threat hunting, and forensic investigations
🎬 Demo
LogReaper scanning a compromised web server — detecting SQLi, XSS, LFI, brute force, and privilege escalation in seconds
Try it yourself: A sample attack log is included at
demo/sample-attack.log./logreaper -A demo/sample-attack.log -v
💻 Tech Stack
Core
Log Sources
Output Formats
🎯 Features
🔬 Analysis Modules (8)
|
📋 Supported Logs (25+)
|
🚀 Quick Start
Installation
# Clone and build
git clone https://github.com/bad-antics/nullsec-logreaper
cd nullsec-logreaper
make

# Install system-wide (optional)
sudo make install
Basic Usage
# Analyze auth logs for brute force
./logreaper -a /var/log/auth.log

# Hunt for web attacks
./logreaper -w /var/log/nginx/access.log

# Full system analysis with timeline
./logreaper -t /var/log/

# Real-time monitoring
./logreaper -l /var/log/syslog

# Extract IOCs to JSON
./logreaper -i /var/log/ -o iocs.json
📊 Detection Patterns
Authentication Threats
| Pattern | Description | Severity |
|---|---|---|
AUTH_BRUTE_SSH | SSH brute force attempts | 🔴 High |
AUTH_SUDO_ABUSE | Unusual sudo usage | 🟡 Medium |
AUTH_SU_ROOT | Privilege escalation via su | 🔴 High |
AUTH_FAIL_BURST | Rapid auth failures | 🔴 High |
AUTH_NEW_USER | New user created | 🟡 Medium |
AUTH_PASSWD_CHG | Password changed | 🟡 Medium |
Web Attack Signatures
| Pattern | Description | Severity |
|---|---|---|
WEB_SQLI | SQL injection attempts | 🔴 Critical |
WEB_XSS | Cross-site scripting | 🔴 High |
WEB_LFI | Local file inclusion | 🔴 Critical |
WEB_RFI | Remote file inclusion | 🔴 Critical |
WEB_PATH_TRAV | Path traversal (../) | 🔴 High |
WEB_CMD_INJ | Command injection | 🔴 Critical |
WEB_SCANNER | Automated scanner detected | 🟡 Medium |
System Anomalies
| Pattern | Description | Severity |
|---|---|---|
SYS_KERNEL_MOD | Kernel module loaded | 🟡 Medium |
SYS_SELINUX_OFF | SELinux disabled | 🔴 High |
SYS_CRON_CHANGE | Cron job modified | 🟡 Medium |
SYS_SERVICE_NEW | New systemd service | 🟡 Medium |
SYS_MOUNT_EXEC | Exec mount option | 🟡 Medium |
📈 Output Formats
JSON Report
{
  "scan_id": "lr-20250127-143022",
  "total_events": 15847,
  "threats_found": 23,
  "timeline": [...],
  "iocs": {
    "ips": ["192.168.1.100", "10.0.0.5"],
    "domains": ["evil.example.com"],
    "hashes": []
  },
  "findings": [...]
}
Terminal Output
║                    🪓 LogReaper v1.0                         ║
║  Target: /var/log/auth.log                                   ║
║  Lines:  15,847                                              ║
║  Period: 2025-01-20 → 2025-01-27                             ║
║  🔴 CRITICAL  │ 3                                            ║
║  🟠 HIGH      │ 12                                           ║
║  🟡 MEDIUM    │ 8                                            ║
║  🟢 LOW       │ 0                                            ║

[!] AUTH_BRUTE_SSH detected
    Time:   2025-01-26 14:32:15
    Source: 192.168.1.100
    Count:  847 attempts in 5 minutes
    User:   root, admin, ubuntu
🔧 Advanced Usage
Timeline Correlation
# Build attack timeline from multiple sources
./logreaper -t \
    /var/log/auth.log \
    /var/log/nginx/access.log \
    /var/log/syslog \
    -o timeline.json
IOC Extraction for SIEM
# Extract IOCs in Splunk-compatible format
./logreaper -i /var/log/ --format splunk > iocs.txt

# Extract for ELK Stack
./logreaper -i /var/log/ --format elastic | curl -X POST ...
Integration with RKHunt
# Run LogReaper → pipe suspicious IPs to firewall
./logreaper -a /var/log/auth.log --extract-ips | \
    xargs -I {} iptables -A INPUT -s {} -j DROP

# Correlate with RKHunt findings
./logreaper -s /var/log/syslog | grep -f <(rkhunt --list-iocs)
🛠️ Build Options
# Standard build
make

# Build with debug symbols
make DEBUG=1

# Build with PCRE2 regex (faster patterns)
make PCRE2=1

# Build static binary
make STATIC=1

# Cross-compile for ARM64
make ARCH=aarch64
📁 Project Structure
nullsec-logreaper/
├── src/
│   ├── main.c           # Entry point, arg parsing
│   ├── parser.c         # Log format parsers
│   ├── analyzer.c       # Pattern matching engine
│   ├── timeline.c       # Event correlation
│   ├── output.c         # Report generation
│   ├── patterns.h       # Detection signatures
│   └── utils.c          # Helper functions
├── patterns/
│   ├── auth.rules       # Authentication patterns
│   ├── web.rules        # Web attack signatures
│   └── system.rules     # System anomaly patterns
├── Makefile
├── LICENSE
└── README.md
🔗 NullSec Toolkit Integration
LogReaper works seamlessly with other NullSec tools:
| Tool | Integration |
|---|---|
| RKHunt | Correlate rootkit indicators with log anomalies |
| Specter | Feed extracted IOCs for threat intelligence |
| NetSniff | Combine network + log analysis |
| MemScan | Timeline memory artifacts with system logs |
📜 License
MIT License - See LICENSE for details.
Part of the NullSec Toolkit
"From logs to leads."
Similar repos
Contributors
7 commits
Languages
C
97.8%
Makefile
2.2%