An step by step fuzzing tutorial. A GitHub Security Lab initiative
See the codeDo you want to learn how to fuzz like a real expert, but don't know how to start?
If so, this is the course for you!
10 real targets, 10 exercises. Are you able to solve all 10?
| Exercise No. | Target | CVEs to find | Time estimated | Main topics |
|---|---|---|---|---|
| Exercise 1 | Xpdf | CVE-2019-13288 | 120 mins | Afl-clang-fast, Afl-fuzz, GDB |
| Exercise 2 | libexif | CVE-2009-3895, CVE-2012-2836 | 6 hours | Afl-clang-lto, Fuzz libraries, Eclipse IDE |
| Exercise 3 | TCPdump | CVE-2017-13028 | 4 hours | ASan, Sanitizers |
| Exercise 4 | LibTIFF | CVE-2016-9297 | 3 hours | Code coverage, LCOV |
| Exercise 5 | Libxml2 | CVE-2017-9048 | 3 hours | Dictionaries, Basic parallelization, Fuzzing command-line arguments |
| Exercise 6 | GIMP | CVE-2016-4994, Bonus bugs | 7 hours | Persistent fuzzing, Fuzzing interactive applications |
| Exercise 7 | VLC media player | CVE-2019-14776 | 6 hours | Partial instrumentation, Fuzzing harness |
| Exercise 8 | Adobe Reader | 8 hours | Fuzzing closed-source applications, QEMU instrumentation | |
| Exercise 9 | 7-Zip | CVE-2016-2334 | 8 hours | WinAFL, Fuzzing Windows Applications |
| Exercise 10 (Final Challenge) | Google Chrome / V8 | CVE-2019-5847 | 8 hours | Fuzzilli, Fuzzing Javascript engines |
Fuzz testing (or fuzzing) is an automated software testing technique that is based on feeding the program with random/mutated input values and monitoring it for exceptions/crashes.
AFL, libFuzzer and HonggFuzz are three of the most successful fuzzers when it comes to real world applications. All three are examples of Coverage-guided evolutionary fuzzers.
Evolutionary: is a metaheuristic approach inspired by evolutionary algorithms, which basically consists in the evolution and mutation of the initial subset (seeds) over time, by using a selection criteria (ex. coverage).
Coverage-guided: To increase the chance of finding new crashes, coverage-guided fuzzers gather and compare code coverage data between different inputs (usually through instrumentation) and pick those inputs which lead to new execution paths.
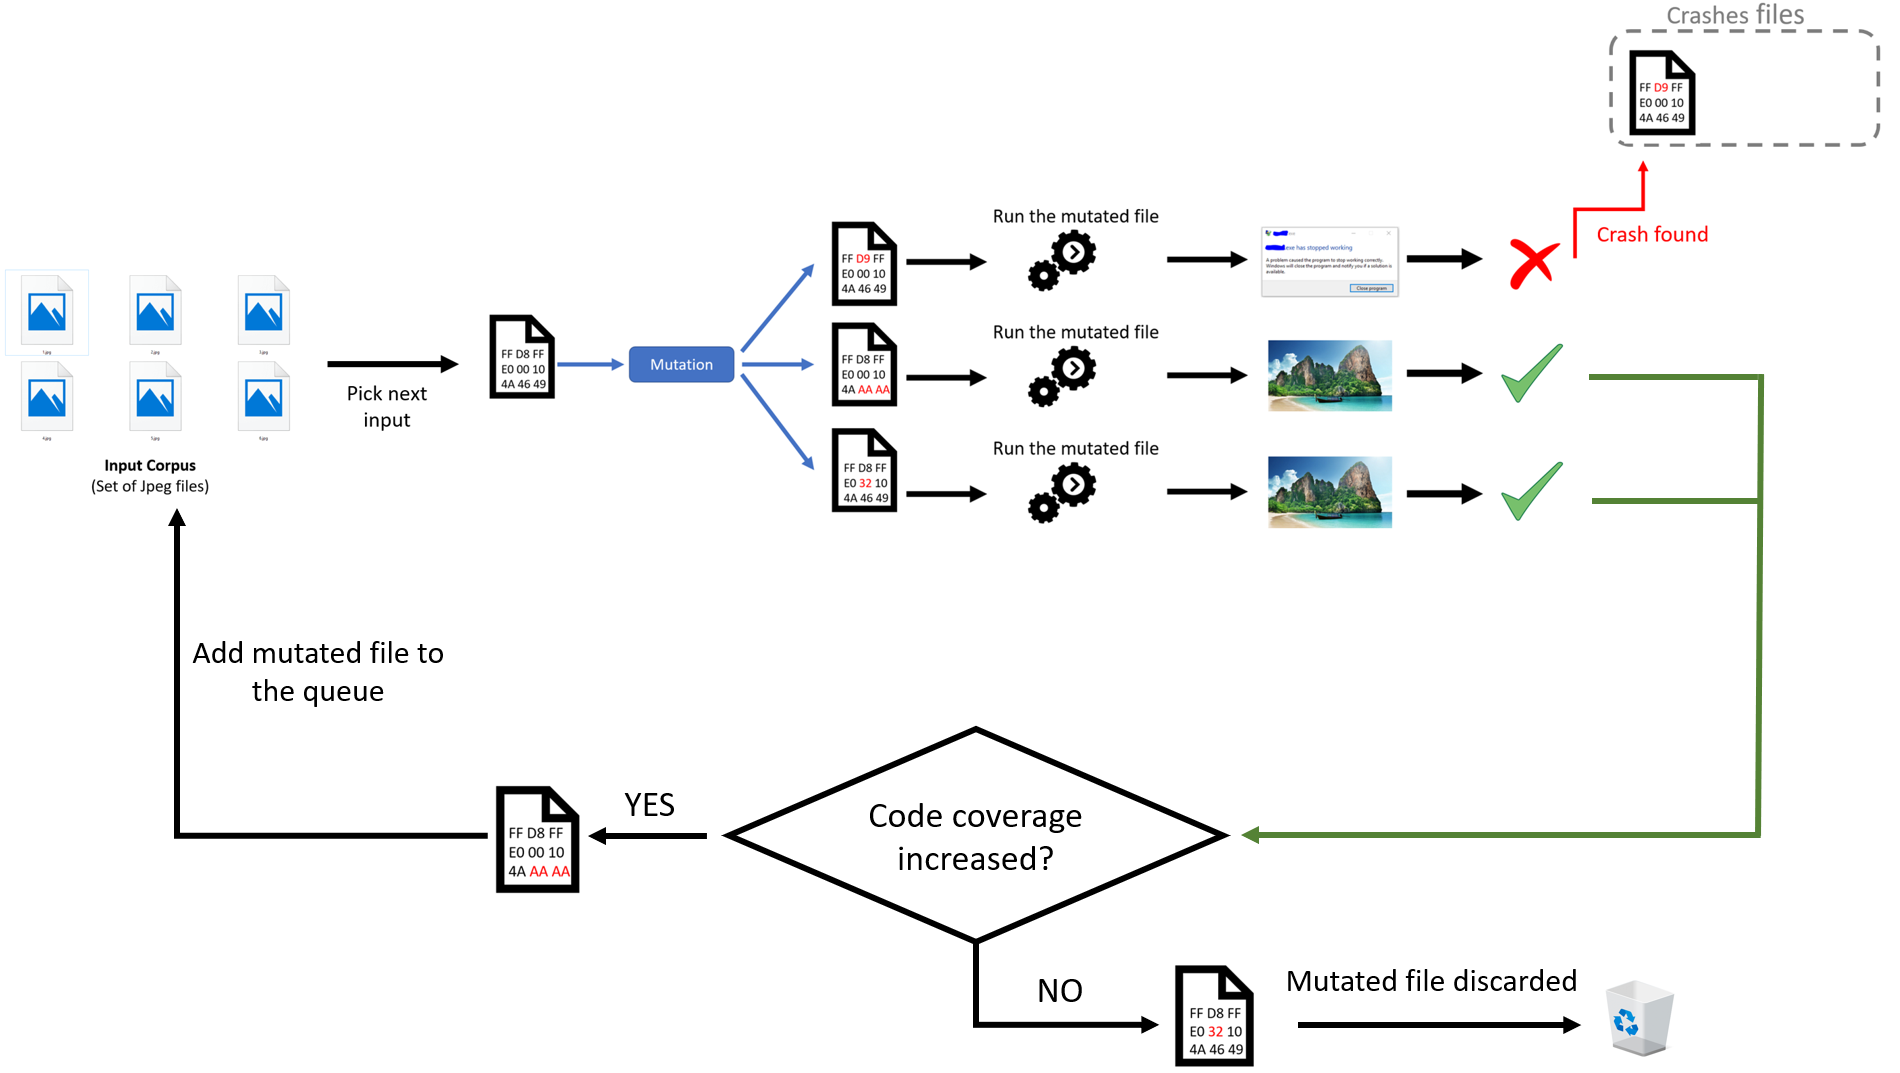
Simplification of the coverage gathering process of a coverage-guided evolutionary fuzzer
Thanks for their help:
(top 24 of 52)
475 followers · starred Mar 2022
105 followers · starred Aug 2021
203 followers · starred Oct 2024
156 followers · starred Oct 2024
An step by step fuzzing tutorial. A GitHub Security Lab initiative
See the codeDo you want to learn how to fuzz like a real expert, but don't know how to start?
If so, this is the course for you!
10 real targets, 10 exercises. Are you able to solve all 10?
| Exercise No. | Target | CVEs to find | Time estimated | Main topics |
|---|---|---|---|---|
| Exercise 1 | Xpdf | CVE-2019-13288 | 120 mins | Afl-clang-fast, Afl-fuzz, GDB |
| Exercise 2 | libexif | CVE-2009-3895, CVE-2012-2836 | 6 hours | Afl-clang-lto, Fuzz libraries, Eclipse IDE |
| Exercise 3 | TCPdump | CVE-2017-13028 | 4 hours | ASan, Sanitizers |
| Exercise 4 | LibTIFF | CVE-2016-9297 | 3 hours | Code coverage, LCOV |
| Exercise 5 | Libxml2 | CVE-2017-9048 | 3 hours | Dictionaries, Basic parallelization, Fuzzing command-line arguments |
| Exercise 6 | GIMP | CVE-2016-4994, Bonus bugs | 7 hours | Persistent fuzzing, Fuzzing interactive applications |
| Exercise 7 | VLC media player | CVE-2019-14776 | 6 hours | Partial instrumentation, Fuzzing harness |
| Exercise 8 | Adobe Reader | 8 hours | Fuzzing closed-source applications, QEMU instrumentation | |
| Exercise 9 | 7-Zip | CVE-2016-2334 | 8 hours | WinAFL, Fuzzing Windows Applications |
| Exercise 10 (Final Challenge) | Google Chrome / V8 | CVE-2019-5847 | 8 hours | Fuzzilli, Fuzzing Javascript engines |
Fuzz testing (or fuzzing) is an automated software testing technique that is based on feeding the program with random/mutated input values and monitoring it for exceptions/crashes.
AFL, libFuzzer and HonggFuzz are three of the most successful fuzzers when it comes to real world applications. All three are examples of Coverage-guided evolutionary fuzzers.
Evolutionary: is a metaheuristic approach inspired by evolutionary algorithms, which basically consists in the evolution and mutation of the initial subset (seeds) over time, by using a selection criteria (ex. coverage).
Coverage-guided: To increase the chance of finding new crashes, coverage-guided fuzzers gather and compare code coverage data between different inputs (usually through instrumentation) and pick those inputs which lead to new execution paths.
Simplification of the coverage gathering process of a coverage-guided evolutionary fuzzer
Thanks for their help:
(top 24 of 52)
475 followers · starred Mar 2022
105 followers · starred Aug 2021
203 followers · starred Oct 2024
156 followers · starred Oct 2024





