Creates a comment inside Pull Request with the human-readable summary of changes to the Yarn lock file. Works with every Yarn version (classic and berry).
See the code
Creates a comment inside Pull Request with the human-readable summary of the changes to the yarn.lock file. Works in public and private repositories, offers a degree of customization.
Example below shows the minimal workflow setup, required action input (token) and all the optional inputs (set to theirs default values). If you are happy with the output generated by the action, it's safe to remove all optional inputs.
name: Yarn Lock Changes
on: [pull_request]

jobs:
  yarn_lock_changes:
    runs-on: ubuntu-latest
    # Permission overwrite is required for Dependabot PRs, see "Common issues" section below.
    permissions:
      pull-requests: write
    steps:
      - name: Checkout
        uses: actions/checkout@v6
      - name: Yarn Lock Changes
        # Please use `main` as version before the stable release will be published as `v1`.
        uses: Simek/yarn-lock-changes@main
        with:
          token: ${{ secrets.GITHUB_TOKEN }}
          # Optional inputs, can be deleted safely if you are happy with default values.
          collapsibleThreshold: 25
          failOnDowngrade: false
          path: yarn.lock
          updateComment: true
          groupByType: false
[!note] For Node <22 support, you can change the action version tag in your workflow to
v0.12:- name: Yarn Lock Changes uses: Simek/[email protected]For Node <18 support, you can change the action version tag in your workflow to
v0.11:- name: Yarn Lock Changes uses: Simek/[email protected]
| Input | Required | Default | Description |
|---|---|---|---|
token | Yes | – | Repository GITHUB_TOKEN which allows action to make calls to the GitHub API (Octokit). |
collapsibleThreshold | No | 25 | Number of lock changes, which will result in collapsed comment content, and an addition of changes summary table. |
failOnDowngrade | No | false | WFail the action when a dependency downgrade is detected. Comment will still be posted. |
path | No | yarn.lock | Path to the yarn.lock file in the repository. Default value points to the file at project root. |
updateComment | No | true | Update the comment on each new commit. If value is set to false, bot will post a new comment on each change. |
groupByType | No | false | Group the dependencies in the comment table by the change type. |

collapsibleThreshold has been reached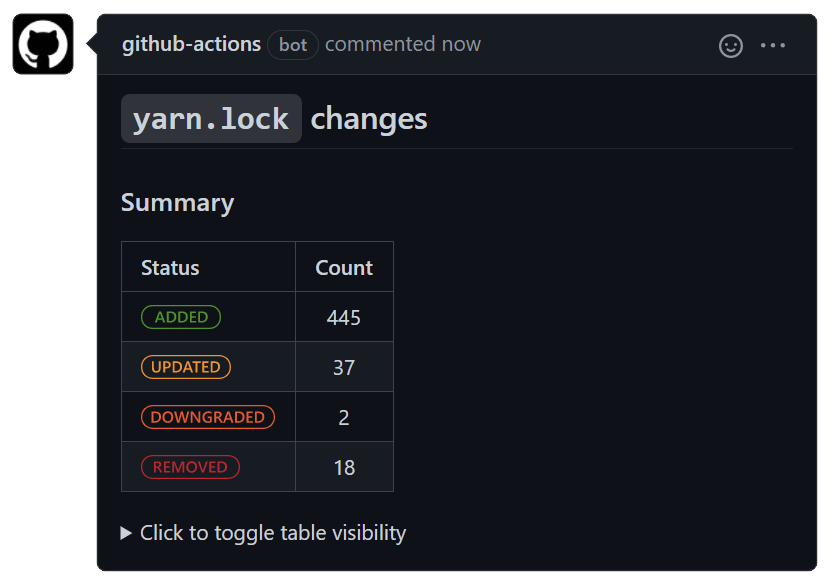
Due to the security reasons from March 1st, 2021 workflow runs that are triggered by Dependabot have permissions reduced by default:
To ensure that sufficient permissions for this action are always granted, you will need to add permissions entry to the job which runs yarn-lock-changes:
jobs:
  ...:
    runs-on: ...
    #####
    permissions:
      pull-requests: write
    #####
    steps: ...
After one of the GitHub Actions security breaches GitHub decided to trim down the default permission set for actions running in private repositories.
If you are trying to run action with default setup in the private repository, you will see the following error during checkout step:
remote: Repository not found.
Error: fatal: repository 'https://github.com/<your_user>/<your_repo>/' not found
Error: The process '/usr/bin/git' failed with exit code 128
This means that you will need to add the following permissions entry to the job which runs checkout:
jobs:
  ...:
    runs-on: ...
    #####
    permissions:
      contents: read
    #####
    steps: ...
If you would like to learn a little bit more about this problem, you can visit this issue in the GitHub Checkout Action repository:
To run action in the debug mode you need to add the ACTIONS_STEP_DEBUG repository secret and set it to true, as stated in the GitHub documentation.
Then additional information which might be useful for the users when debugging the issues will be available in the action output, prefixed by ##[debug].
450 followers · starred Oct 2024
5,285 followers · starred May 2021
4,533 followers · starred Apr 2021
282 followers · starred Jul 2022
Creates a comment inside Pull Request with the human-readable summary of changes to the Yarn lock file. Works with every Yarn version (classic and berry).
See the code
Creates a comment inside Pull Request with the human-readable summary of the changes to the yarn.lock file. Works in public and private repositories, offers a degree of customization.
Example below shows the minimal workflow setup, required action input (token) and all the optional inputs (set to theirs default values). If you are happy with the output generated by the action, it's safe to remove all optional inputs.
name: Yarn Lock Changes
on: [pull_request]

jobs:
  yarn_lock_changes:
    runs-on: ubuntu-latest
    # Permission overwrite is required for Dependabot PRs, see "Common issues" section below.
    permissions:
      pull-requests: write
    steps:
      - name: Checkout
        uses: actions/checkout@v6
      - name: Yarn Lock Changes
        # Please use `main` as version before the stable release will be published as `v1`.
        uses: Simek/yarn-lock-changes@main
        with:
          token: ${{ secrets.GITHUB_TOKEN }}
          # Optional inputs, can be deleted safely if you are happy with default values.
          collapsibleThreshold: 25
          failOnDowngrade: false
          path: yarn.lock
          updateComment: true
          groupByType: false
[!note] For Node <22 support, you can change the action version tag in your workflow to
v0.12:- name: Yarn Lock Changes uses: Simek/[email protected]For Node <18 support, you can change the action version tag in your workflow to
v0.11:- name: Yarn Lock Changes uses: Simek/[email protected]
| Input | Required | Default | Description |
|---|---|---|---|
token | Yes | – | Repository GITHUB_TOKEN which allows action to make calls to the GitHub API (Octokit). |
collapsibleThreshold | No | 25 | Number of lock changes, which will result in collapsed comment content, and an addition of changes summary table. |
failOnDowngrade | No | false | WFail the action when a dependency downgrade is detected. Comment will still be posted. |
path | No | yarn.lock | Path to the yarn.lock file in the repository. Default value points to the file at project root. |
updateComment | No | true | Update the comment on each new commit. If value is set to false, bot will post a new comment on each change. |
groupByType | No | false | Group the dependencies in the comment table by the change type. |
collapsibleThreshold has been reached
Due to the security reasons from March 1st, 2021 workflow runs that are triggered by Dependabot have permissions reduced by default:
To ensure that sufficient permissions for this action are always granted, you will need to add permissions entry to the job which runs yarn-lock-changes:
jobs:
  ...:
    runs-on: ...
    #####
    permissions:
      pull-requests: write
    #####
    steps: ...
After one of the GitHub Actions security breaches GitHub decided to trim down the default permission set for actions running in private repositories.
If you are trying to run action with default setup in the private repository, you will see the following error during checkout step:
remote: Repository not found.
Error: fatal: repository 'https://github.com/<your_user>/<your_repo>/' not found
Error: The process '/usr/bin/git' failed with exit code 128
This means that you will need to add the following permissions entry to the job which runs checkout:
jobs:
  ...:
    runs-on: ...
    #####
    permissions:
      contents: read
    #####
    steps: ...
If you would like to learn a little bit more about this problem, you can visit this issue in the GitHub Checkout Action repository:
To run action in the debug mode you need to add the ACTIONS_STEP_DEBUG repository secret and set it to true, as stated in the GitHub documentation.
Then additional information which might be useful for the users when debugging the issues will be available in the action output, prefixed by ##[debug].
450 followers · starred Oct 2024
5,285 followers · starred May 2021
4,533 followers · starred Apr 2021
282 followers · starred Jul 2022