
JavaScript security CLI that allow you to deeply analyze the dependency tree of a given package or local Node.js project.
JavaScript
385
1,011 commits
updated Sep 21, 2026
README
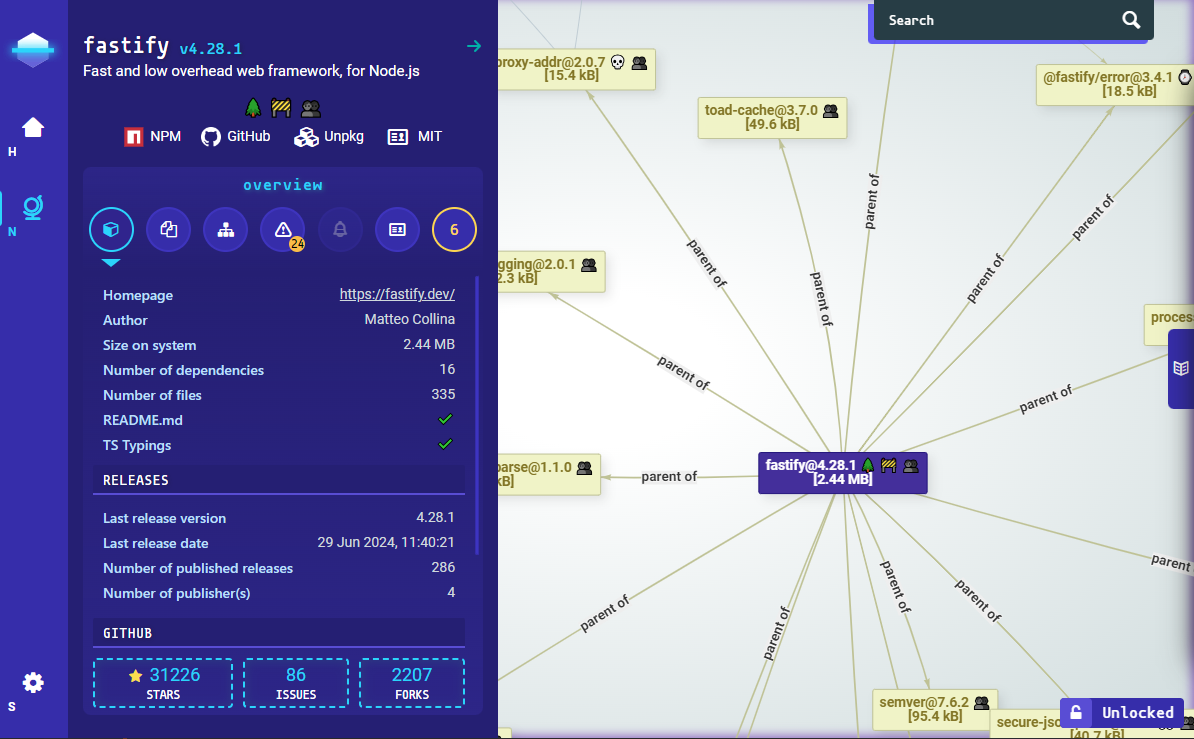


A Node.js tool that performs a static and deep analysis of a package's dependency tree: AST-based scanning for malicious or unsafe patterns, npm registry metadata, license conformance, vulnerability aggregation (GitHub Advisory, Sonatype, Snyk) and OpenSSF Scorecard, all rendered through an interactive dependency graph.
💃 Getting Started
$ npm install @nodesecure/cli -g
$ nsecure auto express
This repository is a monorepo. The @nodesecure/cli package, along with its full feature list, command documentation, configuration and FAQ, lives in the workspaces/cli workspace — head there for everything about installing and using the CLI.
📦 Workspaces
| name | package and link |
|---|---|
| cli | @nodesecure/cli |
| documentation-ui | @nodesecure/documentation-ui |
| vis-network | @nodesecure/vis-network |
| size-satisfies | @nodesecure/size-satisfies |
| server | @nodesecure/server |
| cache | @nodesecure/cache |
These packages are available in the Node Package Repository and can be easily installed with npm or yarn, for example:
$ npm i @nodesecure/documentation-ui
# or
$ yarn add @nodesecure/documentation-ui
🙏 Contributing
If you are a developer looking to contribute to the project, please first read our CONTRIBUTING guide (Code of Conduct, first-contributor guide, Developer's Certificate of Origin, Discord).
Local Setup
$ git clone https://github.com/NodeSecure/cli.git
$ cd cli

$ npm install
# bundle/compile front-end assets for every workspace
$ npm run build
[!IMPORTANT] Restart
npm run buildwhen modifying files under a workspace's public/front-end assets folder.
Once you have finished your development, check that the tests (and linter) are still good by running the following script:
$ npm test
[!CAUTION] If you add a feature, try adding tests for it along.
Publishing package and SLSA
The @nodesecure/cli package is published on NPM with provenance, ensuring that this project is compliant with SLSA Level 3 standards. The build and publication process is managed through the GitHub npm-provenance.yml workflow, which is automatically triggered upon the creation of a new release.
To create a local version of the package using npm and Git, follow these commands:
$ npm version [patch | minor | major]
$ git commit -am "chore: x.x.x"
$ git push origin master --tags
These commands will increment the package version, commit the changes, and push them along with the tags to the repository.
Contributors ✨

Thanks goes to these wonderful people (emoji key):


This project follows the all-contributors specification. Contributions of any kind welcome!
License
MIT
Contributors
(top 30 of 38)


Similar repos


Languages
JavaScript
76.4%
TypeScript
14.6%
CSS
6.7%
HTML
2.3%
JavaScript security CLI that allow you to deeply analyze the dependency tree of a given package or local Node.js project.
JavaScript
385
1,011 commits
updated Sep 21, 2026
README
A Node.js tool that performs a static and deep analysis of a package's dependency tree: AST-based scanning for malicious or unsafe patterns, npm registry metadata, license conformance, vulnerability aggregation (GitHub Advisory, Sonatype, Snyk) and OpenSSF Scorecard, all rendered through an interactive dependency graph.
💃 Getting Started
$ npm install @nodesecure/cli -g
$ nsecure auto express
This repository is a monorepo. The @nodesecure/cli package, along with its full feature list, command documentation, configuration and FAQ, lives in the workspaces/cli workspace — head there for everything about installing and using the CLI.
📦 Workspaces
| name | package and link |
|---|---|
| cli | @nodesecure/cli |
| documentation-ui | @nodesecure/documentation-ui |
| vis-network | @nodesecure/vis-network |
| size-satisfies | @nodesecure/size-satisfies |
| server | @nodesecure/server |
| cache | @nodesecure/cache |
These packages are available in the Node Package Repository and can be easily installed with npm or yarn, for example:
$ npm i @nodesecure/documentation-ui
# or
$ yarn add @nodesecure/documentation-ui
🙏 Contributing
If you are a developer looking to contribute to the project, please first read our CONTRIBUTING guide (Code of Conduct, first-contributor guide, Developer's Certificate of Origin, Discord).
Local Setup
$ git clone https://github.com/NodeSecure/cli.git
$ cd cli

$ npm install
# bundle/compile front-end assets for every workspace
$ npm run build
[!IMPORTANT] Restart
npm run buildwhen modifying files under a workspace's public/front-end assets folder.
Once you have finished your development, check that the tests (and linter) are still good by running the following script:
$ npm test
[!CAUTION] If you add a feature, try adding tests for it along.
Publishing package and SLSA
The @nodesecure/cli package is published on NPM with provenance, ensuring that this project is compliant with SLSA Level 3 standards. The build and publication process is managed through the GitHub npm-provenance.yml workflow, which is automatically triggered upon the creation of a new release.
To create a local version of the package using npm and Git, follow these commands:
$ npm version [patch | minor | major]
$ git commit -am "chore: x.x.x"
$ git push origin master --tags
These commands will increment the package version, commit the changes, and push them along with the tags to the repository.
Contributors ✨
Thanks goes to these wonderful people (emoji key):
This project follows the all-contributors specification. Contributions of any kind welcome!
License
MIT
Similar repos
Contributors
(top 30 of 38)
Languages
JavaScript
76.4%
TypeScript
14.6%
CSS
6.7%
HTML
2.3%