
| Language: English | 日本語 |


|
Kubernetes History Inspector (KHI) is a rich log visualization tool for Kubernetes clusters. KHI transforms vast quantities of logs into an interactive, comprehensive timeline view. This makes it an invaluable tool for troubleshooting complex issues that span multiple components within your Kubernetes clusters. Also, KHI is agentless, allowing anyone to access its features without a complicated process.
| Timeline view | Topology view |
|---|---|
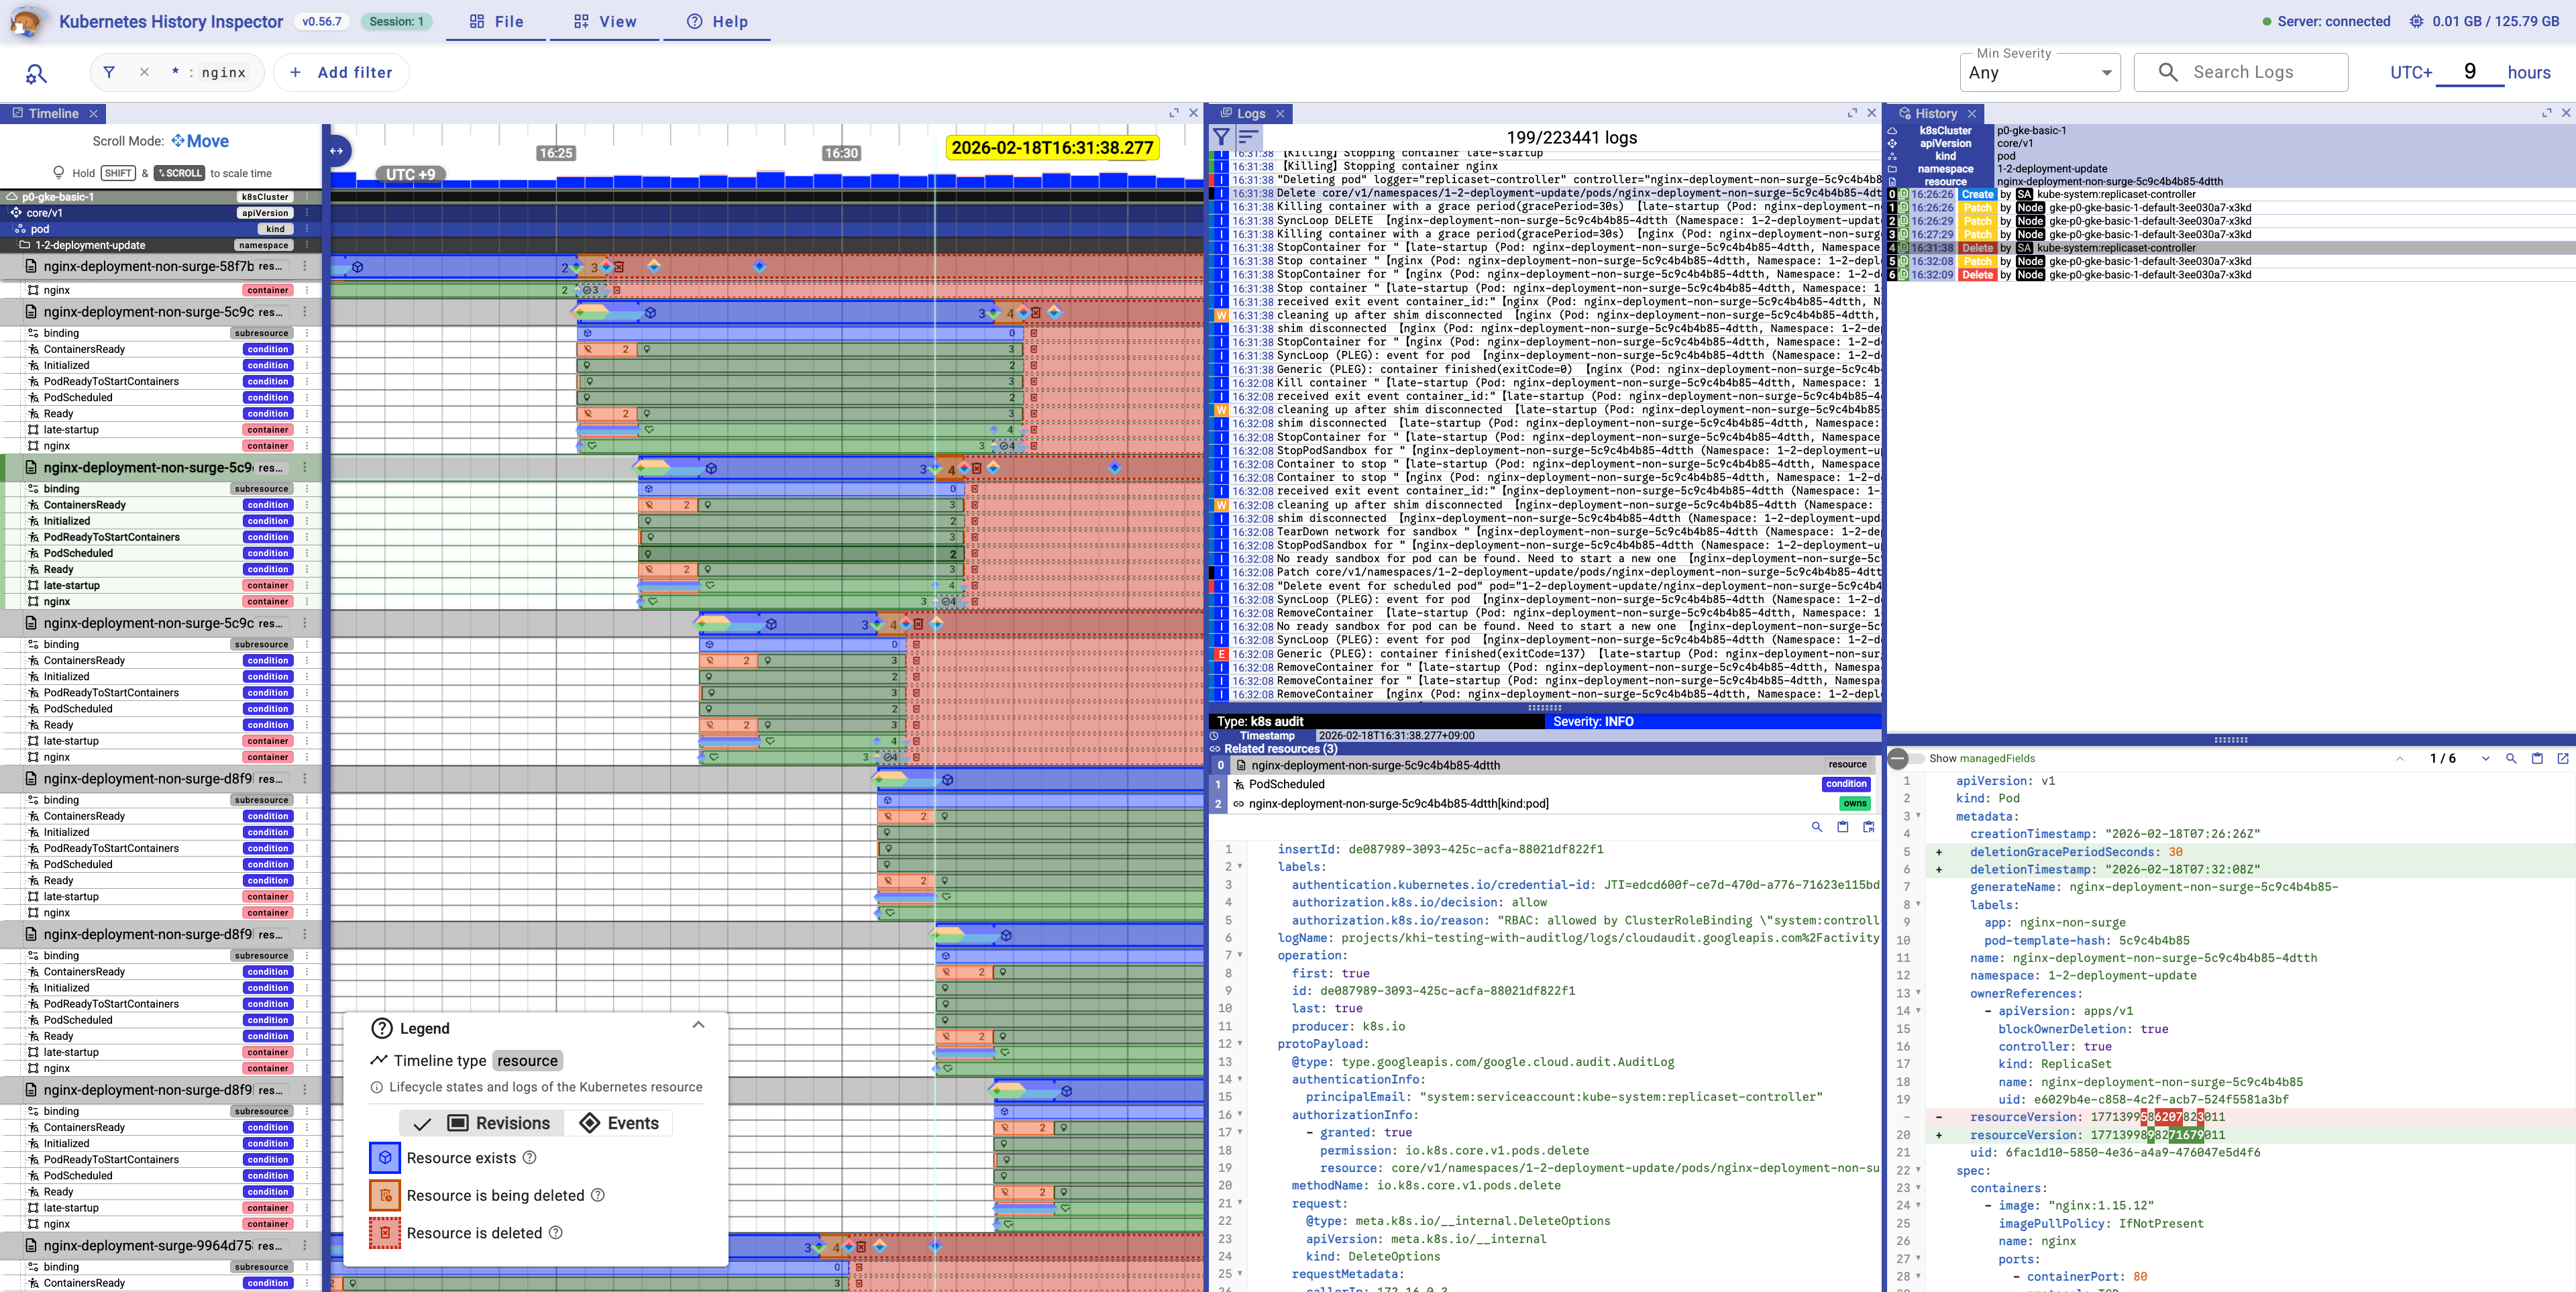
Timeline view visualizes resource status change timings with timeline charts and manifest diffs from Kubernetes audit logs. |
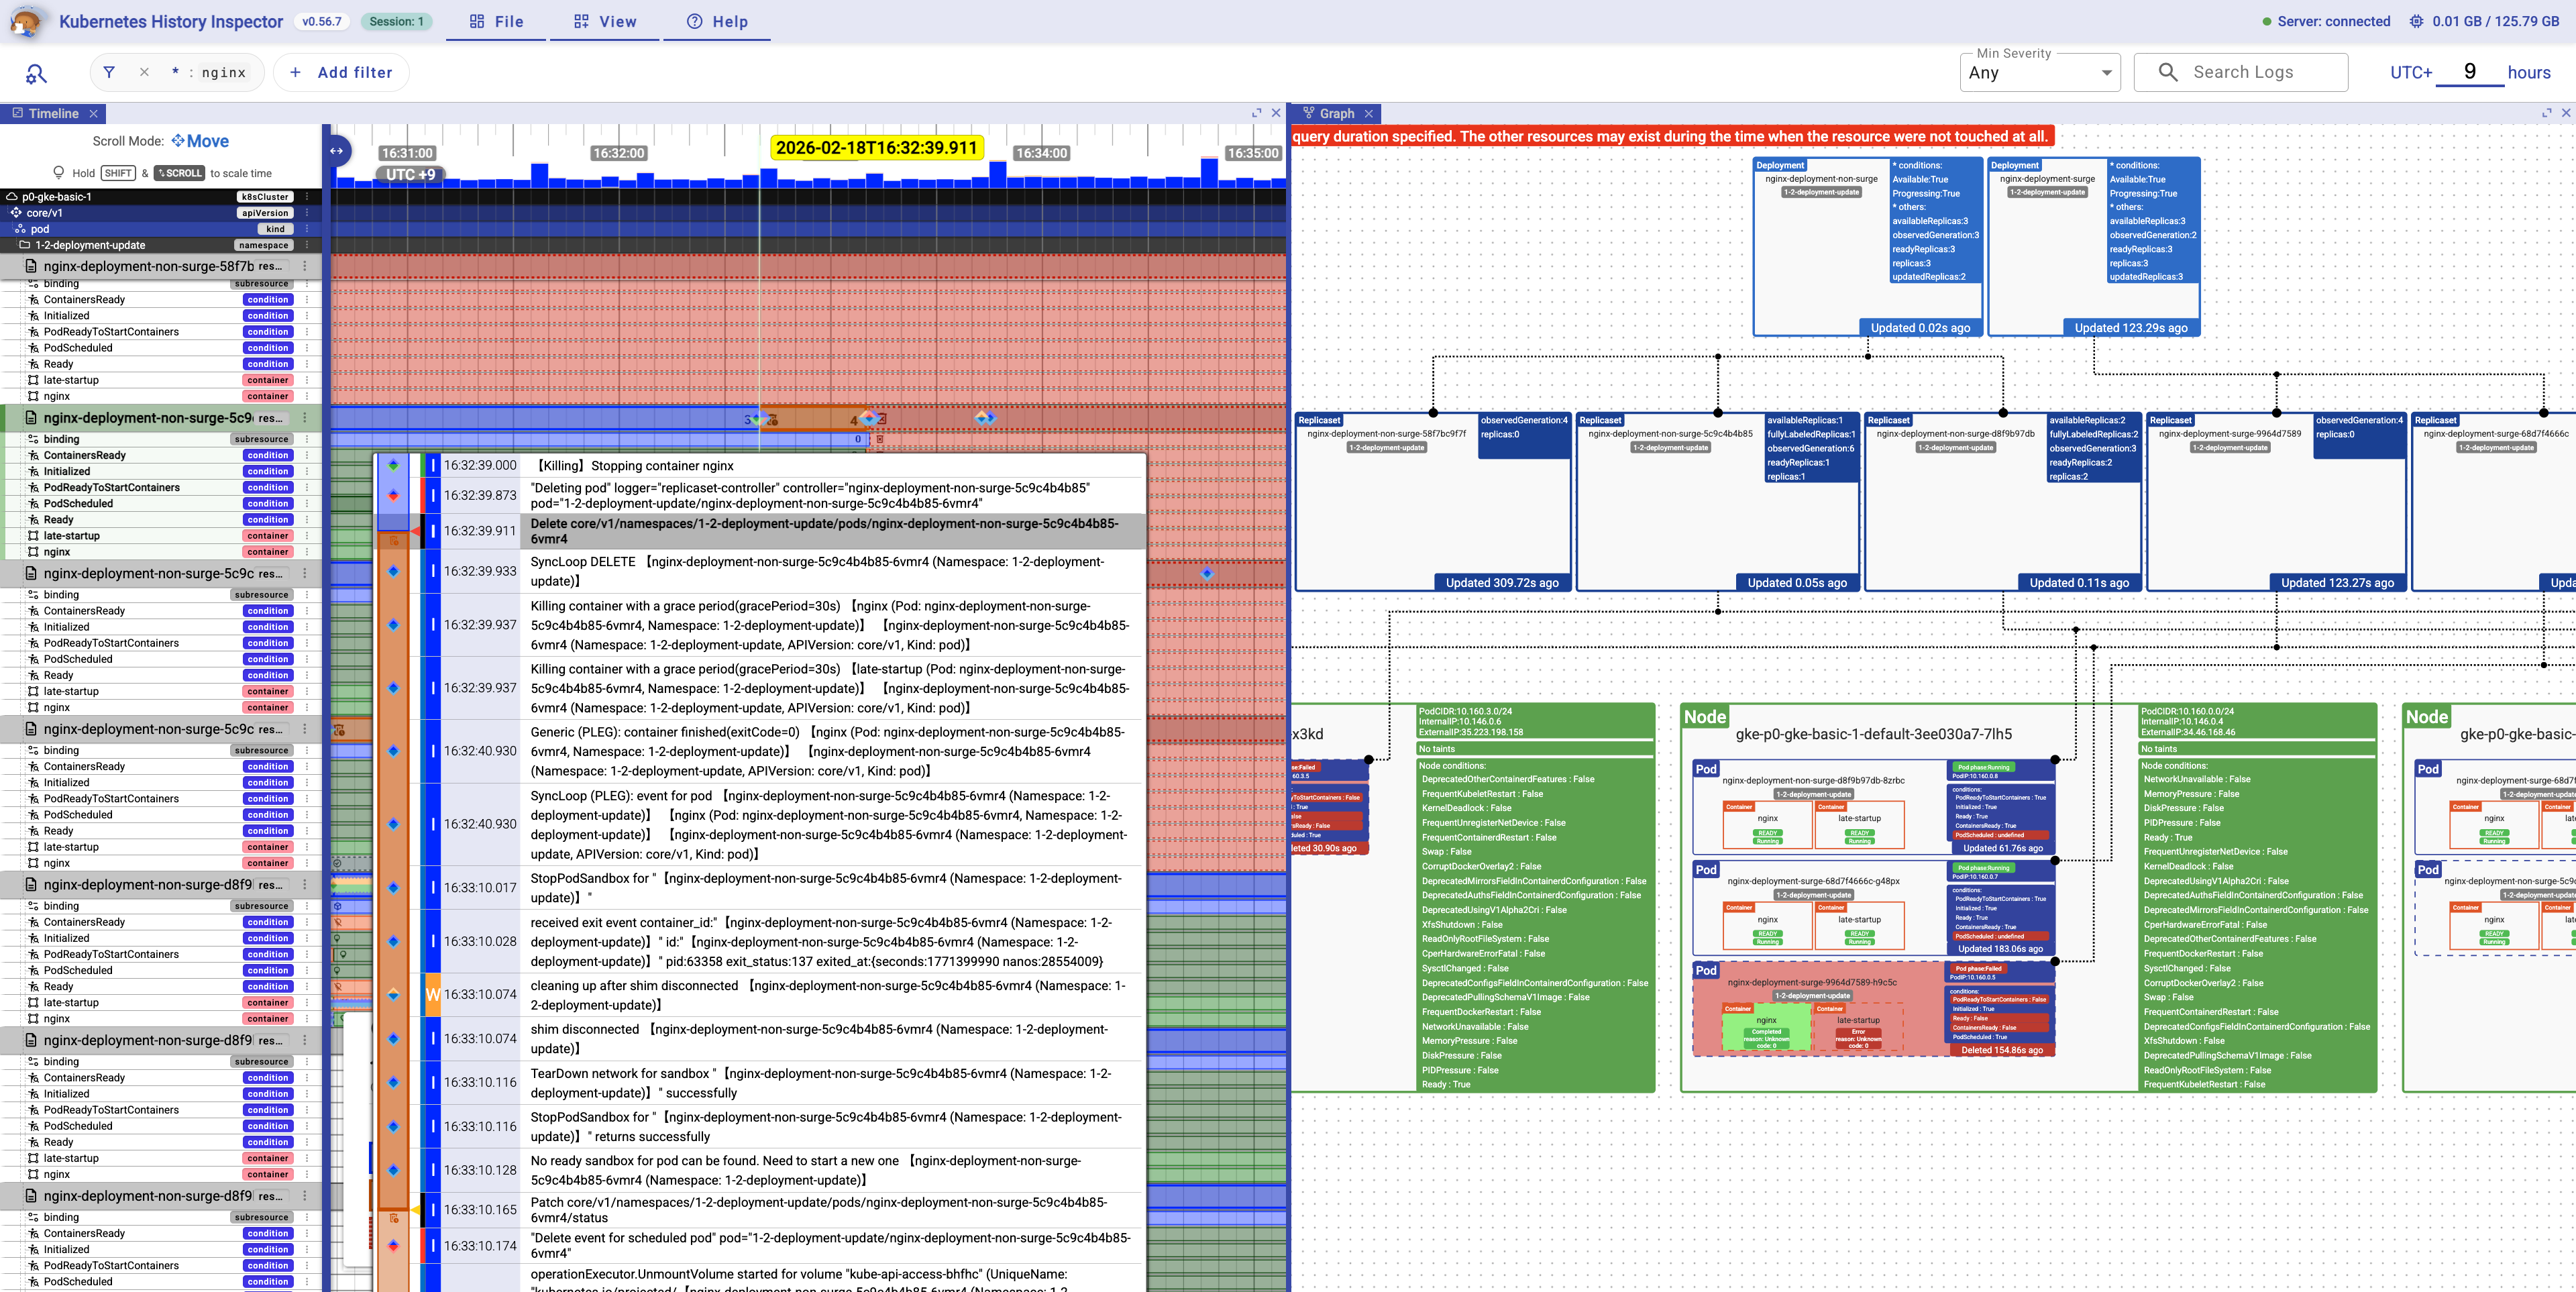
Topology view visualizes relationships among Kubernetes resources, solely from kube-apiserver audit logs. |
The easiest way to try KHI is using Cloud Shell, where the metadata server is available without requiring initial credential setup.
Open Cloud Shell
Run the following command:
docker run -p 127.0.0.1:8080:8080 gcr.io/kubernetes-history-inspector/release:latest
Click the link http://localhost:8080 on the terminal and start working with KHI!
If you want to run KHI in an environment where the metadata server is not available, you can use Application Default Credentials (ADC) by mounting your ADC file from your host filesystem to the container.
gcloud auth application-default login
docker run \
 -p 127.0.0.1:8080:8080 \
 -v ~/.config/gcloud/application_default_credentials.json:/root/.config/gcloud/application_default_credentials.json:ro \
 gcr.io/kubernetes-history-inspector/release:latest
gcloud auth application-default login
docker run `
-p 127.0.0.1:8080:8080 `
-v $env:APPDATA\gcloud\application_default_credentials.json:/root/.config/gcloud/application_default_credentials.json:ro `
gcr.io/kubernetes-history-inspector/release:latest
Google Cloud
Other
Google Cloud
Other
docker command[!IMPORTANT] We only test KHI on the latest version of Google Chrome. KHI may work with other browsers, but we do not provide support if it does not.
Read Google Cloud Permissions & Configuration Guide.
Read Using KHI with OSS Kubernetes Clusters - Example with Loki.
Please refer to the User Guide for detailed usage.
If you'd like to contribute to the project KHI, read Contribution Guide and then follow Development Guide
Please note that this tool is not an officially supported Google Cloud product. If you find any issues and have a feature request, file a Github issue on this repository and we are happy to check them on best-effort basis.
[!IMPORTANT] Do not expose KHI port on the internet. KHI itself is not providing any authentication or authorization features and KHI is intended to be accessed from its local user.
(top 24 of 62)
599 followers · starred Jan 2025
885 followers · starred Jan 2025
740 followers · starred Feb 2025
883 followers · starred Jan 2025
| Language: English | 日本語 |
|
|
Kubernetes History Inspector (KHI) is a rich log visualization tool for Kubernetes clusters. KHI transforms vast quantities of logs into an interactive, comprehensive timeline view. This makes it an invaluable tool for troubleshooting complex issues that span multiple components within your Kubernetes clusters. Also, KHI is agentless, allowing anyone to access its features without a complicated process.
| Timeline view | Topology view |
|---|---|
|
Timeline view visualizes resource status change timings with timeline charts and manifest diffs from Kubernetes audit logs. |
Topology view visualizes relationships among Kubernetes resources, solely from kube-apiserver audit logs. |
The easiest way to try KHI is using Cloud Shell, where the metadata server is available without requiring initial credential setup.
Open Cloud Shell
Run the following command:
docker run -p 127.0.0.1:8080:8080 gcr.io/kubernetes-history-inspector/release:latest
Click the link http://localhost:8080 on the terminal and start working with KHI!
If you want to run KHI in an environment where the metadata server is not available, you can use Application Default Credentials (ADC) by mounting your ADC file from your host filesystem to the container.
gcloud auth application-default login
docker run \
 -p 127.0.0.1:8080:8080 \
 -v ~/.config/gcloud/application_default_credentials.json:/root/.config/gcloud/application_default_credentials.json:ro \
 gcr.io/kubernetes-history-inspector/release:latest
gcloud auth application-default login
docker run `
-p 127.0.0.1:8080:8080 `
-v $env:APPDATA\gcloud\application_default_credentials.json:/root/.config/gcloud/application_default_credentials.json:ro `
gcr.io/kubernetes-history-inspector/release:latest
Google Cloud
Other
Google Cloud
Other
docker command[!IMPORTANT] We only test KHI on the latest version of Google Chrome. KHI may work with other browsers, but we do not provide support if it does not.
Read Google Cloud Permissions & Configuration Guide.
Read Using KHI with OSS Kubernetes Clusters - Example with Loki.
Please refer to the User Guide for detailed usage.
If you'd like to contribute to the project KHI, read Contribution Guide and then follow Development Guide
Please note that this tool is not an officially supported Google Cloud product. If you find any issues and have a feature request, file a Github issue on this repository and we are happy to check them on best-effort basis.
[!IMPORTANT] Do not expose KHI port on the internet. KHI itself is not providing any authentication or authorization features and KHI is intended to be accessed from its local user.
(top 24 of 62)
599 followers · starred Jan 2025
885 followers · starred Jan 2025
740 followers · starred Feb 2025
883 followers · starred Jan 2025



